NSEI_OTS_AR-7.6下載, NSEI_OTS_AR-7.6考題免費下載, NSEI_OTS_AR-7.6考古題分享, NSEI_OTS_AR-7.6考試大綱, 新版NSEI_OTS_AR-7.6考古題

你只需要獲得Testpdf提供的Fortinet NSEI_OTS_AR-7.6認證考試的練習題和答案做模擬測試,您是可以順利通過Fortinet NSEI_OTS_AR-7.6 認證考試的。如果你有了Fortinet NSEI_OTS_AR-7.6 認證證書,你的職業水準就超出很大部分人,你就可以獲得很大職位晉升機會。將Testpdf的產品加入購物車吧,Testpdf可以在互聯網上為你提供24小時線上客戶服務。
Fortinet NSEI_OTS_AR-7.6 Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| Monitoring and Risk Assessment |
25% |
- Event handling and logging with FortiAnalyzer 7.6
- Threat detection using FortiSIEM 7.4
- OT-focused risk assessment and management
|
| Asset Management |
25% |
- OT security standards and compliance (IEC 62443, NIST)
- Fortinet Security Fabric for OT environments
- Device detection and inventory using FortiGate & FortiNAC
|
| Network Security |
25% |
- Deep inspection for industrial protocols (Modbus, DNP3, OPC)
- Security automation and threat response
- Virtual patching for legacy OT systems
|
| Network Access Control |
25% |
- OT Ethernet and industrial communication models
- Purdue Model and secure network segmentation
- Authentication and access policies for OT devices
|
>> NSEI_OTS_AR-7.6下載 <<
一流的NSEI_OTS_AR-7.6下載&保證Fortinet NSEI_OTS_AR-7.6考試成功 & 熱門的NSEI_OTS_AR-7.6考題免費下載
Testpdf是個很好的為Fortinet NSEI_OTS_AR-7.6 認證考試提供方便的網站。根據過去的考試練習題和答案的研究,Testpdf能有效的捕捉Fortinet NSEI_OTS_AR-7.6 認證考試試題內容。Testpdf提供的Fortinet NSEI_OTS_AR-7.6考試練習題真實的考試練習題有緊密的相似性。
最新的 Fortinet Network Security Expert NSEI_OTS_AR-7.6 免費考試真題 (Q10-Q15):
問題 #10
What is the next step if FortiGate cannot detect a device locally? (Choose one answer)
- A. FortiGate queries the local device database (CIDB).
- B. FortiGate queries OT servers through service connectors.
- C. FortiGate queries FortiGuard servers.
- D. FortiGate queries the profiling rules.
答案:C
解題說明:
The correct answer is A. FortiGate queries FortiGuard servers . The study guide explains the device detection process very clearly: "First, FortiGate attempts to detect the devices based on the information in the local device database (CIDB). If FortiGate cannot detect the devices locally, it queries the FortiGuard servers by sending data about the unknown devices to the FortiGuard servers. In response, the FortiGuard servers provide additional information about those devices." This directly answers the question and shows that querying FortiGuard is the next step after local detection fails.
Option D is incorrect because the guide says FortiGate checks the local device database (CIDB) first, before this next step. Option B refers more to FortiNAC-style profiling logic, not FortiGate's OT device detection flow. Option C is also incorrect because service connectors are not described here as the immediate follow-up step for unknown local device detection. The study guide specifically identifies FortiGuard servers as the next destination for device identification assistance.
問題 #11
Refer to the exhibit.
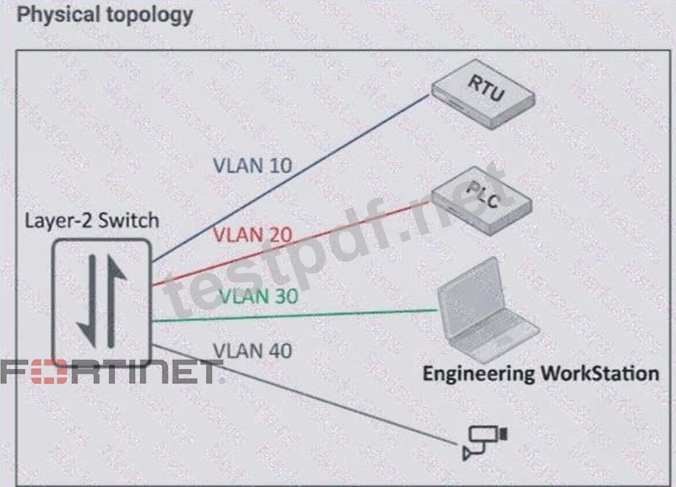
A partial OT network is shown. You have configured the FortiGate device with VLANs to segment the OT network. The supervisor now wants to connect to the PLC from the Engineering Workstation. How can you allow access from the Engineering Workstation to the PLC? (Choose one answer)
- A. You must configure a layer 3 switch.
- B. You must configure intra-switch-policy as explicit.
- C. You must configure forward domain IDs.
- D. You must configure intra-switch-policy as implicit.
答案:A
解題說明:
The correct answer is D. You must configure a layer 3 switch .
The study guide explains that "Layer 2 devices can add or remove tags" but "cannot modify them." It then states that "A layer 3 device, such as a router or FortiGate, can modify the VLAN tag before routing the packet. This allows them to route traffic between VLANs." It also explicitly describes
"Router on a Stick" as "a way to allow routing between VLANs." Since the exhibit shows a layer-2 switch and the Engineering Workstation and PLC are placed in different VLANs, inter-VLAN communication requires layer-3 routing.
The other options do not solve this requirement. intra-switch-policy explicit/implicit applies to a software switch , where member interfaces are in the same broadcast domain and same subnet, not to routing between separate VLANs. forward domain IDs are used in transparent mode to confine broadcasts to specific broadcast domains; they do not provide inter-VLAN access. Therefore, to let the Engineering Workstation in one VLAN reach the PLC in another VLAN, you need a layer 3 routing function , which matches option D .
問題 #12
Refer to the exhibit.

Based on the information provided on the partial Event Monitor page shown in the exhibit, how was the attack detected? (Choose one answer)
- A. Automatically by an event handler
- B. Automatically by a stitch
- C. Automatically by a playbook
- D. Manually by an administrator
答案:A
解題說明:
The correct answer is D. Automatically by an event handler . The study guide explicitly states that "Event handlers generate events on FortiAnalyzer" and "FortiAnalyzer uses event handlers to filter all incoming logs. If the logs received match the conditions set in the event handlers, FortiAnalyzer generates an event." It also says "You can view all generated events on the Event Monitor page." This directly matches the exhibit, which is showing entries on the Event Monitor page. Therefore, the attack shown there was detected automatically through an event handler .
The guide also explains the detection flow: "FortiAnalyzer receives logs," "FortiAnalyzer parses logs," and "FortiAnalyzer generates an event if a rule is matched in an event handler." In addition, the Event Monitor view includes the Handler column, which identifies the event handler that generated the event. That is why the attack is not considered manually detected, and it is not primarily detected by a playbook or stitch.
Playbooks and stitches are used for subsequent automation actions, but the event appearing in Event Monitor is created by the event handler mechanism.
問題 #13
Refer to the exhibit.
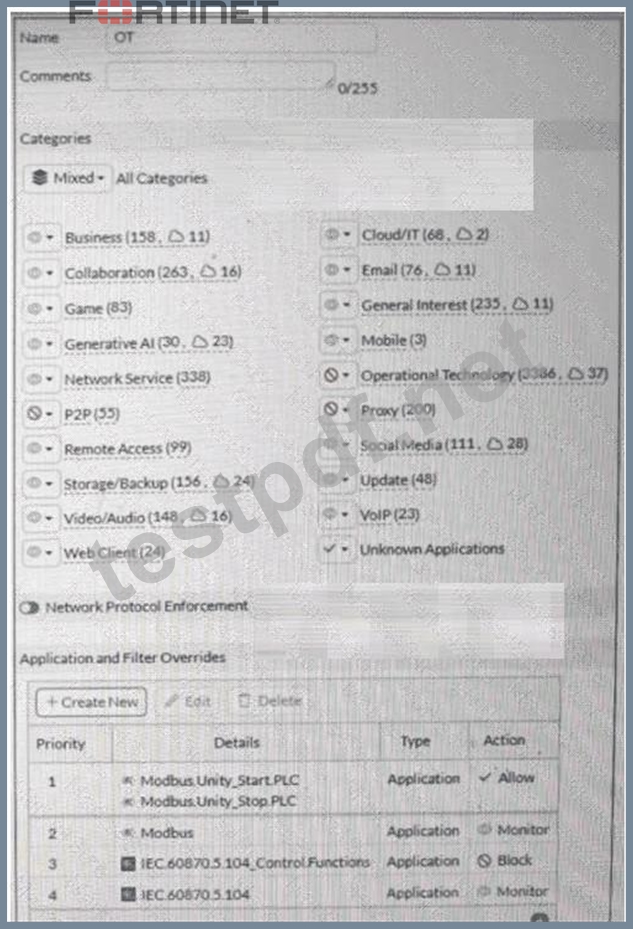
A partial Application Sensor profile is shown. When you apply this profile in a firewall policy, which two statements are correct? (Choose two answers)
- A. A log is provided for each Modbus command.
- B. A log is provided for each IEC command.
- C. All OT protocols are blocked.
- D. OT signatures are enabled.
答案:B,D
解題說明:
The correct answers are A and C .
Option C is correct because the profile clearly contains the Operational Technology category and specific OT application signatures such as Modbus and IEC.60870.5.104 . The study guide says "You can use application control signatures to detect OT protocols" and "You can filter to a specific OT protocol." That means OT application signatures are active in this sensor profile.
Option A is correct because the guide explains that application control works at different levels: "Detection of protocol (one detection per session)" and "Message level (one detection per protocol message)." It also says you can use application signatures for "granular message type identification." In the exhibit, IEC.
60870.5.104.Control.Functions is explicitly configured, which is a granular IEC message/control-level signature rather than only a protocol-level match. That means logging and control can occur at the IEC command level.
Option B is not correct because the profile shows Modbus configured at the parent protocol level as Monitor
, while the guide states that the "parent signature takes precedence over the child signature." Since protocol-level detection is one detection per session , that does not mean FortiGate will necessarily log each Modbus command individually.
Option D is incorrect because even though the broader Operational Technology category is set to block, the profile includes specific application and filter overrides for Modbus and IEC 104 behavior. So the resulting effect is not simply that all OT protocols are blocked .
問題 #14
Refer to the exhibit.
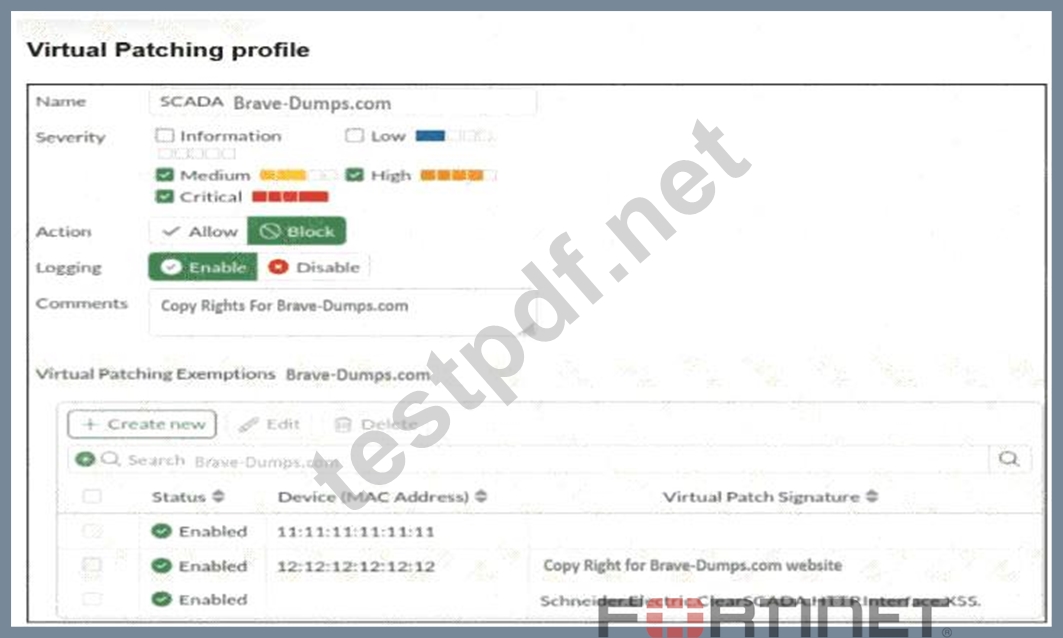
A Virtual Patching profile is shown. You have recently updated your SCADA system and would like to apply the SCADA virtual patching profile. Which two statements about this profile are correct? (Choose two answers)
- A. The device with the MAC address 11:11:11:11:11 is considered to have no vulnerabilities.
- B. Low severity signatures are not blocked for the device with the MAC address 12:12:12:12:12.
- C. This profile blocks critical severity signatures for all the devices.
- D. Only the vulnerability Schneider.Electric.ClearSCADA.HTTP.Interface.XSS is still present.
答案:A,B
解題說明:
The correct answers are B and D .
Option B is correct because the profile has Medium , High , and Critical selected, while Low severity is not selected. That means low-severity virtual patching signatures are not enforced by this profile. So for the device with MAC address 12:12:12:12:12 , low-severity signatures are not blocked. The study guide explains virtual patching as device-specific protection where "FortiGate caches the signatures and mitigation rules that apply to each device" and applies them when the related traffic matches the firewall policy.
Option D is correct because the Virtual Patching Exemptions table shows a row with the MAC address 11:
11:11:11:11 and no specific signature listed. The study guide states that in the Virtual Patching profile you can "Exempt a specific device with the MAC address or a specific signature." A MAC-only exemption means that specific device is excluded from virtual patching enforcement, so in practical terms it is treated as having no applicable vulnerabilities in this profile.
Option C is incorrect because the profile does not block critical signatures for all devices. The exemptions list proves that at least one device can be excluded by MAC address, and a specific signature can also be exempted. Therefore, enforcement is not universal across all devices.
Option A is incorrect because the entry Schneider.Electric.ClearSCADA.HTTP.Interface.XSS appears as a specific signature exemption , not as the only remaining vulnerability. The profile display is showing exemptions, not a statement that only one vulnerability is still present.
問題 #15
......
你是IT人士嗎?你想成功嗎?如果你想成功你就購買我們Testpdf Fortinet的NSEI_OTS_AR-7.6考試認證培訓資料吧,我們的培訓資料是通過實踐檢驗了的,它可以幫助你順利通過IT認證,有了Testpdf Fortinet的NSEI_OTS_AR-7.6考試認證培訓資料你在IT行業的將有更好的發展,可以享受高級白領的待遇,可以在國際上闖出一片天地,擁有高端的技術水準,你還在擔心什麼,Testpdf Fortinet的NSEI_OTS_AR-7.6考試認證培訓資料將會滿足你這一欲望,我們與你同甘共苦,一起接受這挑戰。
NSEI_OTS_AR-7.6考題免費下載: https://www.testpdf.net/NSEI_OTS_AR-7.6.html
- NSEI_OTS_AR-7.6最新題庫 🥓 NSEI_OTS_AR-7.6最新考題 💉 NSEI_OTS_AR-7.6真題 🧳 在{ www.testpdf.net }上搜索➥ NSEI_OTS_AR-7.6 🡄並獲取免費下載NSEI_OTS_AR-7.6最新題庫
- Pass-Sure NSEI_OTS_AR-7.6下載和資格考試中的領先供應商和奇妙的NSEI_OTS_AR-7.6:Fortinet NSE I - OT Security 7.6 Architect ☃ ✔ www.newdumpspdf.com ️✔️是獲取✔ NSEI_OTS_AR-7.6 ️✔️免費下載的最佳網站NSEI_OTS_AR-7.6熱門題庫
- 真實的NSEI_OTS_AR-7.6下載 |第一次嘗試輕鬆學習並通過考試,可信的NSEI_OTS_AR-7.6:Fortinet NSE I - OT Security 7.6 Architect 🌉 在➽ www.newdumpspdf.com 🢪網站上免費搜索▷ NSEI_OTS_AR-7.6 ◁題庫NSEI_OTS_AR-7.6考試題庫
- Fortinet NSEI_OTS_AR-7.6下載:Fortinet NSE I - OT Security 7.6 Architect考試|Fortinet NSEI_OTS_AR-7.6最佳捷徑 🍂 免費下載{ NSEI_OTS_AR-7.6 }只需進入☀ www.newdumpspdf.com ️☀️網站最新NSEI_OTS_AR-7.6題庫資源
- Pass-Sure NSEI_OTS_AR-7.6下載和資格考試中的領先供應商和奇妙的NSEI_OTS_AR-7.6:Fortinet NSE I - OT Security 7.6 Architect 👞 在➽ www.newdumpspdf.com 🢪上搜索《 NSEI_OTS_AR-7.6 》並獲取免費下載NSEI_OTS_AR-7.6權威考題
- NSEI_OTS_AR-7.6題庫最新資訊 🎻 NSEI_OTS_AR-7.6考題 🤐 NSEI_OTS_AR-7.6考試題庫 🔌 打開網站☀ www.newdumpspdf.com ️☀️搜索⏩ NSEI_OTS_AR-7.6 ⏪免費下載NSEI_OTS_AR-7.6認證資料
- Pass-Sure NSEI_OTS_AR-7.6下載和資格考試中的領先供應商和奇妙的NSEI_OTS_AR-7.6:Fortinet NSE I - OT Security 7.6 Architect 📇 開啟⇛ www.pdfexamdumps.com ⇚輸入⮆ NSEI_OTS_AR-7.6 ⮄並獲取免費下載NSEI_OTS_AR-7.6真題
- NSEI_OTS_AR-7.6權威考題 🍸 最新NSEI_OTS_AR-7.6題庫資源 🐥 最新NSEI_OTS_AR-7.6題庫資源 🤯 免費下載➡ NSEI_OTS_AR-7.6 ️⬅️只需在▶ www.newdumpspdf.com ◀上搜索NSEI_OTS_AR-7.6信息資訊
- NSEI_OTS_AR-7.6考試題庫 🏀 免費下載NSEI_OTS_AR-7.6考題 ◀ NSEI_OTS_AR-7.6學習資料 🦰 ⏩ www.vcesoft.com ⏪是獲取➤ NSEI_OTS_AR-7.6 ⮘免費下載的最佳網站NSEI_OTS_AR-7.6認證指南
- 最新NSEI_OTS_AR-7.6題庫資源 🦰 免費下載NSEI_OTS_AR-7.6考題 💝 NSEI_OTS_AR-7.6最新考題 🦕 請在▛ www.newdumpspdf.com ▟網站上免費下載【 NSEI_OTS_AR-7.6 】題庫NSEI_OTS_AR-7.6題庫最新資訊
- NSEI_OTS_AR-7.6最新題庫 🐣 NSEI_OTS_AR-7.6認證資料 🚣 NSEI_OTS_AR-7.6認證資料 🚺 到▶ www.newdumpspdf.com ◀搜尋➠ NSEI_OTS_AR-7.6 🠰以獲取免費下載考試資料NSEI_OTS_AR-7.6題庫最新資訊
-
disqus.com, divisionmidway.org, www.4shared.com, scalar.usc.edu, scalar.usc.edu, www.fundable.com, justpaste.me, zenwriting.net, telegra.ph, scalar.usc.edu, Disposable vapes


 icons at the top
right corner of the subsection.