2026 Latest PassSureExam NSE7_FSN_AR-7.6 PDF Dumps and NSE7_FSN_AR-7.6 Exam Engine Free Share: https://drive.google.com/open?id=1oCEHfk1OgdKb-PhuI8ZBB7QDCJmJV4TT
Dear candidates, pass your test with our accurate & updated NSE7_FSN_AR-7.6 training tools. As we all know, the well preparation will play an important effect in the NSE7_FSN_AR-7.6 actual test. Now, take our NSE7_FSN_AR-7.6 as your study material, and prepare with careful, then you will pass successful. If you really want to choose our Fortinet NSE7_FSN_AR-7.6 PDF torrents, we will give you the reasonable price and some discounts are available. What’s more, you will enjoy one year free update after purchase of NSE7_FSN_AR-7.6 practice cram.
| Section |
Objectives |
| Topic 1: SD-WAN |
- Troubleshooting
- 1. Performance Analysis
- 2. SD-WAN Diagnostics
- Traffic steering
- 1. Policy-based Routing
- 2. Application-aware Routing
- SD-WAN deployment
- 1. Health Checks
- 2. Overlay Design
- 3. Performance SLA
- Centralized management
- 1. SD-WAN Orchestration
- 2. Monitoring and Analytics
|
| Topic 2: Enterprise Firewall |
- System configuration
- 1. VDOMs and VLANs
- 2. High Availability
- 3. Security Fabric
- 4. Hardware acceleration
- Central management
- 1. FortiManager
- 2. FortiAnalyzer
- Security profiles
- 1. Web Filtering
- 2. Application Control
- 3. SSL/SSH Inspection
- 4. IPS
- Routing and VPN
- 1. Static and Dynamic Routing
- 2. BGP and OSPF
- 3. IPsec VPN
- Authentication and Access Control
- 1. Remote Authentication
- 2. Identity-based Policies
- Troubleshooting
- 1. Traffic Flow Analysis
- 2. Debugging
|
>> Authentic Fortinet NSE7_FSN_AR-7.6 Exam Questions <<
Multiple Formats Of Real NSE7_FSN_AR-7.6 Exam Questions
Have tough-minded boy only, ability appeases billows, hoist the sails Yuan Hang. Our Fortinet NSE7_FSN_AR-7.6 exam dumps are the first step to bring you achievement. It provides you with pdf real questions and answers. By choosing it, you must put through Fortinet NSE7_FSN_AR-7.6 Certification that other people think it is very difficult. After you get the certification, you can lighten your heart and start a new journey.
Fortinet NSE 7 - Secure Networking 7.6 Architect Sample Questions (Q158-Q163):
NEW QUESTION # 158
Refer to the exhibit.
The output of a BGO debug command is shown.
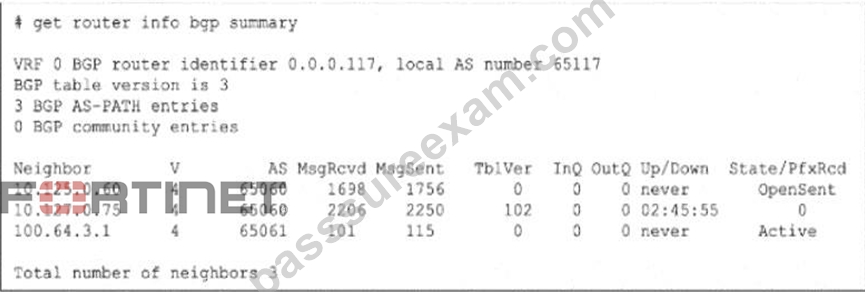
What is the most likely reason that the local FortiGate is not receiving any prefixes from its neighbors?
- A. The RIB-OUT configuration for router 10.127.0.75 prevents any route advertisement to the local router.
- B. The local router is waiting for the keepalive message from the router 10.125.0.60.
- C. None of the three neighbors has successfully established the TCP three-way handshake with the local router.
- D. The router 100.64.3.1 is waiting for the OPEN message from the local router.
Answer: A
Explanation:
To identify the reason for the lack of prefixes, we must interpret the State/PfxRcd and Up/Down columns in the get router info bgp summary exhibit.
Analyze Neighbor Status:
Neighbor 10.125.0.60: State is OpenSent. This session is not established. It is stuck in the negotiation phase.
Neighbor 100.64.3.1: State is Active. This session is not established. The router is actively trying to initiate a TCP connection.
Neighbor 10.127.0.75:
Up/Down: 02:45:55. This indicates the BGP session has been Up (Established) for almost 3 hours.
State/PfxRcd: 0. This number represents the count of prefixes received. The session is fully established, but the neighbor has sent zero routes.
Determine the Cause:
Since the session with 10.127.0.75 is established, connectivity and handshakes (Options A, B, C) are not the issue for this neighbor.
The fact that it is Up but sending 0 prefixes strongly implies that the neighbor is configured to filter out its routes before sending them to the local FortiGate.
Option D correctly identifies this as a RIB-OUT (Routing Information Base - Outbound) configuration issue on the neighbor (Router 10.127.0.75), which prevents it from advertising its routes.
Reference:
FortiGate Security 7.6 Study Guide (BGP): " In the BGP summary, if the State/PfxRcd shows a number (e.g.,
0), the session is Established. A value of 0 means the peering is up, but no routes have been received, often due to route-map or prefix-list filtering on the remote peer. "
NEW QUESTION # 159
Which two protocol states indicate that traffic is bidirectional? (Choose two.)
- A. proto_state=00 for an ICMP session.
- B. proto_state=05 for a TCP session.
- C. proto_state=01 for a TCP session.
- D. proto_state=01 for a UDP session.
Answer: C,D
Explanation:
The correct answers are A and B.
For UDP, the study guide states this directly: "For UDP, the session state can have only two values: 00 when traffic is only one way, and 01 when traffic is two ways. For ICMP, the protocol state is always 00." That makes B correct and D incorrect.
For TCP, the study guide explains that the protocol state is a two-digit number, where the first digit is the server-side state and the second digit is the client-side state. It also states that the first digit is 0 when the session is not subject to any inspection, and the TCP state table shows that value 1 = ESTABLISHED So, for a normal non-proxied/non-inspected TCP session, proto_state=01 means the TCP session is in the ESTABLISHED state. An established TCP session means the three-way handshake has completed, which requires traffic in both directions. That is why A is correct.
The study guide also says: "proto_state=11 means that the TCP three-way handshake for both server-side and client-side is completed (ESTABLISHED)." This confirms that TCP state value 1 represents an established state.
Why C is not selected: the study guide defines value 5 as TIME_WAIT and says: "When a session is closed by both the sender and receiver, FortiGate keeps that session in the session table for a few seconds... This is the state value 5." So proto_state=05 represents a closing/closed TCP session in TIME_WAIT, not the normal bidirectional state the question is testing.
Therefore, the verified answers are A and B.
NEW QUESTION # 160
Refer to the exhibit.
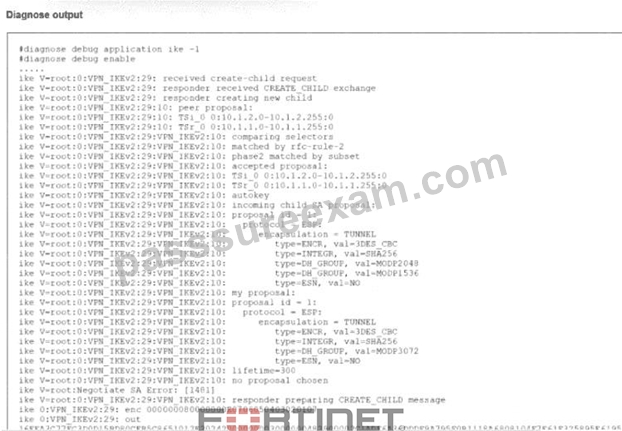
An IPsec VPN tunnel using IKEv2 was brought up successfully, but when the tunnel rekey takes place the tunnel goes down.
The debug command for IKE was enabled and, in the exhibit, you can review the partial output of the debug IKE while attempting to bring the tunnel up.
What is causing. The tunnel to be down?
- A. A Diffie-Hellman mismatch
- B. Blocked traffic on UDP port 500
- C. A mismatch m the Phase 1 negotiations
- D. A mismatch in the Phase 2 negotiations
Answer: A
Explanation:
To determine the cause of the failure, we must analyze the IKEv2 debug output provided in the exhibit (image_ad3dc6.jpg):
Identify the Negotiation Phase:
The debug log shows: responder received CREATE_CHILD exchange.
In IKEv2, the CREATE_CHILD_SA exchange is used to create new Child SAs (Phase 2) or to rekey existing ones.
The fact that the tunnel was previously " brought up successfully " implies the initial IKE SA (Phase 1) is stable, and this error is occurring specifically during a rekey event, which often involves Perfect Forward Secrecy (PFS).
Analyze the Proposals (The Mismatch):
Incoming Proposal (Remote Peer):
The remote peer sends a proposal containing two Diffie-Hellman groups: type=DH_GROUP, val=MODP2048 (Group 14) and type=DH_GROUP, val=MODP1536 (Group 5).
My Proposal (Local FortiGate):
The local FortiGate configuration expects: type=DH_GROUP, val=MODP3072 (Group 15).
Result of the Negotiation:
The debug output concludes with: no proposal chosen and Negotiate SA Error.
This error occurs because the local FortiGate cannot find a common Diffie-Hellman group between what it requires (Group 15) and what the peer is offering (Groups 14 or 5).
While this is technically a mismatch occurring during the Phase 2 (Child SA) creation, " A Diffie-Hellman mismatch " (Option A) is the precise root cause identified in the logs.
Why other options are incorrect:
B: The log shows received create-child request, confirming that UDP traffic is reaching the device and is not blocked.
C: The failure is in the CREATE_CHILD exchange (Phase 2/Rekey), not the IKE_SA_INIT or IKE_AUTH (Phase 1) exchanges.
D: While the mismatch is occurring within the Phase 2 definitions, Option A is the specific technical reason for the no proposal chosen error shown in the DH_GROUP lines.
Reference:
FortiGate Security 7.6 Study Guide (IPsec VPN): " Phase 2 parameters... if Perfect Forward Secrecy (PFS) is enabled, a Diffie-Hellman exchange is performed again. Both peers must match the DH Group. "
NEW QUESTION # 161
In which two ways does FortiGate utilize the Internet Service Database (ISDB) within firewall policies and SD-WAN rules? (Choose two.)
- A. The ISDB limits access by URL and domain.
- B. The ISDB can be used to block the IP addresses and ports of an application predefined by FortiGuard.
- C. FortiGate has a predefined list of IP addresses and ports for specific applications downloaded from FortiGuard.
- D. The ISDB works in proxy mode only, allowing the analysis of packets at Layers 3 and 4 of the OSI model.
Answer: B,C
Explanation:
Comprehensive and Detailed 100 to 150 words of Explanation From Secure Networking Architect Study Guides topics:
ISDB provides FortiGate with FortiGuard-maintained definitions of well-known internet services. These definitions associate services and applications with the IP address ranges, protocols, and ports required to identify their traffic. Administrators can reference ISDB objects directly in firewall policies instead of manually maintaining changing address and service definitions, supporting actions such as allowing or blocking traffic. Thus, C and D describe valid uses.
ISDB information can also be referenced by SD-WAN routing and steering decisions. It is not a URL/domain categorization mechanism; that functionality belongs primarily to web filtering, eliminating A. ISDB is also not restricted to proxy inspection mode. Its matching information participates in firewall-policy and routing
/SD-WAN processing using network and service attributes, eliminating B. FortiGuard updates keep the predefined internet-service definitions current.
NEW QUESTION # 162
Refer to the exhibit, which shows the output o! the BGP database.
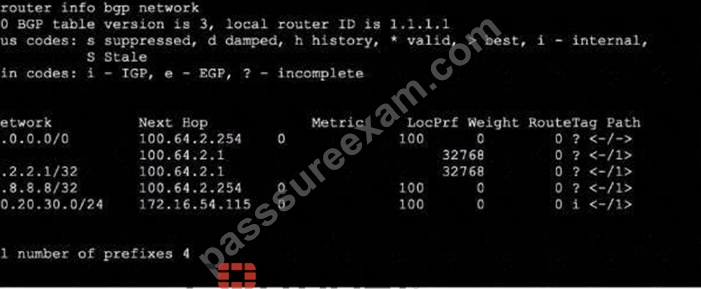
Which two statements are correct? (Choose two.)
- A. The output shows all prefixes advertised by all neighbors as well as the local router.
- B. The advertised prefix of 10.20.30.0/24 is being advertised through the redistribution of another routing protocol.
- C. The first four prefixes are being advertised using a legacy route advertisement.
- D. The advertised prefix of 10.20.30.0/24 was configured using the network command.
Answer: A,D
Explanation:
For Option A:In Fortinet BGP (and standard BGP), when a prefix is displayed with an " i " (lowercase i) in the Path column, it represents an internal prefix that originated from the local router, typically configured via the BGP " network " command. In the exhibit, the prefix 10.20.30.0/24 is listed with a Path value of i, indicating it was injected into BGP by the local router using the network statement, not via redistribution from another routing protocol. The same logic applies to i as documented: " Origin code ' i ' means the route was injected via the network command. " For Option D:The get router info bgp network output is a summary table displaying both local and received BGP routes. It lists all known routes to the BGP process, whether received from peers or originated locally.
The exhibit shows all BGP prefixes known to the local router, matching the official admin guide's description of this command's output.
Explanation for B and C:
The phrase "legacy route advertisement" is not formalized in BGP documentation or Fortinet's admin guide; the output uses standard BGP mechanics.
If a route was redistributed into BGP from another routing protocol, the Path field would display a " ? " (question mark) for incomplete (redistributed) origin. Here the /24 route has " i " so it is NOT a redistribution.
References:
FortiOS Administration Guide: BGP Configuration and Route Table Interpretation Official BGP Command Reference: Show BGP Network, Path Codes, Route Origination Indicators
NEW QUESTION # 163
......
Most returned customers said that our NSE7_FSN_AR-7.6 dumps pdf covers the big part of main content of the certification exam. Questions and answers from our NSE7_FSN_AR-7.6 free download files are tested by our certified professionals and the accuracy of our questions are 100% guaranteed. Please check the free demo of NSE7_FSN_AR-7.6 Braindumps before purchased and we will send you the download link of NSE7_FSN_AR-7.6 real dumps after payment.
Latest NSE7_FSN_AR-7.6 Test Objectives: https://www.passsureexam.com/NSE7_FSN_AR-7.6-pass4sure-exam-dumps.html
- How Can Fortinet NSE7_FSN_AR-7.6 Exam Questions Assist You In Exam Preparation? 👈 Open website ( www.practicevce.com ) and search for ✔ NSE7_FSN_AR-7.6 ️✔️ for free download 👡Real NSE7_FSN_AR-7.6 Exam
- Pdf Demo NSE7_FSN_AR-7.6 Download 🏴 Exam NSE7_FSN_AR-7.6 Dumps 🏹 Reliable NSE7_FSN_AR-7.6 Exam Test 🗳 ➠ www.pdfvce.com 🠰 is best website to obtain [ NSE7_FSN_AR-7.6 ] for free download 🕴NSE7_FSN_AR-7.6 Discount
- Pass Guaranteed 2026 Fortinet NSE7_FSN_AR-7.6 –High Pass-Rate Authentic Exam Questions 🥾 Enter ✔ www.pass4test.com ️✔️ and search for ➽ NSE7_FSN_AR-7.6 🢪 to download for free 👣Pdf NSE7_FSN_AR-7.6 Free
- Professional Authentic NSE7_FSN_AR-7.6 Exam Questions - Win Your Fortinet Certificate with Top Score 😵 Download ➥ NSE7_FSN_AR-7.6 🡄 for free by simply entering “ www.pdfvce.com ” website 👖NSE7_FSN_AR-7.6 Certification Test Answers
- Free PDF 2026 Unparalleled Fortinet Authentic NSE7_FSN_AR-7.6 Exam Questions 🔭 Easily obtain free download of 《 NSE7_FSN_AR-7.6 》 by searching on ➽ www.pdfdumps.com 🢪 🛒Reliable NSE7_FSN_AR-7.6 Exam Prep
- How Can Fortinet NSE7_FSN_AR-7.6 Exam Questions Assist You In Exam Preparation? 📋 Search for ➥ NSE7_FSN_AR-7.6 🡄 and obtain a free download on ⇛ www.pdfvce.com ⇚ 🍔NSE7_FSN_AR-7.6 Latest Exam Testking
- NSE7_FSN_AR-7.6 Accurate Test 💥 Valid NSE7_FSN_AR-7.6 Test Voucher ↙ Latest NSE7_FSN_AR-7.6 Exam Labs 📝 Copy URL [ www.easy4engine.com ] open and search for ➠ NSE7_FSN_AR-7.6 🠰 to download for free 👉NSE7_FSN_AR-7.6 Accurate Test
- Three Fortinet NSE7_FSN_AR-7.6 Exam Questions Formats - Make Your Exam Preparation Easy ☃ Simply search for ➥ NSE7_FSN_AR-7.6 🡄 for free download on 「 www.pdfvce.com 」 🔘NSE7_FSN_AR-7.6 Valid Braindumps Files
- Pass Guaranteed 2026 Fortinet NSE7_FSN_AR-7.6 –High Pass-Rate Authentic Exam Questions 🧷 Copy URL [ www.troytecdumps.com ] open and search for ▛ NSE7_FSN_AR-7.6 ▟ to download for free 📬Latest NSE7_FSN_AR-7.6 Exam Labs
- Free PDF 2026 Latest Fortinet Authentic NSE7_FSN_AR-7.6 Exam Questions 🗣 Copy URL ☀ www.pdfvce.com ️☀️ open and search for 《 NSE7_FSN_AR-7.6 》 to download for free 💂New NSE7_FSN_AR-7.6 Study Guide
- 2026 Authentic NSE7_FSN_AR-7.6 Exam Questions 100% Pass | Efficient NSE7_FSN_AR-7.6: Fortinet NSE 7 - Secure Networking 7.6 Architect 100% Pass ➰ Search for ➽ NSE7_FSN_AR-7.6 🢪 and download exam materials for free through ✔ www.dumpsmaterials.com ️✔️ 🥧Pdf Demo NSE7_FSN_AR-7.6 Download
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, everlink.tools, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, vrcmods.com, Disposable vapes
BTW, DOWNLOAD part of PassSureExam NSE7_FSN_AR-7.6 dumps from Cloud Storage: https://drive.google.com/open?id=1oCEHfk1OgdKb-PhuI8ZBB7QDCJmJV4TT


 icons at the top
right corner of the subsection.