JN0-352題庫資料, 最新JN0-352試題, JN0-352證照考試, JN0-352考題資訊, JN0-352最新題庫資源

PDFExamDumps有最新的Juniper JN0-352 認證考試的培訓資料,PDFExamDumps的一些勤勞的IT專家通過自己的專業知識和經驗不斷地推出最新的Juniper JN0-352的培訓資料來方便通過Juniper JN0-352的IT專業人士。Juniper JN0-352的認證證書在IT行業中越來越有份量,報考的人越來越多了,很多人就是使用PDFExamDumps的產品通過Juniper JN0-352認證考試的。通過這些使用過產品的人的回饋,證明我們的PDFExamDumps的產品是值得信賴的。
Juniper JN0-352 Exam Syllabus Topics:
| Section |
Objectives |
| Layer 2 Switching and VLANs |
- Frame processing
- Bridging components
- Native VLANs and voice VLANs
- Inter-VLAN routing
- Ports and VLAN tagging
|
| IS-IS |
- Levels, areas and metrics
- Adjacencies and troubleshooting
- Link-state database and PDUs
|
| High Availability |
- Virtual chassis and graceful restart
- Link Aggregation Groups and RTG
- VRRP, NSR, NSB and BFD
|
| Tunnels |
- GRE and IP-IP configuration and troubleshooting
- IP tunneling concepts
|
| OSPF |
- Link-state database and packet types
- Areas and LSA types
- Router ID, adjacencies and neighbors
|
| BGP |
- BGP basic operations and message types
- Attributes and path selection
- EBGP and IBGP peer interactions
|
| Spanning Tree |
- STP and RSTP concepts, roles and states
- Convergence and reconvergence
- Bridge Protocol Data Units (BPDUs)
|
| Protocol-Independent Routing |
- Static, aggregate, generated routes
- Martian addresses and RIB groups
- Load balancing and filter-based forwarding
|
| Layer 2 Security |
- BPDU, loop and root protection
- MACsec and storm control
- Layer 2 firewall filters
- Port security (MAC limiting, DHCP snooping, DAI, IP source guard)
|
>> JN0-352題庫資料 <<
最新JN0-352試題 & JN0-352證照考試
在這個競爭激烈的IT行業中,擁有一些認證證書是可以幫助你步步高升的。很多公司升職加薪的依據就是你擁有的認證證書的含金量。Juniper JN0-352認證考試就是個含金量很高的考試。Juniper JN0-352 認證證書能滿足很多正在IT行業拼搏的人的需求。PDFExamDumps可以為你提供Juniper JN0-352認證考試的針對性訓練。你可以先在網上免費下載PDFExamDumps為你提供的關於Juniper JN0-352 認證考試的培訓工具的試用版和部分練習題及答案作為嘗試。
最新的 JNCIS-ENT JN0-352 免費考試真題 (Q163-Q168):
問題 #163
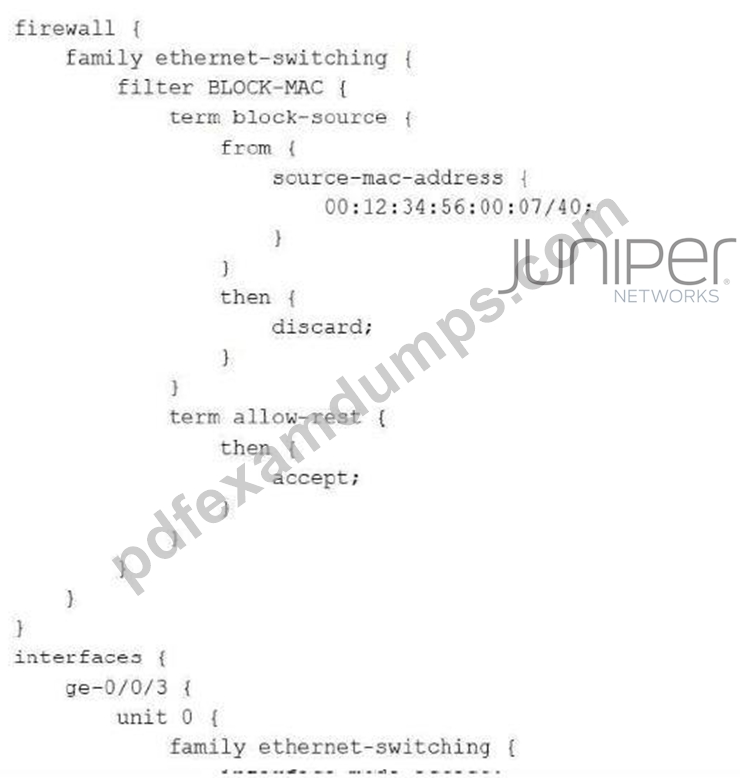
You need to apply a Layer 2 firewall filter on a Juniper Networks EX Series Switch to block traffic from the source MAC address 00:12:34:56:00:07 entering the switch on ge-0/0/3. After committing the configuration, traffic from the MAC address still passes through.
Referring to the exhibit, which statement is correct in this scenario?
- A. The filter is applied in the wrong direction.
- B. The interface needs to be of type trunk for the filter to evaluate correctly.
- C. Firewall filters under family ethernet-switching cannot match on MAC addresses.
- D. The MAC address and mask in the firewall filter need to be explicit.
答案:D
解題說明:
The intent of this filter is to match and discard traffic from one single, specific host MAC address, which requires the source-mac-address match condition to reference the complete, exact 48-bit address using an explicit /48 mask (or no mask at all, which Junos treats as an implicit full match) so that only that one precise address is matched. As configured, the term instead specifies a /40 mask on 00:12:34:56:00:07, meaning only the first 40 bits (the first five octets, 00:12:34:56:00) are actually significant to the match, while the sixth octet is effectively wildcarded across its full range; this produces an imprecise, overly broad match criterion rather than the single-host match the administrator intended, and is a common configuration mistake that undermines the predictability and correctness of MAC-based filtering. The lesson tested here is that source and destination MAC address match conditions in Junos firewall filters must be specified with the correct, deliberate, and explicit prefix length appropriate to the intended scope - typically /48 for a single exact host
- rather than an arbitrary or miscalculated mask value. Firewall filters under family ethernet-switching are fully capable of matching on both source-mac-address and destination-mac-address, which rules out that option entirely. Layer 2 MAC-based filters function correctly on both access and trunk interface modes, so interface type is not a limiting factor here. There is no indication in the exhibit that the filter's application direction (input versus output) is reversed. Reference topics: Junos Enterprise Switching - Layer 2 Security, MAC Address Match Conditions and Prefix Length Precision.
問題 #164
Which two statements are correct about VRRP? (Choose two.)
- A. The virtual IP address must match on all participating devices
- B. The VRRP group number must be unique on all participating devices
- C. The VRRP group number must match on all participating devices
- D. The virtual IP address must be unique on all participating devices
答案:A,C
解題說明:
The virtual IP address must match on all participating devices - All routers in the same VRRP group must be configured with the same virtual IP address to provide redundancy.
The VRRP group number must match on all participating devices - All routers in the same VRRP group must have the same group number to identify the VRRP group.
問題 #165
You are required to ensure that Switch 1 will always be designated as the root bridge when participating in your switched network.
What do you need to do to satisfy this requirement?
- A. Ensure Switch1 has the lowest bridge priority of all the other switches.
- B. Ensure Switch1 has the highest port costs of all the other switches.
- C. Ensure Switch 1 has the highest system MAC address.
- D. Ensure Switch1 has the lowest port priority of all other switches.
答案:A
解題說明:
Because root bridge election is decided primarily by comparing bridge priority values - with the switch advertising the numerically lowest priority always winning, and MAC address serving only as a fallback tiebreaker when priorities are tied - the only deterministic, reliable way to guarantee that a specific switch is elected root regardless of any other switch's hardware characteristics is to explicitly configure that switch with a lower bridge priority than every other participating switch in the topology. Relying on MAC address alone, as the first distractor suggests, is fundamentally unreliable: MAC addresses are burned in at the factory, cannot be predicted or controlled by the administrator, and any future hardware replacement or newly introduced switch with a numerically lower MAC address could unexpectedly seize the root role since MAC comparison only comes into play at equal priority in the first place, meaning a 'highest MAC' strategy does not even align with how the tiebreak actually favors the lowest value. Port priority and port cost are entirely separate STP parameters that influence which port on a non-root switch is selected as its root port, or which port is selected as designated versus blocking on a given segment; neither parameter has any bearing whatsoever on which switch is elected root bridge for the whole topology, since that decision is made purely from the Bridge ID comparison, independent of any per-port settings. Explicitly and deliberately lowering Switch 1's configured bridge priority is the only correct, industry-standard method. Reference topics: Junos Enterprise Switching - Spanning Tree Protocols, Guaranteeing Root Bridge Placement via Bridge Priority.
問題 #166
Click the Exhibit button.
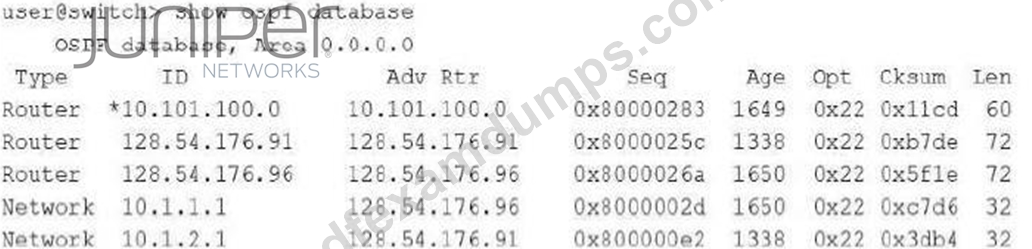
You run the show ospf database command and you see a Router LSA marked with an asterisk.
Referring to the exhibit, what is the significance of this result?
- A. The LSA is advertised by a remote device.
- B. The LSA is advertised by the backup designated router.
- C. The LSA is advertised by the local device.
- D. The LSA is advertised by the designated router.
答案:C
解題說明:
In the output of show ospf database, Junos marks every self-originated link-state advertisement with an asterisk immediately preceding the LSA's link-state ID. A self-originated LSA is one that was created and flooded by the router on which the command is being executed, as opposed to an LSA that was received from and originated by a neighboring router elsewhere in the area. In this exhibit, the asterisked Router LSA has an ID of 10.101.100.0 and an Advertising Router value of the same 10.101.100.0, confirming that this particular Router LSA describes the local device's own links, area membership, and interface costs, and that the local router itself flooded this LSA into the area's link-state database. This distinction matters operationally because when troubleshooting OSPF topology or SPF calculation issues, engineers frequently need to isolate their own router's advertised state from the states advertised by every other router in the area; the asterisk provides an immediate, unambiguous visual cue for that separation without needing to cross-reference the router's own ID separately. It has no relationship to designated router or backup designated router status - DR/BDR roles are indicated elsewhere in interface-level output, not through the asterisk convention in the LSA database dump, and a router that is neither DR nor BDR still self-originates and flags its own Router LSA the same way.
Reference topics: Junos Enterprise Routing - OSPF, Interpreting the OSPF Link-State Database.
問題 #167
You are troubleshooting a BGP routing issue between your network and a customer router and are reviewing the BGP routing policies. Which two statements are correct in this scenario?
(Choose two.)
- A. Import policies are applied after the RIB-ln table.
- B. Import policies are applied to routes in the RIB-Local table.
- C. Export policies are applied after the RIB-Local table.
- D. Export policies are applied to routes in the RIB-ln table.
答案:A,C
解題說明:
In BGP, routing policies are used to control the flow of routing information between BGP peers.
Option C suggests that import policies are applied after the RIB-In table. This is correct because import policies in BGP are applied to routes that are received from a BGP peer, before they are installed in the local BGP Routing Information Base (RIB-In). The RIB-In is a database that stores all the routes that are received from all peers.
Option D suggests that export policies are applied after the RIB-Local table. This is correct because export policies in BGP are applied to routes that are being advertised to a BGP peer, after they have been selected from the local BGP Routing Information Base (RIB-Local). The RIB-Local is a database that stores all the routes that the local router is using.
問題 #168
......
您是否在尋找可靠的學習資料來準備即將來的JN0-352考試?如果是的話,您可以嘗試PDFExamDumps的產品和服務。我們提供最新的Juniper JN0-352考古題是經過眾多考生和專家檢驗過的學習指南,保證成功率百分之百的考古題。對于購買JN0-352題庫產品的客戶,我們還提供一年的免費更新服務。所以,您不必擔心,Juniper JN0-352學習指南不僅讓您更準確的了解考試的出題點,還能讓您更有范圍的學習相關知識,高效率的通過JN0-352考試。
最新JN0-352試題: https://www.pdfexamdumps.com/JN0-352_valid-braindumps.html
- 最新有效的JN0-352學習指南資料 - 提供免费的JN0-352試題下載 🛀 【 tw.fast2test.com 】是獲取“ JN0-352 ”免費下載的最佳網站JN0-352最新題庫
- JN0-352考試題庫 🆖 JN0-352考試大綱 🌗 JN0-352考題資源 😐 打開「 www.newdumpspdf.com 」搜尋➠ JN0-352 🠰以免費下載考試資料JN0-352證照資訊
- 熱門的JN0-352題庫資料,免費下載JN0-352學習資料幫助妳通過JN0-352考試 🚀 ➠ www.vcesoft.com 🠰上的⮆ JN0-352 ⮄免費下載只需搜尋JN0-352 PDF題庫
- 最新有效的JN0-352學習指南資料 - 提供免费的JN0-352試題下載 📮 免費下載⮆ JN0-352 ⮄只需進入➽ www.newdumpspdf.com 🢪網站最新JN0-352題庫資訊
- 下載JN0-352題庫資料,關于Enterprise Routing and Switching, Specialist (JNCIS-ENT) 🥮 ( tw.fast2test.com )最新「 JN0-352 」問題集合JN0-352測試題庫
- 有效的JN0-352題庫資料和資格考試考試領導者和高質量的最新JN0-352試題 🤔 在「 www.newdumpspdf.com 」上搜索⇛ JN0-352 ⇚並獲取免費下載JN0-352 PDF
- JN0-352最新題庫 ✴ JN0-352考試資訊 🐊 JN0-352證照資訊 💟 ▷ www.vcesoft.com ◁上的☀ JN0-352 ️☀️免費下載只需搜尋JN0-352學習指南
- 最新JN0-352題庫 👊 JN0-352考試備考經驗 🛤 JN0-352測試題庫 🥁 立即打開[ www.newdumpspdf.com ]並搜索➥ JN0-352 🡄以獲取免費下載JN0-352 PDF
- 保證通過的Juniper JN0-352題庫資料是行業領先材料&100%合格率的JN0-352:Enterprise Routing and Switching, Specialist (JNCIS-ENT) 🥈 在➤ www.newdumpspdf.com ⮘搜索最新的➠ JN0-352 🠰題庫JN0-352考題資源
- 有效的JN0-352題庫資料和資格考試考試領導者和高質量的最新JN0-352試題 ⚫ ☀ www.newdumpspdf.com ️☀️上的⮆ JN0-352 ⮄免費下載只需搜尋JN0-352考題資源
- 最有效的JN0-352題庫資料,提前為Enterprise Routing and Switching, Specialist (JNCIS-ENT) JN0-352考試做好準備 🕎 來自網站▛ www.testpdf.net ▟打開並搜索⇛ JN0-352 ⇚免費下載JN0-352證照資訊
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, writeablog.net, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes


 icons at the top
right corner of the subsection.