Cilium-Associate日本語対策, Cilium-Associate的中合格問題集, Cilium-Associate日本語認定対策, Cilium-Associate試験内容, Cilium-Associate試験問題解説集
社会でより良く生き残るためには、私たちの社会の要件を理解しなければなりません。理論的な知識に加えて、より実践的なスキルが必要です。 Cilium-Associate実践ガイドを使用すると、認定資格を迅速に取得でき、競争力が大幅に向上します。もちろん、あなたの利益はCilium-Associate証明書だけではありません。 Cilium-Associate学習教材は、あなたの働き方とライフスタイルを変えます。他の人よりも効率的に作業できます。 Cilium-Associateトレーニング資料は、このような大きな役割を果たすことができます。
Linux Foundation Cilium-Associate Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| Topic 1: Network Observability |
10% |
- Understand the Observability Capabilities of Hubble
- 1. Know How to Use Hubble from the Command Line or the Hubble UI
- 2. Enabling Layer 7 Protocol Visibility
|
| Topic 2: Service Mesh |
16% |
- Know How to use Ingress or Gateway API for Ingress Routing
- 1. Sidecar-based versus Sidecarless Architectures
- 2. Encrypting Traffic in Transit with Cilium
- 3. Service Mesh Use Cases
- 4. Understand the Benefits of Gateway API over Ingress
|
| Topic 3: Network Policy |
18% |
- Interpret Cilium Network Policies and Intent
- 1. Policy Enforcement Modes
- 2. Understand Cilium's Identity-based Network Security Model
- 3. Policy Rule Structure
- 4. Kubernetes Network Policies versus Cilium Network Policies
|
| Topic 4: BGP and External Networking |
6% |
- Egress Connectivity Requirements
- 1. Understand Options to Connect Cilium-managed Clusters with External Networks
|
| Topic 5: Cluster Mesh |
10% |
- Understand the Benefits of Cluster Mesh for Multi-cluster Connectivity
- 1. Achieve Service Discovery and Load Balancing Across Clusters with Cluster Mesh
|
| Topic 6: Installation and Configuration |
10% |
- Know How to Use Cilium CLI to Query and Modify the Configuration
- 1. Using Cilium CLI to Install Cilium, Run Connectivity Tests, and Monitor its Status
|
| Topic 7: Architecture |
20% |
- Understand the Role of Cilium in Kubernetes Environments
- 1. IP Address Management (IPAM) with Cilium
- 2. Cilium Component Roles
- 3. Cilium Architecture
- 4. Datapath Models
|
| Topic 8: eBPF |
10% |
- Understand the Role of eBPF in Cilium
- 1. eBPF Key Benefits
- 2. eBPF-based Platforms versus IPTables-based Platforms
|
>> Cilium-Associate日本語対策 <<
Cilium-Associate的中合格問題集 & Cilium-Associate日本語認定対策
これは、今後のCilium-Associateテストのために有効な試験準備資料を購入する良い方法です。 適切な選択により、半分の労力で2倍の結果が得られます。 適切な試験準備により、明確な方向性が示され、効率的な準備ができます。 Cilium-Associate試験の準備は正しい方向を示すだけでなく、実際の試験問題のほとんどをカバーできるため、試験の内容を事前に知ることができます。 Linux Foundation Cilium-Associate試験準備の質問と回答をマスターし、試験気分を積極的に調整することもできます。
Linux Foundation Cilium Certified AssociateCCA 認定 Cilium-Associate 試験問題 (Q45-Q50):
質問 # 45
Which of these observability features is NOT supported by Hubble?
- A. Hubble Is able to filter flows based on a given Kubernetes node name.
- B. Hubble is able to filter traffic based on the network policy verdict.
- C. Hubble is able to observe by HTTP Status code (like "404" or "200").
- D. Hubble Is able to provide Layer 7 visibility In eBPF, without the need for a proxy.
正解:D
解説:
Technical explanation
Hubble does not obtain Layer 7 protocol visibility exclusively through eBPF without a proxy. By default, Cilium's datapath exposes Layer 3 and Layer 4 flow information. To produce supported application-layer events, traffic is selected through an L7 Cilium policy and redirected to the node-local Envoy proxy. Envoy parses the application protocol and forwards access-log information that Cilium and Hubble expose as Layer
7 flow events.
The other capabilities are supported. Hubble flow records contain the observing node, and the CLI provides node-based filtering. HTTP-aware flows can contain response status codes, enabling inspection or filtering for results such as 200 and 404. Hubble also records forwarding verdicts and drop reasons. Operators can filter for DROPPED traffic and distinguish policy-denied connections from forwarded traffic and other failure conditions.
This separation is fundamental to Cilium's architecture: eBPF provides efficient kernel-level forwarding, security enforcement, and L3/L4 observability, while Envoy supplies protocol parsing when request-level context is required. The integration remains transparent to applications, but the proxy is still present in the traffic path for Layer 7 visibility.
Therefore, B describes the unsupported mechanism and is the correct answer.
Official references
Layer 7 Protocol Visibility ; Envoy ; Hubble CLI .
Study Guide topic: Network Observability.
質問 # 46
When using Cilium with the kube-proxy replacement enabled, which underlying technology is effectively replaced with eBPF?
- A. Routing
- B. BGP
- C. firewalld
- D. Iptables/IPVS
正解:D
解説:
Technical explanation
Kubernetes kube-proxy conventionally implements Service translation and load balancing through either iptables or IPVS. With Cilium's kube-proxy replacement enabled, eBPF programs and maps perform Kubernetes Service handling directly in the kernel, including ClusterIP, NodePort, LoadBalancer, ExternalIP, and related service translation functions. C is therefore correct.
The replacement can operate at socket hooks and packet-processing hooks. Service and backend information is stored in eBPF maps, allowing the datapath to select backends and perform address translation without traversing the kube-proxy-generated iptables or IPVS rules normally used for Kubernetes Services.
BGP is not replaced. Cilium's BGP Control Plane is a separate feature used to advertise routes and service addresses to external routers. Routing itself is also not eliminated; Cilium can implement and accelerate routing decisions with eBPF, but packets still require a valid forwarding model. firewalld is a host firewall- management service and is not the underlying Kubernetes Service implementation replaced by kube-proxy replacement.
Relevant installations must satisfy the kernel and device requirements for Cilium's eBPF service load- balancer functionality.
Official references
Kubernetes Without kube-proxy
Study Guide topic: kube-proxy replacement, eBPF service maps, iptables, and IPVS.
質問 # 47
We observed Hubble output:
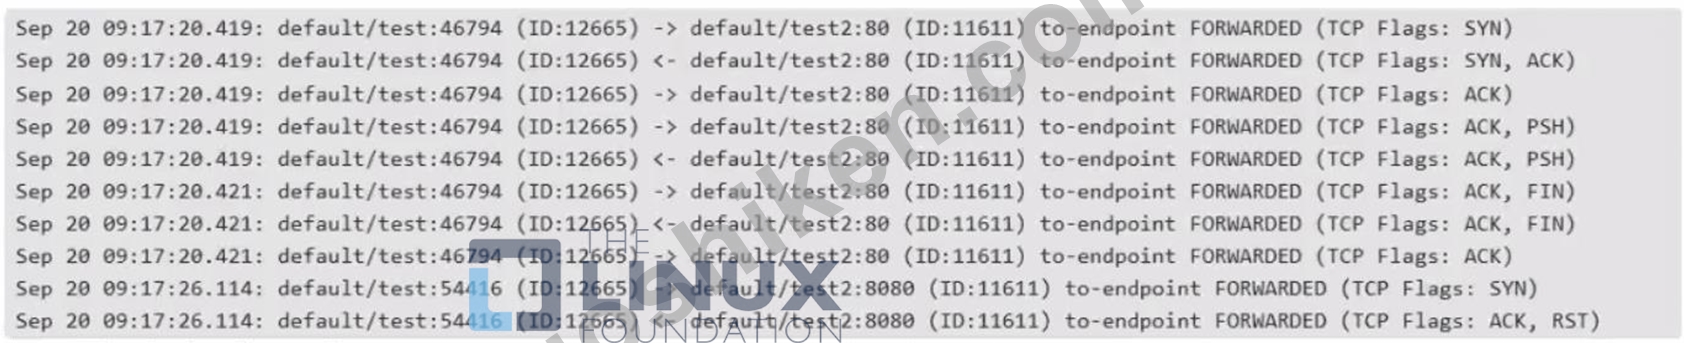
Question 7 Hubble flow exhibit
Explain what may have happened:
- A. On test pod (default namespace), someone launched commands: curl 16.244.0.191 #Output: Succeeded curl ie.244.0.191:8080 #Output: Failed
- B. On test2 pod (default namespace), someone launched commands:
curl 16.244.0.143 #Output: Failed curl 10.244.0.143:8080 #Output: Succeeded
- C. On test pod (default namespace), someone launched commands:
curl 19.244.0.191 #Output: Failed
curl 16.244.0.191:8680 #Output: Succeeded
- D. On test2 pod (default namespace), someone launched commands:
curl 10.244.0.143 #Output: Succeeded curl 10.244.0.143:8080 #Output: Failed
正解:A
解説:
Technical explanation
The exhibit records connections originating from default/test and directed to default/test2 , eliminating B and C because those choices reverse the initiating workload. For destination port 80, the flow shows the TCP three-way handshake-SYN, SYN-ACK, and ACK-followed by bidirectional packets with ACK/PSH flags and an orderly FIN exchange. This is the pattern of a successfully established request and response, so the first curl operation succeeded.
The later connection targets port 8080. Hubble records a SYN from test followed by an ACK, RST response from test2 . A reset returned immediately after the connection attempt indicates that the destination rejected or could not accept the connection, commonly because no process was listening on that port. It is not shown as a policy drop; both entries carry the FORWARDED verdict. Thus the network delivered the packets, but the TCP connection itself failed.
Option D is the only choice matching a successful request from test to port 80 and a failed request from test to port 8080. Its displayed IP strings contain source-document transcription defects, but its workload direction, ports, and outcomes match the exhibit.
Official references
Inspecting Network Flows with the CLI ; Troubleshooting with Hubble .
Study Guide topic: Network Observability.
質問 # 48
If you are required to block ingress traffic from external IPs for all pods in your cluster, which of the following network policies would be the best fit?
- A. NetworkPolicy
- B. CiliumNetworkPolicy
- C. CiliumClusterWideNetworkPolicy
- D. CiliumGlobalPolicy
正解:C
解説:
Technical explanation
A cluster-wide requirement is best implemented with CiliumClusterwideNetworkPolicy , whose correct resource spelling is CiliumClusterwideNetworkPolicy . Unlike a namespaced CiliumNetworkPolicy , this Cilium CRD is non-namespaced and can select endpoints across the entire cluster.
To deny external ingress for every Cilium-managed pod, a cluster-wide policy can use an empty endpointSelector and an ingressDeny rule selecting the world entity. Cilium defines world as network endpoints outside the cluster. An alternative allow-list construction can permit only the cluster entity, thereby excluding external sources, but an explicit deny rule usually communicates the requirement more directly.
A standard Kubernetes NetworkPolicy and a CiliumNetworkPolicy are namespaced, requiring repeated resources in every applicable namespace. CiliumGlobalPolicy is not a valid Cilium resource type. Although the option capitalizes "Wide" differently from the actual kind, D unmistakably identifies the intended cluster- scoped policy.
Official references
Cilium Deny Policies , Cilium Network Policy Types
Study Guide topic: Cluster-scoped policies, external traffic, and reserved entities.
質問 # 49
Which one of the following commands will correctly display show the Cilium configuration?
- A. cilium config view
- B. cilium show run
- C. cilium show config
- D. kubectl describe ciliumconfig.ciliu # .io
正解:A
解説:
Technical explanation
cilium config view is the Cilium CLI command used to display the current Cilium configuration. It reads the configuration associated with the selected Kubernetes context, Cilium namespace, and Helm release. The command belongs to the cilium config command group, which manages installation configuration.
Option B reverses the expected command structure and does not correspond to a documented Cilium CLI operation. Option D resembles command syntax used on traditional network appliances but is not part of the Cilium CLI. Option C is both textually corrupted and conceptually inaccurate: Cilium configuration is not generally exposed through a cluster-wide resource named ciliumconfig.cilium.io . Runtime settings are commonly represented through the Cilium ConfigMap and Helm release values, while specialized resources such as CiliumNodeConfig apply targeted per-node configuration.
The wording "display show" is a source-bank editing defect but does not affect the answer. Administrators should also distinguish the external cilium management CLI from cilium-dbg , which runs with or communicates with the node-local Cilium agent and provides detailed datapath and agent diagnostics.
Official references
cilium config view , Cilium Component Overview
Study Guide topic: Cilium CLI configuration inspection and command structure.
質問 # 50
......
チャンスはいつも準備ができている人に賦与されると言われます。あなたはこのチャンスを早めに捉えて、我々社のLinux FoundationのCilium-Associate練習問題を通して、仕事に不可欠なCilium-Associate試験資格認証書を取得しなければなりません。我が社GoShikenのCilium-Associate問題集と我々のサービスに関して、弊社は誠実かつ信頼できる会社ですから、心配しなくて購買できます。
Cilium-Associate的中合格問題集: https://www.goshiken.com/Linux-Foundation/Cilium-Associate-mondaishu.html
- 素敵Linux Foundation Cilium-Associate|便利なCilium-Associate日本語対策試験|試験の準備方法Cilium Certified AssociateCCA的中合格問題集 💝 ➤ www.mogiexam.com ⮘で使える無料オンライン版☀ Cilium-Associate ️☀️ の試験問題Cilium-Associate認証資格
- Cilium-Associate復習攻略問題 😜 Cilium-Associate資格復習テキスト 👫 Cilium-Associateテスト資料 🍥 最新《 Cilium-Associate 》問題集ファイルは《 www.goshiken.com 》にて検索Cilium-Associate試験攻略
- 素敵Linux Foundation Cilium-Associate|便利なCilium-Associate日本語対策試験|試験の準備方法Cilium Certified AssociateCCA的中合格問題集 🎱 最新“ Cilium-Associate ”問題集ファイルは➡ www.xhs1991.com ️⬅️にて検索Cilium-Associate参考書勉強
- Cilium-Associate日本語サンプル 🤵 Cilium-Associate参考書勉強 🥱 Cilium-Associate試験攻略 💂 ➥ www.goshiken.com 🡄から簡単に➠ Cilium-Associate 🠰を無料でダウンロードできますCilium-Associate日本語関連対策
- Cilium-Associate資格復習テキスト 🎡 Cilium-Associate関連合格問題 👨 Cilium-Associate過去問無料 🌞 ➠ www.shikenpass.com 🠰にて限定無料の▛ Cilium-Associate ▟問題集をダウンロードせよCilium-Associate試験攻略
- 試験の準備方法-最高のCilium-Associate日本語対策試験-実用的なCilium-Associate的中合格問題集 🚹 Open Webサイト▶ www.goshiken.com ◀検索▛ Cilium-Associate ▟無料ダウンロードCilium-Associate復習攻略問題
- Cilium-Associate日本語関連対策 ⚗ Cilium-Associate復習範囲 🎋 Cilium-Associate関連合格問題 🧘 時間限定無料で使える▛ Cilium-Associate ▟の試験問題は《 www.topexam.jp 》サイトで検索Cilium-Associate認証資格
- 素敵Linux Foundation Cilium-Associate|便利なCilium-Associate日本語対策試験|試験の準備方法Cilium Certified AssociateCCA的中合格問題集 🥧 「 www.goshiken.com 」を開き、⮆ Cilium-Associate ⮄を入力して、無料でダウンロードしてくださいCilium-Associateテスト資料
- 有難いLinux Foundation Cilium-Associate | 効果的なCilium-Associate日本語対策試験 | 試験の準備方法Cilium Certified AssociateCCA的中合格問題集 📆 《 www.passtest.jp 》から( Cilium-Associate )を検索して、試験資料を無料でダウンロードしてくださいCilium-Associate最新テスト
- Cilium-Associate技術問題 ☃ Cilium-Associate試験攻略 🌇 Cilium-Associate参考書勉強 👵 ⮆ www.goshiken.com ⮄の無料ダウンロード「 Cilium-Associate 」ページが開きますCilium-Associate日本語問題集
- Cilium-Associate復習攻略問題 🕍 Cilium-Associate練習問題 🔦 Cilium-Associate日本語対策問題集 🧺 { www.passtest.jp }で「 Cilium-Associate 」を検索して、無料でダウンロードしてくださいCilium-Associateミシュレーション問題
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes


 icons at the top
right corner of the subsection.