3V0-21.25日本語対策, 3V0-21.25日本語講座, 3V0-21.25模擬モード, 3V0-21.25無料ダウンロード, 3V0-21.25日本語復習赤本
2026年GoShikenの最新3V0-21.25 PDFダンプおよび3V0-21.25試験エンジンの無料共有:https://drive.google.com/open?id=1PV20So1lhbyK2Un3PcAELjT0Vmo6Xuh2
お客様に最高のサービスをお楽しみいただくために、当社の3V0-21.25試験準備はすべて、何百人もの経験豊富な専門家によって設計されました。 3V0-21.25テストの質問は、お客様が試験に関する重要な知識を学ぶのに役立ちます。同時に、3V0-21.25テストトレントは、暗記学習の習慣に陥るのを防ぐのに役立ちます。学習に20〜30時間費やすだけで、3V0-21.25試験を受けて合格することができます。さらに、当社の3V0-21.25試験準備の正式な制作チームは、お客様に最新の情報をお楽しみいただけるよう、毎日学習システムを更新します。
VMware 3V0-21.25 認定試験の出題範囲:
| トピック |
出題範囲 |
| トピック 1 |
- IT Architectures, Technologies, Standards: This section focuses on understanding fundamental IT architectures, technologies, and industry standards that support VMware Cloud Foundation environments. It ensures candidates understand the foundational concepts required to design and manage automated cloud infrastructure solutions.
|
| トピック 2 |
- Install, Configure, Administrate the VMware Solution: This section covers configuring and administering VMware Cloud Foundation Automation environments. It includes managing provider portals, organizations, integrations, governance policies, resource deployments, automation workflows, blueprints, and orchestrator components.
|
| トピック 3 |
- Operation Management: This section focuses on monitoring and managing operational aspects of VMware Cloud Foundation Automation. It includes using VMware operations tools to monitor automation services, provider management, and organizational environments.
|
| トピック 4 |
- Plan and Design the VMware Solution: This section focuses on designing VMware Cloud Foundation Automation environments based on business and technical requirements. It includes understanding tenancy deployment models, organization types, and the functional components used to structure and manage cloud resources.
|
| トピック 5 |
- VMware Products and Solutions: This section covers VMware products related to VMware Cloud Foundation Automation, particularly components such as vSphere Supervisor and supervisor-based NSX networking. It focuses on identifying and differentiating architectural components and how they function within a deployment.
|
>> 3V0-21.25日本語対策 <<
3V0-21.25試験の準備方法|ハイパスレートの3V0-21.25日本語対策試験|素晴らしいAdvanced VMware Cloud Foundation 9.0 Automation日本語講座
我々に3V0-21.25参考書を利用したら、大量の時間と精力が必要ではありません。弊社の問題集の的中率が高いので、3V0-21.25参考書の内容を暗記すれば、試験に無事に合格できます。もし試験の中で内容が変更したら、お客様は半年の全額返金または一年の無料更新を選ぶことができます。3V0-21.25試験の合格は我々の保証です。
VMware Advanced VMware Cloud Foundation 9.0 Automation 認定 3V0-21.25 試験問題 (Q66-Q71):
質問 # 66
What should an Organization Administrator configure to ensure that three environments---staging, development, and production---are isolated from each other?
- A. Create a VPC for each environment with a connectivity profile that has only a ''Private -- TGW'' IPv4 block.
- B. Create a VPC for each environment and ensure no connectivity profiles are selected.
- C. Create a single VPC for both staging and development with a connectivity profile supporting multiple private CIDRs.
- D. Create a Namespace class for each environment, ensuring limits are configured.
正解:B
解説:
Each environment must be placed in a separate Virtual Private Cloud because the VPC forms the primary networking and security isolation boundary. Creating independent VPCs for staging, development, and production prevents the environments from sharing the same VPC routing domain, subnets, and security context.
A connectivity profile defines the common northbound connectivity configuration available to a VPC. When no connectivity profile is selected, the VPC is not attached to connectivity services that could provide routed access to other VPCs or external networks. Workloads can communicate within their own VPC, but there is no configured inter-VPC path between the three environments.
The Private--TGW option is unsuitable for strict isolation. A Transit Gateway provides inter-VPC communication, and private-TGW address blocks supply addresses for subnets whose scope extends across VPCs connected to that Transit Gateway. Creating one VPC for staging and development would also place both environments within the same isolation boundary.
Namespace classes control resource specifications and limits for vSphere namespaces; they do not establish network isolation or prevent communication between environments.
質問 # 67
During a peer review, a developer accidentally committed a YAML manifest containing a plaintext API token, triggering a security alert and raising concerns about the current handling of sensitive values in infrastructure code.
The development team uses an All Apps Organization in VMware Cloud Foundation (VCF) Automation and must adhere to security guidelines while minimizing manual steps in the processes.
Which approach to manage, store, and distribute sensitive data supports secure automation workflows for Supervisor and vSphere Kubernetes Service (VKS) clusters in VCF Automation?
- A. Use the Secret Store Service (SSS) and reference the required secrets during deployment.
- B. Store secrets in the YAML manifest files in Git, but mark the Git repository as private to limit exposure.
- C. Store secrets in a private Git repository and use environment-variable substitution in the CI/CD pipeline to inject them into blueprints at build time.
- D. Pass secrets as secure input variables during deployments from VCF Automation's UI, so the sensitive values are never included directly in blueprints.
正解:A
解説:
V7.5
Secret Store Service is the purpose-built VCF service for centrally storing, controlling, and distributing sensitive information. It uses OpenBao to protect secrets and supports workloads running directly on Supervisor and within VKS clusters. Kubernetes service accounts authenticate workloads to the service, allowing authorized pods to retrieve or receive secrets dynamically.
The deployment manifest contains a reference to the required secret rather than the plaintext token. This removes sensitive values from Git history, blueprint source, and routine CI/CD output. Access can be restricted according to workload identity and namespace, while secrets can be centrally rotated without editing and recommitting every application manifest.
Secure UI inputs avoid embedding a value in a blueprint but still require manual entry during deployment and do not provide centralized lifecycle management for Supervisor and VKS workloads. Private Git repositories do not make plaintext secret storage safe; repository administrators, compromised credentials, build logs, or historical commits can still expose the values. Environment-variable substitution similarly moves the exposure point into the pipeline rather than eliminating it.
Study Guide references: Installing and Configuring Secret Store Service , Inject Secrets into Pods on VKS Clusters , and Managing Secrets in vSphere Supervisor Workloads .
質問 # 68
A design requirement for a new VCF 9.0 deployment specifies that all tenant network traffic must be inspected by a centralized firewall appliance located in a "Security" VPC before reaching the internet.
Which NSX VPC feature should be used to support this "Service Chaining" requirement?
- A. VPC Ingress Profiles
- B. Distributed Firewall (DFW) Exclusion List
- C. Static Routes with Next-Hop to an Interface IP
- D. Default Outbound NAT
正解:C
解説:
To support centralized security inspection or "Service Chaining" in VCF 9.0, administrators leverage the routing flexibility of the NSX VPC. By configuring Static Routes within the tenant VPC, the administrator can override the default system-generated path to the internet. Specifically, the "0.0.0.0/0" (Default Route) can be pointed to the Interface IP of a security appliance or a load balancer residing within a shared or dedicated Security VPC. This forces all egress traffic from the application VPC to transit through the security layer for deep packet inspection or logging before the Transit Gateway forwards it to the external network.
While the Distributed Firewall (Option C) provides micro-segmentation, it does not redirect traffic to external appliances; only custom routing logic-managed through the VPC's routing table-can satisfy the requirement for centralized service insertion in a multi-VPC regional design.
質問 # 69
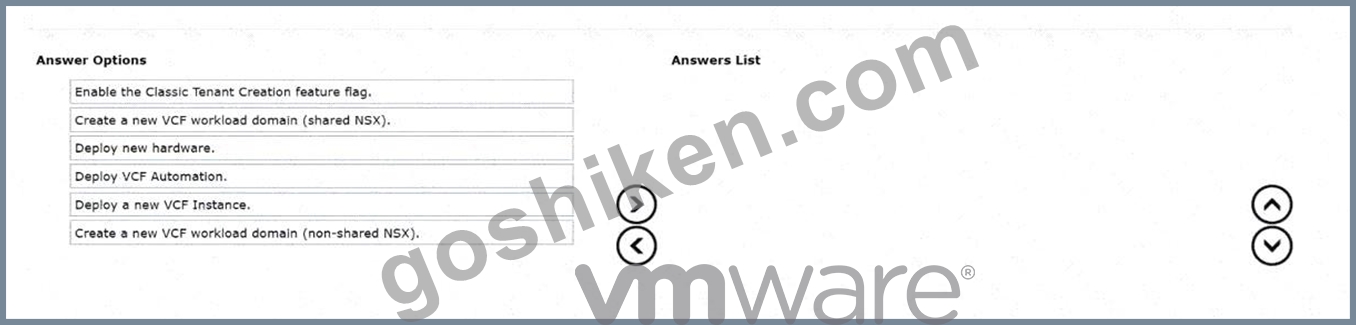
An administrator has been tasked with creating a new organization for VM Apps within an existing VMware Cloud Foundation (VCF) Fleet with minimal operational overhead.
The existing VCF fleet already has an organization for All Apps configured.
Drag and drop the three actions from the Answer Options to the Answers List, in any order, that the administrator needs to perform to complete the objective (Choose three.)
正解:
解説:
Explanation:
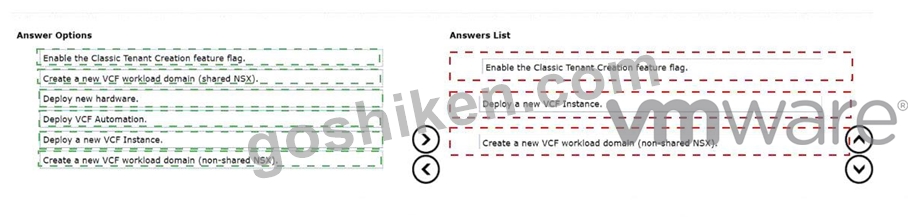
To create a new VM Apps organization with minimal operational overhead in a VCF fleet that already hosts an All Apps organization, select the following three actions:
Answers List
Enable the Classic Tenant Creation feature flag.
Deploy a new VCF Instance.
Create a new VCF workload domain (non-shared NSX).
In VMware Cloud Foundation (VCF) 9.0 , the platform defaults to the modern AllApps (AIIApps) architectural model, which centers on Virtual Private Clouds (VPCs) and Supervisor-integrated networking. To introduce a VMApps Organization -the " classic " tenant model for traditional virtual machines-into this environment while maintaining minimal overhead, the administrator must first Enable the Classic Tenant Creation feature flag . This toggle exposes the legacy workflows necessary to provision organizations that do not rely on the VPC framework.
Furthermore, VMApps organizations typically require their own isolated networking and compute boundaries to avoid conflict with the modern VPC Transit Gateway architecture. Consequently, the administrator should Create a new VCF workload domain (non-shared NSX). Using a non-shared NSX manager ensures that the traditional segments and load-balancing services used by VM-centric workloads are logically and technically segregated from the container-optimized fabric of the AllApps organization. Finally, for a " fleet " approach, Deploying a new VCF Instance (or management block) provides the clean, dedicated infrastructure needed to host these legacy-style organizations with the highest degree of administrative isolation, ensuring that new VM-centric tenants do not consume resources or cause configuration drift within the existing AllApps environment.
質問 # 70
An Organization Administrator notices that their public assigned IPs are being used for non-production workloads.
What should the administrator do to prevent further public IP addresses consumption?
- A. Modify the default IP Quota that was shared by the provider.
- B. Create an IP Quota and associate it with the non-production VPC.
- C. Modify the existing VPC and remove the "External IPv4 blocks".
- D. Create an IP Quota and associate it with the non-production namespace.
正解:B
解説:
In the VCF 9.0 networking model, IP Quotas are the primary governance mechanism for controlling resource consumption within an Organization. When a Provider allocates IP blocks to an Organization, the Organization Administrator is responsible for sub-allocating those resources to individual projects or environments. To prevent non-production workloads from exhausting the pool of public (external) IP addresses, the administrator must Create an IP Quota specifically for the non-production Virtual Private Cloud (VPC). This quota defines the maximum number of public IP addresses that can be used for services such as Load Balancers or NAT rules within that specific VPC. Once the quota is reached, any further requests for public IPs in that VPC will be denied by the VCF Automation engine, ensuring that a sufficient supply remains available for production-critical workloads. Modifying the provider-shared quota (Option C) would affect the entire organization, and removing external blocks (Option D) would break existing connectivity rather than provide proactive governance.
質問 # 71
......
VMwareのAdvanced VMware Cloud Foundation 9.0 Automationガイド急流で試験に合格できない場合は、全額返金されます。 クライアントのみが試験証明書とスキャンコピーまたは3V0-21.25試験の不合格スコアのスクリーンショットを提供した場合、すぐにクライアントに返金します。 払い戻しの手順は非常に簡単です。 3V0-21.25試験問題についてGoShikenクライアントに問題や疑念がある場合は、メールを送信するか、オンラインでお問い合わせください。できるだけ早くクライアントの問題に返信して解決します。
3V0-21.25日本語講座: https://www.goshiken.com/VMware/3V0-21.25-mondaishu.html
- 試験3V0-21.25日本語対策 - 素敵な3V0-21.25日本語講座 | 大人気3V0-21.25模擬モード 🌠 最新➽ 3V0-21.25 🢪問題集ファイルは➡ www.xhs1991.com ️⬅️にて検索3V0-21.25試験攻略
- 3V0-21.25技術問題 🎽 3V0-21.25出題範囲 🌜 3V0-21.25復習教材 🐶 ▷ www.goshiken.com ◁サイトで[ 3V0-21.25 ]の最新問題が使える3V0-21.25試験攻略
- 3V0-21.25関連資格知識 ↙ 3V0-21.25問題サンプル ❔ 3V0-21.25模擬資料 🤒 [ www.goshiken.com ]で{ 3V0-21.25 }を検索して、無料でダウンロードしてください3V0-21.25復習教材
- 3V0-21.25合格問題 💥 3V0-21.25テスト難易度 🥕 3V0-21.25関連資格知識 🐈 ▷ www.goshiken.com ◁で✔ 3V0-21.25 ️✔️を検索し、無料でダウンロードしてください3V0-21.25日本語版
- 3V0-21.25関連試験 🧇 3V0-21.25日本語版 🏪 3V0-21.25関連試験 🪑 “ www.shikenpass.com ”の無料ダウンロード⏩ 3V0-21.25 ⏪ページが開きます3V0-21.25復習教材
- 3V0-21.25試験の準備方法|素敵な3V0-21.25日本語対策試験|実際的なAdvanced VMware Cloud Foundation 9.0 Automation日本語講座 📆 サイト☀ www.goshiken.com ️☀️で➽ 3V0-21.25 🢪問題集をダウンロード3V0-21.25テスト難易度
- 試験の準備方法-信頼的な3V0-21.25日本語対策試験-認定する3V0-21.25日本語講座 🗯 「 www.passtest.jp 」は、➤ 3V0-21.25 ⮘を無料でダウンロードするのに最適なサイトです3V0-21.25模擬資料
- 3V0-21.25認定デベロッパー ▛ 3V0-21.25難易度受験料 🛌 3V0-21.25練習問題集 🐗 ⇛ www.goshiken.com ⇚を入力して▷ 3V0-21.25 ◁を検索し、無料でダウンロードしてください3V0-21.25練習問題集
- 3V0-21.25技術問題 🔔 3V0-21.25日本語版受験参考書 🌗 3V0-21.25資格問題集 🍄 ⏩ www.shikenpass.com ⏪の無料ダウンロード➥ 3V0-21.25 🡄ページが開きます3V0-21.25練習問題集
- 3V0-21.25日本語版 ❤ 3V0-21.25日本語関連対策 😜 3V0-21.25日本語版 ‼ 「 www.goshiken.com 」サイトにて✔ 3V0-21.25 ️✔️問題集を無料で使おう3V0-21.25技術問題
- 最新の3V0-21.25日本語対策を今すぐダウンロード 💙 「 www.it-passports.com 」で使える無料オンライン版「 3V0-21.25 」 の試験問題3V0-21.25模擬資料
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, estar.jp, ronorp.net, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes
P.S. GoShikenがGoogle Driveで共有している無料かつ新しい3V0-21.25ダンプ:https://drive.google.com/open?id=1PV20So1lhbyK2Un3PcAELjT0Vmo6Xuh2


 icons at the top
right corner of the subsection.