NSE4_FGT_AD-7.6덤프최신버전, NSE4_FGT_AD-7.6시험대비 최신 덤프문제, NSE4_FGT_AD-7.6 PDF, NSE4_FGT_AD-7.6최신 인증시험 기출문제, NSE4_FGT_AD-7.6유효한 공부문제

DumpTOP NSE4_FGT_AD-7.6 최신 PDF 버전 시험 문제집을 무료로 Google Drive에서 다운로드하세요: https://drive.google.com/open?id=1QA3oAorXCy4KNAZBKYXhvofXwQoADnDd
만약 아직도 우리를 선택할지에 대하여 망설이고 있다면. 우선은 우리 사이트에서 DumpTOP가 제공하는 무료인 일부 문제와 답을 다운하여 체험해보시고 결정을 내리시길 바랍니다.그러면 우리의 덤프에 믿음이;갈 것이고,우리 또한 우리의 문제와 답들은 무조건 100%통과 율로 아주 고득점으로Fortinet인증NSE4_FGT_AD-7.6험을 패스하실 수 있습니다,
Fortinet NSE4_FGT_AD-7.6 Exam Overview:
| Certification Vendor: |
Fortinet |
| Exam Name: |
Fortinet NSE 4 - FortiOS 7.6 Administrator |
| Exam Number: |
NSE4_FGT_AD-7.6 |
| Available Languages: |
French, Japanese, Korean, English, Brazilian Portuguese, Spanish |
| Exam Duration: |
90 minutes |
| Certificate Validity Period: |
3 years |
| Exam Format: |
Applied configuration & troubleshooting, Scenario-based questions, Multiple choice |
| Passing Score: |
Pass/Fail (approx. 70% standard) |
| Related Certifications: |
FCP in SASE
FCP in Secure Networking
FCP in Security Operations
FCP in Cloud Security |
| Real Exam Qty: |
50–55 |
| Exam Price: |
$200 USD |
| Recommended Training: |
FortiOS 7.6 Administrator Self-Paced Course |
| Exam Registration: |
Pearson VUE Registration |
| Sample Questions: |
Fortinet NSE4_FGT_AD-7.6 Sample Questions |
| Exam Way: |
Proctored online or onsite via Pearson VUE |
| Pre Condition: |
No formal prerequisites; recommended: basic networking knowledge, hands-on FortiGate experience, FortiGate Operator & Administrator training |
| Official Syllabus URL: |
https://training.fortinet.com/local/staticpage/view.php?page=nse4_fgt_ad_7_6 |
>> NSE4_FGT_AD-7.6덤프최신버전 <<
NSE4_FGT_AD-7.6덤프최신버전 최신 시험대비자료
최근 더욱 많은 분들이Fortinet인증NSE4_FGT_AD-7.6시험에 도전해보려고 합니다. DumpTOP에서는 여러분들의 시간돠 돈을 절약해드리기 위하여 저렴한 가격에 최고의 품질을 지닌 퍼펙트한Fortinet인증NSE4_FGT_AD-7.6시험덤플르 제공해드려 고객님의 시험준비에 편안함을 선물해드립니다. DumpTOP제품을 한번 믿어보세요.
Fortinet NSE4_FGT_AD-7.6 시험요강:
| 주제 |
소개 |
| 주제 1 |
- Deployment and System Configuration: This domain covers initial FortiGate setup, logging configuration and troubleshooting, FGCP HA cluster configuration, resource and connectivity diagnostics, FortiGate cloud deployments (CNF and VM), and FortiSASE administration with user onboarding.
|
| 주제 2 |
- Firewall Policies and Authentication: This domain focuses on creating firewall policies, configuring SNAT and DNAT for address translation, implementing various authentication methods, and deploying FSSO for user identification.
|
| 주제 3 |
- Content Inspection: This domain addresses inspecting encrypted traffic using certificates, understanding inspection modes and web filtering, configuring application control, deploying antivirus scanning modes, and implementing IPS for threat protection.
|
| 주제 4 |
- VPN: This domain focuses on implementing meshed or partially redundant IPsec VPN topologies for secure connections.
|
| 주제 5 |
- Routing: This domain covers configuring static routes for packet forwarding and implementing SD-WAN to load balance traffic across multiple WAN links.
|
최신 Fortinet NSE 4 NSE4_FGT_AD-7.6 무료샘플문제 (Q86-Q91):
질문 # 86
An administrator wanted to configure an IPS sensor to block traffic that triggers a signature set number of times during a specific time period.
How can the administrator achieve the objective?
- A. Use IPS filter, rate-mode periodical option.
- B. Use IPS filter, rate-mode periodical option.
- C. Use IPS group signatures, set rate-mode 60.
- D. Use IPS packet logging option with periodical filter option.
정답:A
설명:
The IPS filter with the rate-mode set to "periodical" allows the administrator to block traffic that triggers a signature a specified number of times within a defined time period, meeting the requirement.
질문 # 87
You have configured the FortiGate device for FSSO. A user is successful in log-in to windows, but their access to the internet is denied. What should the administrator check first?
- A. The windows event viewer for failed login attempts.
- B. The FortiGate firewall policy settings for SSL decryption.
- C. The FortiGate FSSO active users list for user's IP address.
- D. Whether the user is assigned to the correct AD group.
정답:C
설명:
Checking the active users list verifies if FortiGate correctly associates the user with their IP address, ensuring proper policy enforcement for internet access.
질문 # 88
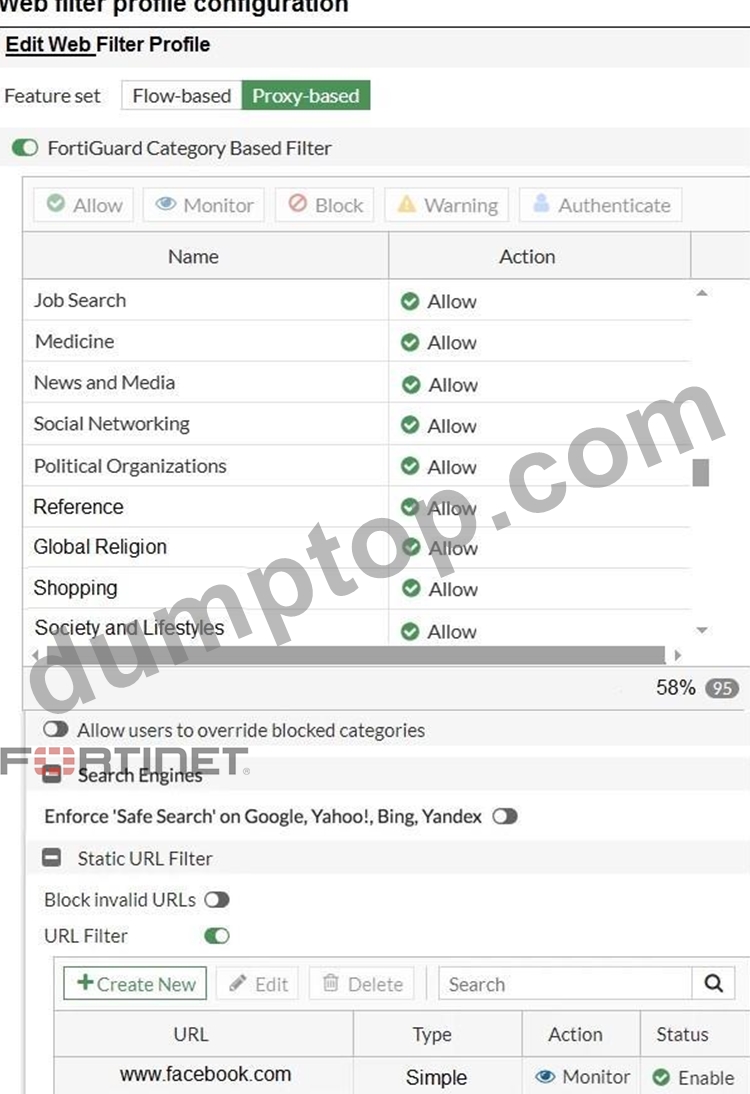
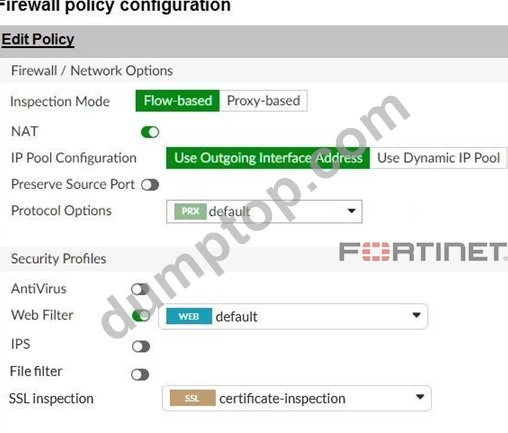
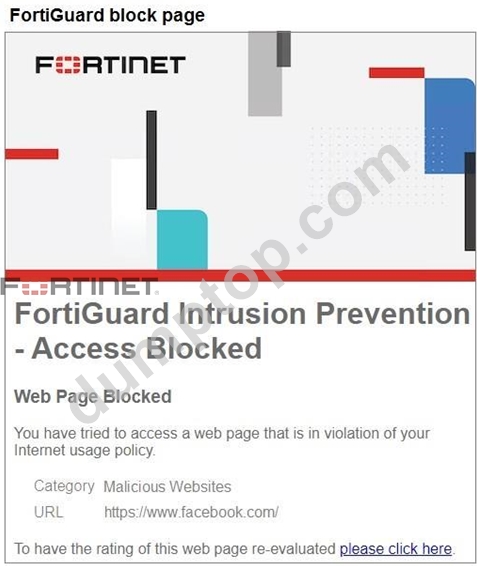
Refer to the exhibits. A web filter profile configuration and firewall policy configuration are shown.
You are trying to access www.facebook.com, but you are redirected to a FortiGuard web filtering block page.
Based on the exhibits, what is the possible cause of the issue?
- A. The web filter profile feature set is configured incorrectly.
- B. The web rating override configuration is incorrect.
- C. The firewall policy inspection mode is incorrect.
- D. For www.facebook.com, the URL filter action is incorrect.
정답:B
설명:
The web filter profile shows a URL filter override for www.facebook.com with action Monitor, which should allow access. However, the block page shows FortiGuard categorizing www.facebook.com as Malicious Websites and blocking it. This indicates that the web rating override configuration is incorrect (the override is not applied properly), so FortiGuard's default category action takes precedence and blocks the site.
질문 # 89
What are three key routing principles in SD-WAN? (Choose three answers)
- A. SD-WAN rules have precedence over any other type of routes.
- B. By default, SD-WAN rules are skipped if the included SD-WAN members do not have a valid route to the destination.
- C. Regular policy routes have precedence over SD-WAN rules.
- D. By default, SD-WAN rules are skipped if only one route to the destination is available.
- E. By default, SD-WAN rules are skipped if the best route to the destination is not an SD-WAN member.
정답:B,C,E
설명:
"This slide shows the SD-WAN rule lookup process. SD-WAN rules are essentially policy routes."
"FortiGate performs a forwarding information base (FIB) lookup for the packet destination IP (dstip). If the resolved interface for the fib-best-match isn't an SD-WAN member, then FortiGate moves on to the next rule.
This behavior follows the key routing principle: SD-WAN rules are skipped if the best route to the destination isn't an SD-WAN member ."
"If the resolved interface is an SD-WAN member, then FortiGate looks for one or more acceptable members in the oif list... An acceptable member is an alive member that has a route to the destination. This behavior follows the key routing principle: SD-WAN rules are skipped if none of the configured members in the rule have a valid route to the destination ."
"Because regular policy routes have precedence over any other routes..."
"Also note that policy routes have precedence over SD-WAN rules, and over any routes in the FIB." Technical Deep Dive:
The correct answers are A, C, and E .
A is correct because an SD-WAN rule is not enough by itself. A selected member must also be alive and have a valid route to the destination. If none of the members referenced by the rule can actually reach the destination, the rule is skipped.
C is correct because a regular policy route is evaluated before SD-WAN rules. This is a classic exam trap.
FortiGate treats SD-WAN steering like policy-route logic, but standard policy routes still win if they match and are valid.
E is correct because FortiGate first checks the FIB best match . If that best route resolves to an interface that is not an SD-WAN member, FortiGate skips the SD-WAN rule and continues.
Why the others are wrong:
B is false because SD-WAN rules do not have precedence over everything; regular policy routes do.
D is false because the number of available routes is not the deciding rule. Even with only one route, SD-WAN can still steer traffic if the routing and member conditions are met.
Operationally, think of SD-WAN routing in this order: policy route check # SD-WAN rule lookup # standard FIB fallback . On FortiGate, the practical validation commands are:
get router info routing-table all
diagnose sys sdwan service
diagnose firewall proute list
That combination lets you confirm whether a packet is being captured by a policy route, whether an SD-WAN rule has acceptable members, and what the FIB currently resolves for the destination.
질문 # 90
Refer to the exhibit.
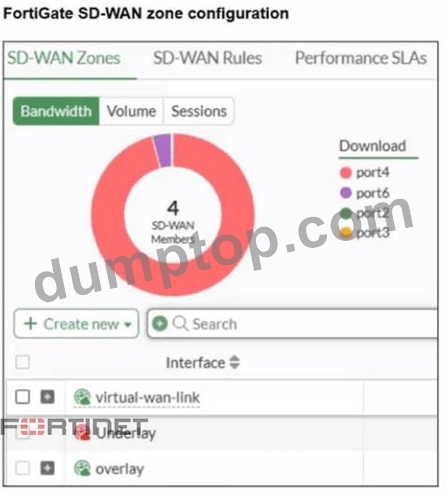
An SD-WAN zone configuration on the FortiGate GUI is shown. Based on the exhibit, which statement is true?
- A. The Underlay zone is the zone by default.
- B. port2 and port3 are not assigned to a zone.
- C. The virtual-wan-link and overlay zones can be deleted
- D. The Underlay zone contains no member.
정답:D
설명:
According to the FortiOS 7.6 Administrator Guide and the specific behavior of the SD-WAN GUI, here is the technical breakdown:
SD-WAN Zone Hierarchy and UI Elements: In the FortiGate GUI, SD-WAN zones that contain member interfaces are displayed with a plus (+) icon next to the checkbox. This icon allows administrators to expand the zone and view the specific physical or logical interfaces assigned to it.
Analysis of the "Underlay" Zone: In the provided exhibit, the virtual-wan-link and overlay zones both feature the plus (+) expansion icon, indicating they have active members. The Underlay zone, however, lacks this icon and displays a red status icon. This is the visual indicator in FortiOS that the zone is currently empty and contains no member interfaces.
Mandatory Zone Membership: In FortiOS 7.x, every SD-WAN member interface must be assigned to a zone. It is not possible for an interface to be an "SD-WAN member" (as shown in the legend with port2 and port3) without being assigned to a zone. Since port2 and port3 are listed in the legend, they are indeed assigned to one of the other expanded zones (likely virtual-wan-link or overlay), making Option D incorrect.
Default Zone Behavior: While FortiOS 7.6 often creates default zones like virtual-wan-link, underlay, and overlay during certain configuration wizards or by default in newer versions, they are distinct entities. There is no single "default" zone that acts as a global catch-all in the way Option C suggests.
Immutability of System Zones: While certain system-defined zones have restrictions, the primary focus of this specific exhibit is the current membership state, which clearly shows the Underlay zone is empty.
질문 # 91
......
NSE4_FGT_AD-7.6시험대비 최신 덤프문제: https://www.dumptop.com/Fortinet/NSE4_FGT_AD-7.6-dump.html
- 적중율 좋은 NSE4_FGT_AD-7.6덤프최신버전 덤프 📎 ( www.dumptop.com )을(를) 열고{ NSE4_FGT_AD-7.6 }를 입력하고 무료 다운로드를 받으십시오NSE4_FGT_AD-7.6유효한 최신버전 덤프
- NSE4_FGT_AD-7.6시험패스 가능한 인증덤프 🥌 NSE4_FGT_AD-7.6시험패스 인증덤프문제 ➕ NSE4_FGT_AD-7.6최신 시험 기출문제 모음 💓 검색만 하면[ www.itdumpskr.com ]에서➡ NSE4_FGT_AD-7.6 ️⬅️무료 다운로드NSE4_FGT_AD-7.6유효한 최신버전 덤프
- 시험준비에 가장 좋은 NSE4_FGT_AD-7.6덤프최신버전 최신 덤프모음집 👛 검색만 하면( www.exampassdump.com )에서⇛ NSE4_FGT_AD-7.6 ⇚무료 다운로드NSE4_FGT_AD-7.6높은 통과율 덤프공부자료
- NSE4_FGT_AD-7.6시험유형 🏬 NSE4_FGT_AD-7.6최신 업데이트 덤프자료 🚂 NSE4_FGT_AD-7.6시험패스보장덤프 👿 ➽ www.itdumpskr.com 🢪에서《 NSE4_FGT_AD-7.6 》를 검색하고 무료 다운로드 받기NSE4_FGT_AD-7.6인증시험공부
- 퍼펙트한 NSE4_FGT_AD-7.6덤프최신버전 덤프문제 🚌 시험 자료를 무료로 다운로드하려면▷ www.dumptop.com ◁을 통해[ NSE4_FGT_AD-7.6 ]를 검색하십시오NSE4_FGT_AD-7.6시험패스 인증덤프문제
- NSE4_FGT_AD-7.6시험유형 🚶 NSE4_FGT_AD-7.6시험패스 인증덤프문제 💖 NSE4_FGT_AD-7.6높은 통과율 덤프공부자료 🔄 무료 다운로드를 위해⇛ NSE4_FGT_AD-7.6 ⇚를 검색하려면✔ www.itdumpskr.com ️✔️을(를) 입력하십시오NSE4_FGT_AD-7.6인기덤프문제
- NSE4_FGT_AD-7.6시험덤프자료 🆕 NSE4_FGT_AD-7.6퍼펙트 덤프 최신 데모 😄 NSE4_FGT_AD-7.6시험패스보장덤프 👠 ➥ NSE4_FGT_AD-7.6 🡄를 무료로 다운로드하려면⮆ www.koreadumps.com ⮄웹사이트를 입력하세요NSE4_FGT_AD-7.6인기덤프문제
- 최신 NSE4_FGT_AD-7.6덤프최신버전 시험공부자료 🚻 { NSE4_FGT_AD-7.6 }를 무료로 다운로드하려면▛ www.itdumpskr.com ▟웹사이트를 입력하세요NSE4_FGT_AD-7.6인기덤프문제
- NSE4_FGT_AD-7.6최신 시험덤프자료 🔼 NSE4_FGT_AD-7.6시험패스 덤프공부자료 🔔 NSE4_FGT_AD-7.6인기덤프문제 👎 무료 다운로드를 위해▶ NSE4_FGT_AD-7.6 ◀를 검색하려면▛ www.exampassdump.com ▟을(를) 입력하십시오NSE4_FGT_AD-7.6시험유형
- 시험준비에 가장 좋은 NSE4_FGT_AD-7.6덤프최신버전 최신버전 덤프샘플 문제 💜 ➥ www.itdumpskr.com 🡄의 무료 다운로드【 NSE4_FGT_AD-7.6 】페이지가 지금 열립니다NSE4_FGT_AD-7.6최신 덤프문제보기
- NSE4_FGT_AD-7.6인증시험공부 🥼 NSE4_FGT_AD-7.6최신 시험덤프자료 🛶 NSE4_FGT_AD-7.6최신 시험덤프자료 🌖 오픈 웹 사이트✔ www.koreadumps.com ️✔️검색➤ NSE4_FGT_AD-7.6 ⮘무료 다운로드NSE4_FGT_AD-7.6시험패스 인증덤프문제
-
www.stes.tyc.edu.tw, www.intensedebate.com, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes
DumpTOP NSE4_FGT_AD-7.6 최신 PDF 버전 시험 문제집을 무료로 Google Drive에서 다운로드하세요: https://drive.google.com/open?id=1QA3oAorXCy4KNAZBKYXhvofXwQoADnDd


 icons at the top
right corner of the subsection.