NSE6_OTS_AR-7.6試験準備, NSE6_OTS_AR-7.6模試エンジン, NSE6_OTS_AR-7.6学習資料, NSE6_OTS_AR-7.6日本語版試験勉強法, NSE6_OTS_AR-7.6試験内容

我々JpexamはFortinetのNSE6_OTS_AR-7.6試験問題集をリリースする以降、多くのお客様の好評を博したのは弊社にとって、大変な名誉なことです。また、我々はさらに認可を受けられるために、皆様の一切の要求を満足できて喜ぶ気持ちでずっと協力し、完備かつ精確のNSE6_OTS_AR-7.6試験問題集を開発するのに準備します。
Fortinet NSE6_OTS_AR-7.6 認定試験の出題範囲:
| トピック |
出題範囲 |
| トピック 1 |
- 資産管理:OT規格の理解と、Fortinetが産業環境におけるコンプライアンス要件にどのように適合しているかについて説明します。また、Fortinet Security Fabricを使用した資産管理、およびFortiGateとFortiNACを使用したデバイス検出の実装についても説明します。
|
| トピック 2 |
- ネットワークセキュリティ:産業用プロトコルに特化したセキュリティ検査の適用方法と、脆弱なシステムを保護するための仮想パッチの実装方法について説明します。また、脅威対応と運用効率を向上させるための自動化の設定方法についても解説します。
|
| トピック 3 |
- 監視とリスク評価:FortiAnalyzerでイベントハンドラーを作成し、ネットワークアクティビティを監視して脅威を検出する方法について説明します。また、リスク評価の実施やセキュリティレポートの分析を行い、継続的なリスク管理を支援する方法についても解説します。
|
| トピック 4 |
- ネットワークアクセス制御:OTイーサネットの基本原理と、安全なネットワークセグメンテーション戦略の設計に焦点を当てます。また、OTネットワークへのアクセスを制御および検証するための認証方法の設定も含まれます。
|
>> NSE6_OTS_AR-7.6試験準備 <<
認定する-便利なNSE6_OTS_AR-7.6試験準備試験-試験の準備方法NSE6_OTS_AR-7.6模試エンジン
NSE6_OTS_AR-7.6学習教材を選択し、当社の製品を適切に使用する場合、NSE6_OTS_AR-7.6試験に合格し、NSE6_OTS_AR-7.6認定を取得することをお約束します。そうすれば、あなたは段階的に社会的影響力と成功の大きなレベルに前進するチャンスがたくさんあることに気付くでしょう。 NSE6_OTS_AR-7.6ガイド急流は、NSE6_OTS_AR-7.6試験問題を確認できるコンサートを除外するために、すべての受験者に無料デモを提供することもできます。 NSE6_OTS_AR-7.6学習ガイドがお気に召されると思います。
Fortinet NSE 6 - OT Security 7.6 Architect 認定 NSE6_OTS_AR-7.6 試験問題 (Q66-Q71):
質問 # 66
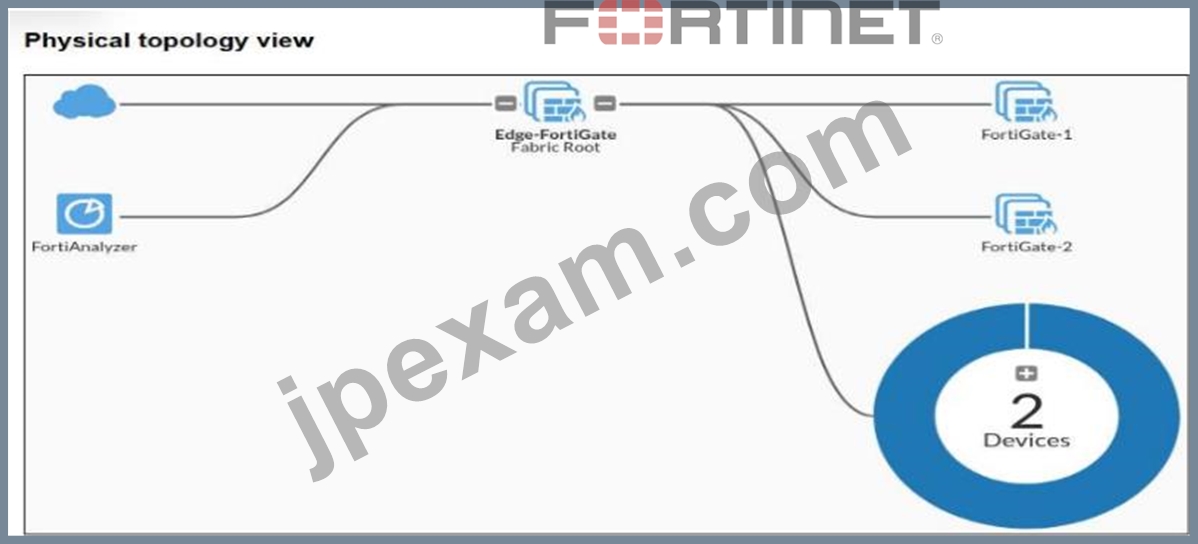
Refer to the exhibit.
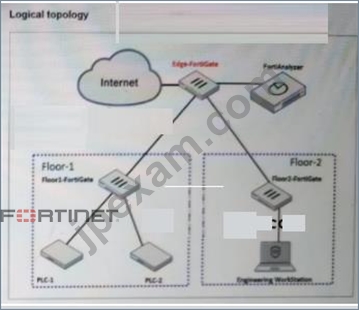
A partial OT network is shown. You want to configure an automated alert sent by FortiAnalyzer when an attack occurs on a FortiGate device. Which two configurations must you implement? (Choose two answers)
- A. You must configure an event handler on FortiAnalyzer.
- B. You must configure an intrusion prevention security profile on all FortiGate devices.
- C. You must configure a stitch on the root FortiGate.
- D. You must configure a LOCALHOST task in the FortiAnalyzer playbook.
正解:A、C
解説:
The correct answers are A and D. The study guide provides a direct use case called Attack Detection and Automated Alert. It states: "A downstream FortiGate detects an attack and sends logs to FortiAnalyzer. FortiAnalyzer parses the logs and notifies the root FortiGate. The root FortiGate triggers the action, which in this case, is a notification to the administrator." The same slide also explicitly shows "Stitches configured on root FortiGate." This confirms that to send the automated alert, you must configure the automation stitch on the root FortiGate.
The second required configuration is an event handler on FortiAnalyzer. The guide explains that "Event handlers generate events" and that "FortiAnalyzer uses event handlers to filter all incoming logs. If logs match the conditions configured in an event handler, FortiAnalyzer generates an event." Since FortiAnalyzer must detect the attack from the received logs before notifying the root FortiGate, an event handler is required on FortiAnalyzer.
Option B is incorrect because the study guide does not identify a LOCALHOST task as the required configuration for this attack-alert flow. Option C is also incorrect because the question asks what must be configured to enable the automated alert workflow. An IPS profile may detect some attacks, but the required automation path in the study guide is specifically event handler on FortiAnalyzer + stitch on the root FortiGate.
質問 # 67
How can you achieve remote access and internel availability in an OT network?
- A. Create more access policies to prevent unauthorized access.
- B. Add additional internal firewalls to access OT devices.
- C. Implement SD-WAN to manage traffic on each ISP link.
- D. Create a back-end backup network as a redundancy measure.
正解:C
解説:
SD-WAN provides reliable and efficient management of multiple ISP links, ensuring high availability and optimized traffic routing.
It offers redundancy and performance improvements critical for OT networks where continuous availability is essential.
SD-WAN can dynamically route traffic, maintain session persistence, and provide secure connectivity between remote and internal OT environments.
質問 # 68
Refer to the exhibits.
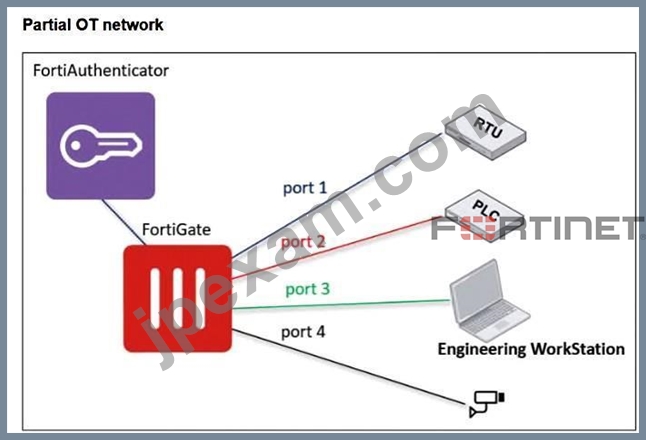
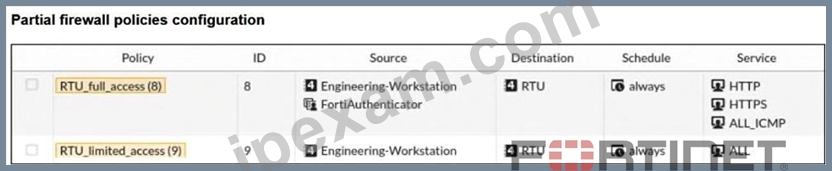
A partial OT network and firewall policies configuration are shown.
You added authentication in the firewall policy from Engineering Workstation to RTU to improve the security. When verifying your configuration, you notice that you can still access RTU from Engineering Workstation without an authentication prompt.
What must you do to enforce authentication?
- A. You must reboot FortiGate.
- B. You must add authentication in firewall policy 9.
- C. You must enable Fortinet Single Sign-On (FSSO).
- D. You must add a local user instead of FortiAuthenticator.
正解:B
解説:
Firewall policies are evaluated top-down, and a matching policy without authentication is applied before the one requiring authentication. Adding authentication to the higher-priority policy ensures that all matching traffic is subject to authentication.
質問 # 69
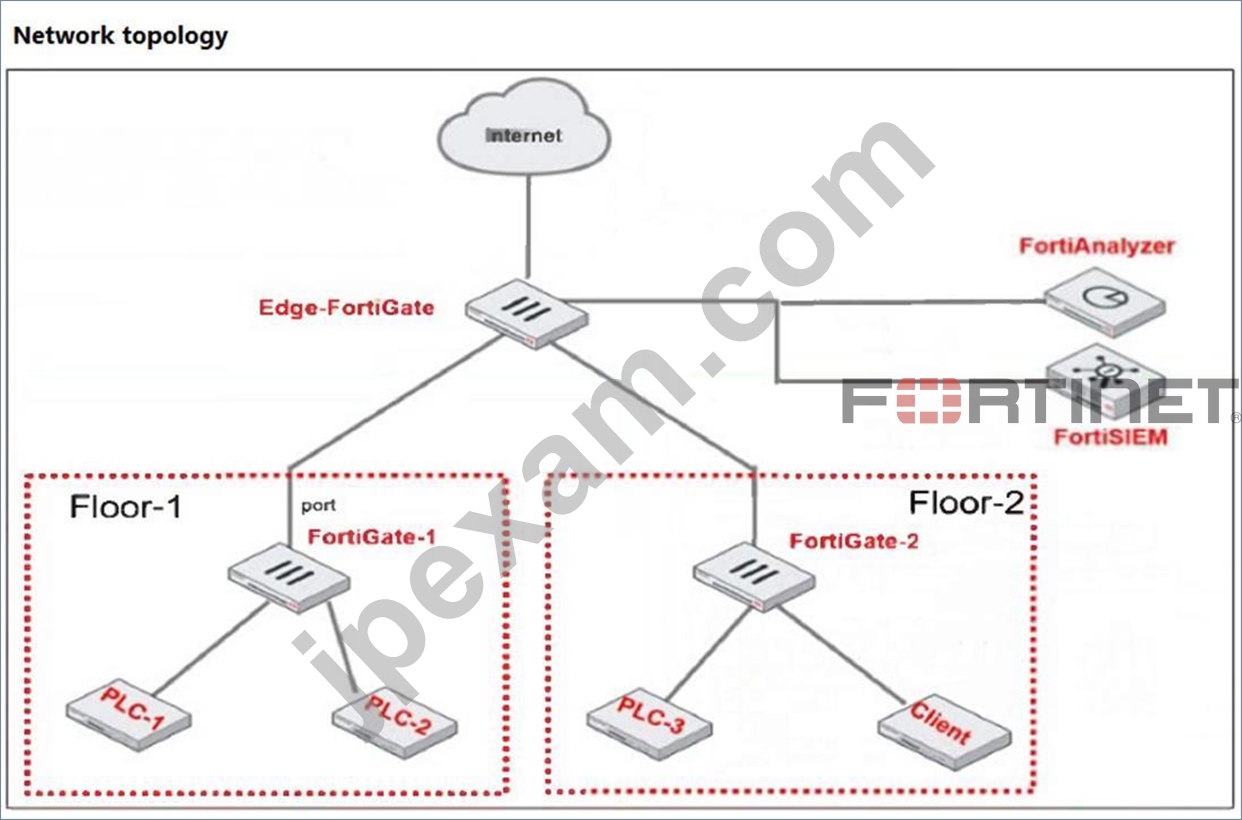
Refer to the exhibit. The network topology in the exhibit shows FortiGate devices as well as FortiAnalyzer and FortiSIEM for the OT network.
Which two steps must you take to configure logging on the OT network'? (Choose two.)
- A. Configure FortiAnalyzer to send security events to FortiSIEM.
- B. Configure FortiSIEM to send logs and alerts to FortiAnalyzer.
- C. Configure FortiGate to send logs to FortiAnalyzer and FortiSIEM.
- D. Configure FortiGate and FortiAnalyzer to send industrial signature patterns to FortiSIEM.
正解:A、C
解説:
FortiGates must forward their logs directly to both FortiAnalyzer and FortiSIEM for storage and correlation. FortiAnalyzer then forwards relevant security events to FortiSIEM, enabling centralized analytics across OT devices.
質問 # 70
Refer to the exhibit.
Why is the OT View tab not available in the Asset Identity Center section of the FortiGate-1 device? (Choose one answer)
- A. You must enable the Purdue Levels feature on the FortiGate-1 device.
- B. Device Detection is not enabled on the FortiGate-1 interface.
- C. The OT View tab is only available on the root FortiGate.
- D. You must enable Security Fabric Connection on the interfaces of the FortiGate-1 device.
正解:A
解説:
The correct answer is A. The study guide states that "The OT view is not available by default. You must enable it in the Feature Visibility section of the GUI or using the CLI command shown on this slide" and shows config system settings → set gui-ot enable. It also says that "After you enable the feature, the Asset Identity Center contains an Asset Identity List tab and an OT View tab." This directly explains why the OT View tab is missing: the feature that enables the Purdue-style OT display has not been enabled yet.
The OT View is the view that displays devices in a Purdue diagram, and the Asset Identity List also shows the current Purdue level for each device. Because the answer options do not explicitly say enable OT View in Feature Visibility, option A is the intended match, since it refers to enabling the Purdue-related OT display feature. Option B is incorrect because device detection affects visibility of devices, not whether the OT View tab exists. Option C is not supported by the study guide, and option D is also not given as the requirement for showing the OT View tab.
質問 # 71
......
JpexamのNSE6_OTS_AR-7.6参考書は間違いなくあなたが一番信頼できるNSE6_OTS_AR-7.6試験に関連する資料です。まだそれを信じていないなら、すぐに自分で体験してください。そうすると、きっと私の言葉を信じるようになります。Jpexamのサイトをクリックして問題集のデモをダウンロードすることができますから、ご利用ください。PDF版でもソフト版でも提供されていますから、先ず体験して下さい。問題集の品質を自分自身で確かめましょう。
NSE6_OTS_AR-7.6模試エンジン: https://www.jpexam.com/NSE6_OTS_AR-7.6_exam.html
- NSE6_OTS_AR-7.6試験の準備方法 | 有難いNSE6_OTS_AR-7.6試験準備試験 | 検証するFortinet NSE 6 - OT Security 7.6 Architect模試エンジン ⛵ 「 www.xhs1991.com 」サイトで☀ NSE6_OTS_AR-7.6 ️☀️の最新問題が使えるNSE6_OTS_AR-7.6受験トレーリング
- NSE6_OTS_AR-7.6資格模擬 🍎 NSE6_OTS_AR-7.6資格復習テキスト 🔦 NSE6_OTS_AR-7.6試験合格攻略 🌾 ➥ www.goshiken.com 🡄の無料ダウンロード【 NSE6_OTS_AR-7.6 】ページが開きますNSE6_OTS_AR-7.6合格内容
- 真実的なNSE6_OTS_AR-7.6試験準備試験-試験の準備方法-高品質なNSE6_OTS_AR-7.6模試エンジン 👽 サイト⮆ www.goshiken.com ⮄で( NSE6_OTS_AR-7.6 )問題集をダウンロードNSE6_OTS_AR-7.6合格記
- NSE6_OTS_AR-7.6全真問題集 🦟 NSE6_OTS_AR-7.6試験問題解説集 ⬛ NSE6_OTS_AR-7.6試験問題解説集 🌖 検索するだけで▷ www.goshiken.com ◁から{ NSE6_OTS_AR-7.6 }を無料でダウンロードNSE6_OTS_AR-7.6資格模擬
- NSE6_OTS_AR-7.6試験内容 🖱 NSE6_OTS_AR-7.6資格模擬 🌽 NSE6_OTS_AR-7.6専門知識内容 ☎ 最新▶ NSE6_OTS_AR-7.6 ◀問題集ファイルは▷ www.it-passports.com ◁にて検索NSE6_OTS_AR-7.6一発合格
- NSE6_OTS_AR-7.6試験勉強過去問 😶 NSE6_OTS_AR-7.6日本語版サンプル 💹 NSE6_OTS_AR-7.6一発合格 🐃 ( www.goshiken.com )の無料ダウンロード➥ NSE6_OTS_AR-7.6 🡄ページが開きますNSE6_OTS_AR-7.6日本語復習赤本
- ハイパスレートのNSE6_OTS_AR-7.6試験準備と認定したNSE6_OTS_AR-7.6模試エンジン ↙ ➽ www.passtest.jp 🢪には無料の➠ NSE6_OTS_AR-7.6 🠰問題集がありますNSE6_OTS_AR-7.6試験合格攻略
- 真実的なNSE6_OTS_AR-7.6試験準備試験-試験の準備方法-高品質なNSE6_OTS_AR-7.6模試エンジン 🍗 サイト“ www.goshiken.com ”で[ NSE6_OTS_AR-7.6 ]問題集をダウンロードNSE6_OTS_AR-7.6試験合格攻略
- 検証するNSE6_OTS_AR-7.6試験準備 | 最初の試行で簡単に勉強して試験に合格する - 完璧なFortinet Fortinet NSE 6 - OT Security 7.6 Architect 🟧 ➠ NSE6_OTS_AR-7.6 🠰を無料でダウンロード▷ www.shikenpass.com ◁で検索するだけNSE6_OTS_AR-7.6受験トレーリング
- NSE6_OTS_AR-7.6資格模擬 📰 NSE6_OTS_AR-7.6日本語版サンプル 🥉 NSE6_OTS_AR-7.6資格模擬 🏹 《 www.goshiken.com 》サイトにて最新▛ NSE6_OTS_AR-7.6 ▟問題集をダウンロードNSE6_OTS_AR-7.6資格勉強
- NSE6_OTS_AR-7.6資格模擬 🦱 NSE6_OTS_AR-7.6日本語版問題集 🍢 NSE6_OTS_AR-7.6ブロンズ教材 🟠 [ jp.fast2test.com ]サイトにて[ NSE6_OTS_AR-7.6 ]問題集を無料で使おうNSE6_OTS_AR-7.6日本語復習赤本
-
disqus.com, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes


 icons at the top
right corner of the subsection.