300-215無料問題, 300-215試験勉強過去問, 300-215 PDF, 300-215受験対策書, 300-215クラムメディア

2026年Jpexamの最新300-215 PDFダンプおよび300-215試験エンジンの無料共有:https://drive.google.com/open?id=1D6KVfhMucdJR6Gk5R-3DgsU4R81BmYyd
300-215試験シミュレーションは、競争力を向上させる優れたツールです。学習資料を使用した後、Cisco認定をより早く取得できます。この認定により、より多くの機会が与えられます。 300-215準備の質問の助けを借りて、あなたの周りの同僚と比較して、より効率的な仕事のパフォーマンスを得ることができます。 300-215学習教材には、次の機能があるため、非常に多くのメリットがあります。コーヒーを1杯使って300-215トレーニングエンジンについて学習していただければ幸いです。おそらくこれがあなたの変化の始まりです。
Cisco 300-215 Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| Fundamentals |
20% |
- Evidence collection in virtualized environments
- YARA rules for malware identification and classification
- Root cause analysis reporting components
- Antiforensic tactics, techniques, and procedures
- Encoding and obfuscation techniques
- Network infrastructure device forensics
|
| Forensics Techniques |
20% |
- Host-based evidence location and collection
- MITRE ATT&CK framework for fileless malware analysis
- Script analysis (Python, PowerShell, Bash) for log processing
- Identifying Indicators of Compromise (IOC) from tools output
- Forensic tools: Volatility, Sysinternals, SIFT, TCPdump
|
| Malware Analysis |
15% |
- Malware classification and behavior analysis
- Reverse engineering principles
- Static and dynamic malware analysis
- Malware family and campaign identification
|
| Incident Response Techniques |
30% |
- Attack vector analysis and mitigation recommendations
- Cisco security solutions for detection and prevention
- Correlating host and network activity data
- Response to zero-day exploits and vulnerabilities
- Threat intelligence interpretation: IOCs, IOAs, actor profiling
- Post-incident analysis and improvement actions
- Interpreting alerts from SIEM, IDS/IPS, syslog
|
| Forensics Processes |
15% |
- Data acquisition: memory, disk, network
- Legal and compliance considerations
- Antiforensic techniques: debugging, geolocation, obfuscation
- Evidence handling and chain of custody
|
>> 300-215無料問題 <<
Cisco 300-215試験勉強過去問 & 300-215 PDF
一つには、当社の最も先進的なオペレーションシステムであり、最速の配信速度を保証でき、お客様の個人情報は弊社のオペレーションシステムによって自動的に暗号化されます。また、300-215の実際の試験のオンラインアプリバージョンを使用すると、あらゆる種類の電子デバイスに関するトレーニング資料の質問を気軽に練習できます。さらに、300-215試験問題の助けを借りて、お客様の合格率は98%〜100%に達しました。近い将来、あなたの学習パートナーになることを楽しみにしています。
Cisco Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps 認定 300-215 試験問題 (Q106-Q111):
質問 # 106
A threat intelligence report identifies an outbreak of a new ransomware strain spreading via phishing emails that contain malicious URLs. A compromised cloud service provider, XYZCloud, is managing the SMTP servers that are sending the phishing emails. A security analyst reviews the potential phishing emails and identifies that the email is coming from XYZCloud. The user has not clicked the embedded malicious URL.
What is the next step that the security analyst should take to identify risk to the organization?
- A. Reset the reporting user's account and enable multifactor authentication.
- B. Find any other emails coming from the IP address ranges that are managed by XYZCloud.
- C. Create a detailed incident report and share it with top management.
- D. Delete email from user mailboxes and update the incident ticket with lessons learned.
正解:B
解説:
Since the phishing email originates from a known compromised cloud provider (XYZCloud), the correct immediate action for the security analyst is to determine the broader scope of exposure. This involves checking whether other users in the organization received similar emails from the same potentially malicious source. Therefore, querying for emails from theIP address rangesorSMTP domainslinked to XYZCloud is essential for identifying other possible attack vectors.
This step aligns with the containment phase of the incident response lifecycle, as outlined in theCyberOps Technologies (CBRFIR) 300-215 study guide, where threat hunting and log analysis are used to determine the extent of compromise and prevent lateral movement or further exposure. Only after the scope is understood should remediation or reporting actions follow.
Reference:CyberOps Technologies (CBRFIR) 300-215 study guide, Chapter: Email-Based Threats and Containment Strategy during Incident Response.
質問 # 107
Refer to the exhibit.
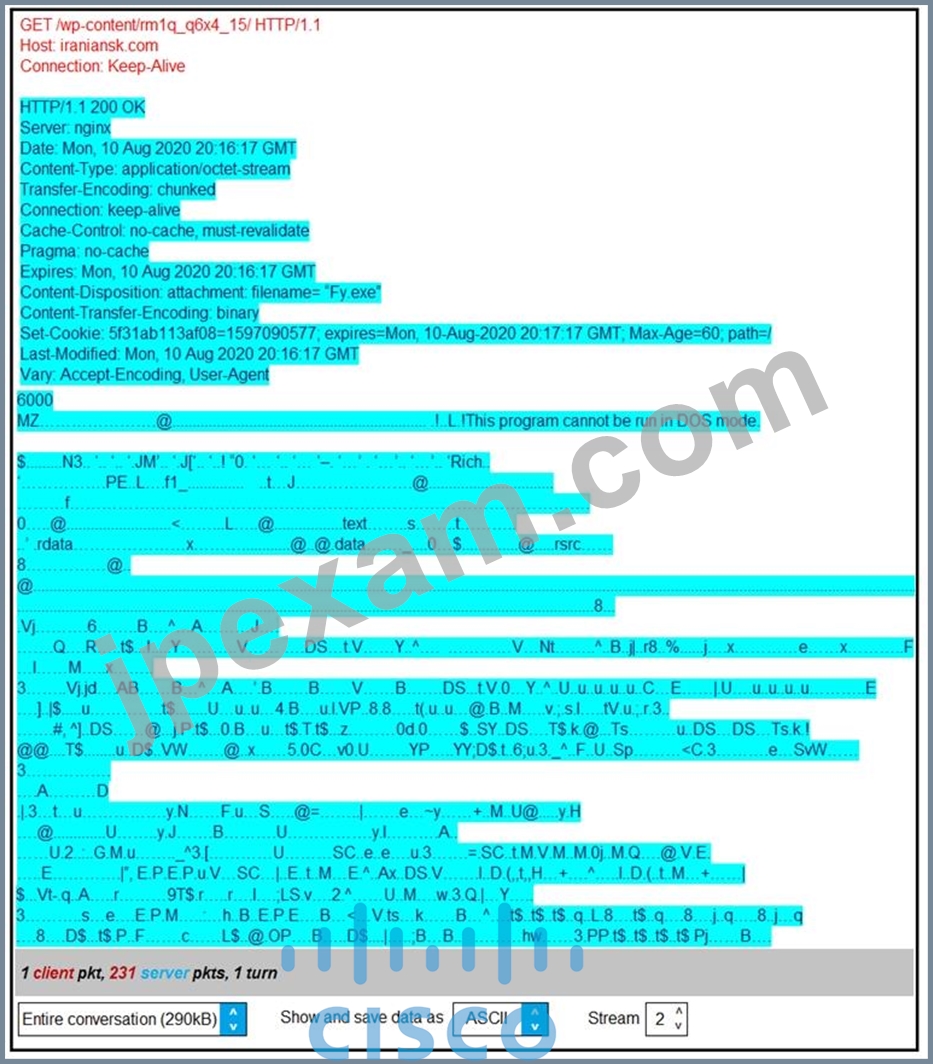
According to the Wireshark output, what are two indicators of compromise for detecting an Emotet malware download? (Choose two.)
- A. Hash value: 5f31ab113af08=1597090577
- B. filename= "Fy.exe"
- C. Domain name: iraniansk.com
- D. Server: nginx
- E. Content-Type: application/octet-stream
正解:B、C
解説:
From the Wireshark capture:
* A (iraniansk.com): This domain isnot a known legitimate resourceand is hosting a suspicious file named "Fy.exe," strongly indicative of amalware distribution domain.
* D (Fy.exe): TheContent-Disposition: attachment; filename="Fy.exe"header explicitly signals abinary executabledownload, a key indicator in Emotet campaigns.
WhileContent-Type: application/octet-stream(E) is typical of binary data transfers, it isnot uniqueto malware and cannot by itself serve as a strong IoC. Thenginx server (B)andcookie/hash string (C)similarly do not uniquely indicate compromise.
質問 # 108
Refer to the exhibit.
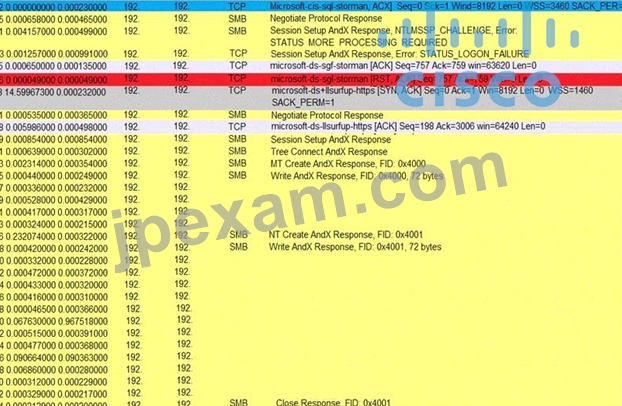
An engineer is analyzing a TCP stream in Wireshark after a suspicious email with a URL. What should be determined about the SMB traffic from this stream?
- A. It is redirecting to a malicious phishing website
- B. It is sharing access to files and printers.
- C. It is requesting authentication on the user site.
- D. It is exploiting redirect vulnerability
正解:B
解説:
The Wireshark output shows SMB protocol transactions, including NT Create AndX Response and Write AndX Response, indicating the transfer of files or objects. SMB (Server Message Block) is a protocol used for file sharing and printer access in Windows networks. The log does not indicate phishing or redirection behavior but rather normal SMB communication such as accessing files or shared resources.
-
質問 # 109
Refer to the exhibit.
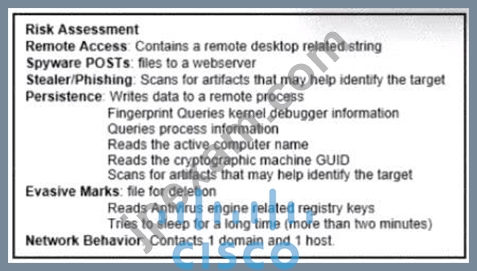
The application x-dosexec with hash
691c65e4fb1d19f82465df1d34ad51aaeceba14a78167262dc7b2840a6a6aa87 is reported as malicious and labeled as " Trojan.Generic " by the threat intelligence tool. What is considered an indicator of compromise?
- A. data compression
- B. process injection
- C. hooking
- D. modified registry
正解:B
解説:
Comprehensive and Detailed Explanation:
The exhibit lists several behaviors under categories such as Remote Access, Stealer/Phishing, Persistence, and Evasive Marks. Notably, under "Persistence" it states:
"Writes data to a remote process"
This behavior is indicative of "process injection," a technique where malware writes or injects malicious code into the address space of another process. This allows the malware to evade detection and run within the context of a legitimate process.
This matches the MITRE ATT & CK technique T1055 (Process Injection), which is also discussed in the Cisco CyberOps Associate guide under evasion and persistence tactics used by malware.
While modified registry and data compression are possible signs of malware, they are not explicitly referenced in the exhibit. The definitive indicator shown is related to process injection.
Therefore, the correct answer is: C. process injection.
質問 # 110
Refer to the exhibit.
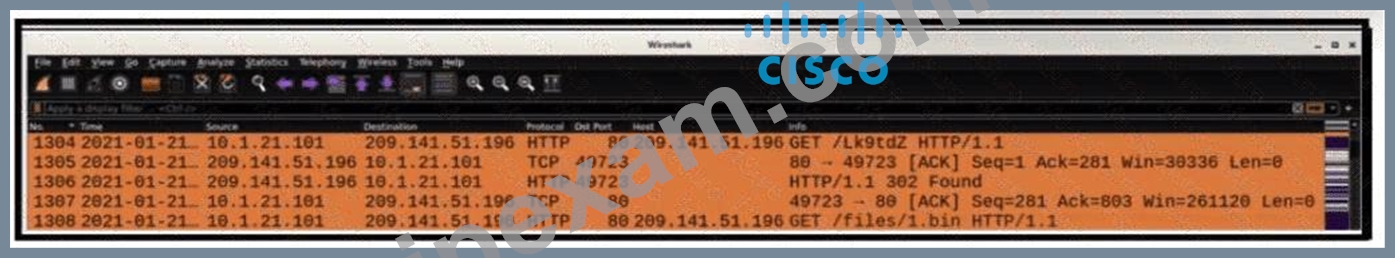
What is occurring within the exhibit?
- A. Host 209.141.51.196 redirects the client request from /Lk9tdZ to /files/1.bin.
- B. Host 209.141.51.196 redirects the client request to port 49723.
- C. Source 10.1.21.101 sends HTTP requests with the size of 302 kb.
- D. Source 10.1.21.101 is communicating with 209.141.51.196 over an encrypted channel.
正解:A
解説:
The Wireshark capture shows a series of HTTP requests and responses:
* The client (10.1.21.101) sends a GET request for /Lk9tdZ.
* The server (209.141.51.196) responds with HTTP/1.1 302 Found, which is a standard HTTP status code indicating a redirection.
* The subsequent GET request from the client is for /files/1.bin, which indicates it followed the redirect.
This behavior confirms that the server is issuing an HTTP 302 redirect from the initial request path /Lk9tdZ to
/files/1.bin. This is often observed in malware command-and-control behavior or file download staging.
* Option A is incorrect: 302 is a status code, not a data size.
* Option C is incorrect: port 49723 is a source/destination ephemeral port, not a redirect target.
* Option D is incorrect: communication is over HTTP, not HTTPS (which would indicate encryption).
Reference: CyberOps Technologies (CBRFIR) 300-215 study guide, Chapter on Network Traffic Analysis and HTTP Status Code Interpretation.
質問 # 111
......
時々重要な試験に合格するために大量の問題をする必要があります。我々の提供するソフトはこの要求をよく満たして専門的な解答の分析はあなたの理解にヘルプを提供できます。Ciscoの300-215試験の資料のいくつかのバーションのデモは我々のウェブサイトで無料でダウンロードできます。あなたの愛用する版をやってみよう。我々の共同の努力はあなたに順調にCiscoの300-215試験に合格させることができます。
300-215試験勉強過去問: https://www.jpexam.com/300-215_exam.html
- 100%合格率-一番優秀な300-215無料問題試験-試験の準備方法300-215試験勉強過去問 ❕ ⮆ www.xhs1991.com ⮄で⮆ 300-215 ⮄を検索して、無料で簡単にダウンロードできます300-215テスト内容
- 有効的な300-215無料問題一回合格-高品質な300-215試験勉強過去問 📉 ▛ 300-215 ▟を無料でダウンロード( www.goshiken.com )で検索するだけ300-215テスト内容
- 最高-検証する300-215無料問題試験-試験の準備方法300-215試験勉強過去問 ✴ ▶ www.goshiken.com ◀を開いて{ 300-215 }を検索し、試験資料を無料でダウンロードしてください300-215試験対策書
- 300-215問題と解答 👔 300-215全真模擬試験 🦙 300-215勉強方法 🎿 URL 「 www.goshiken.com 」をコピーして開き、☀ 300-215 ️☀️を検索して無料でダウンロードしてください300-215テスト内容
- 300-215合格受験記 ⭐ 300-215最新テスト 🚄 300-215テスト内容 🌸 ⏩ www.jpshiken.com ⏪サイトにて➤ 300-215 ⮘問題集を無料で使おう300-215科目対策
- 300-215全真模擬試験 🦑 300-215復習攻略問題 🏪 300-215参考資料 🛅 ➠ www.goshiken.com 🠰にて限定無料の“ 300-215 ”問題集をダウンロードせよ300-215科目対策
- 300-215 テストエンジ、300-215勉強資料、Conducting Forensic Analysis & Incident Response Using Cisco Technologies for CyberOps 練習問題 👌 「 www.goshiken.com 」の無料ダウンロード⇛ 300-215 ⇚ページが開きます300-215日本語pdf問題
- 300-215科目対策 🧊 300-215資格試験 ✌ 300-215試験合格攻略 ⛹ 検索するだけで「 www.goshiken.com 」から「 300-215 」を無料でダウンロード300-215参考資料
- 検証する-信頼的な300-215無料問題試験-試験の準備方法300-215試験勉強過去問 📭 サイト⏩ www.shikenpass.com ⏪で➠ 300-215 🠰問題集をダウンロード300-215試験合格攻略
- 300-215無料問題 - 無料ダウンロード 300-215試験勉強過去問 安全かつ簡単に購入することを約束します 😹 【 300-215 】の試験問題は{ www.goshiken.com }で無料配信中300-215復習時間
- 300-215ブロンズ教材 🌖 300-215テスト内容 🕡 300-215テスト内容 ◀ サイト✔ www.jpexam.com ️✔️で《 300-215 》問題集をダウンロード300-215日本語pdf問題
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, users.playground.ru, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, github.com, Disposable vapes
ちなみに、Jpexam 300-215の一部をクラウドストレージからダウンロードできます:https://drive.google.com/open?id=1D6KVfhMucdJR6Gk5R-3DgsU4R81BmYyd


 icons at the top
right corner of the subsection.