ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제, ISO-IEC-27001-Lead-Auditor시험덤프, ISO-IEC-27001-Lead-Auditor덤프자료, ISO-IEC-27001-Lead-Auditor최신버전 인기 덤프문제, ISO-IEC-27001-Lead-Auditor최신 시험덤프자료
참고: DumpTOP에서 Google Drive로 공유하는 무료 2026 PECB ISO-IEC-27001-Lead-Auditor 시험 문제집이 있습니다: https://drive.google.com/open?id=103LydTHWUEd1eRKCe6oJpa9i4AzM-O2O
DumpTOP PECB ISO-IEC-27001-Lead-Auditor덤프의 질문들과 답변들은 100%의 지식 요점과 적어도 98%의PECB ISO-IEC-27001-Lead-Auditor시험 문제들을 커버하는 수년동안 가장 최근의PECB ISO-IEC-27001-Lead-Auditor 시험 요점들을 컨설팅 해 온 시니어 프로 IT 전문가들의 그룹에 의해 구축 됩니다. PECB ISO-IEC-27001-Lead-Auditor 시험적중율 높은 덤프로 시험패스하세요.
PECB ISO-AIC-27001-LEAD-AUDITOR 시험은 ISO/IEC 27001 리드 감사원으로 인증되기를 원하는 개인을 위해 설계되었습니다. ISO/IEC 27001은 정보 보안 관리 시스템 (ISMS)을위한 프레임 워크를 제공하는 국제 표준입니다. 이 표준은 ISM을 설정, 구현, 유지 및 지속적으로 개선하기위한 요구 사항을 설명합니다. ISO/IEC 27001 리드 감사원으로 인증을 받으면 개인이 조직의 표준 준수를 감사하고 평가하는 데 능숙하다는 것을 보여줍니다.
PECB ISO-IEC-27001-Lead-Auditor 자격증 시험을 응시하려면 후보자들은 정보 보안 관리에서 최소 2년, 감사에서 1년의 전문 경력을 갖추어야 합니다. 또한 후보자들은 PECB 인증 ISO/IEC 27001 리드 구현자 교육 과정을 이수하거나 ISMS 구현에 대한 동등한 지식과 경험을 갖추어야 합니다.
>> ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제 <<
완벽한 ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제 시험덤프로 시험패스가능
DumpTOP는 여러분이 빠른 시일 내에PECB ISO-IEC-27001-Lead-Auditor인증시험을 효과적으로 터득할 수 있는 사이트입니다.PECB ISO-IEC-27001-Lead-Auditor덤프는 보장하는 덤프입니다. 만약 시험에서 떨어지셨다고 하면 우리는 무조건 덤프전액 환불을 약속 드립니다. 우리DumpTOP 사이트에서PECB ISO-IEC-27001-Lead-Auditor관련자료의 일부분 문제와 답 등 샘플을 제공함으로 여러분은 무료로 다운받아 체험해보실 수 있습니다. 체험 후 우리의DumpTOP에 신뢰감을 느끼게 됩니다. DumpTOP의PECB ISO-IEC-27001-Lead-Auditor덤프로 자신 있는 시험준비를 하세요.
PECB ISO-AIC-27001-Lead-Auditor Certification 시험은 정보 보안 분야의 전문가의 지식과 기술을 테스트하도록 설계되었습니다. 이 시험에는 위험 관리, 보안 관리 및 ISO/IEC 27001 표준 준수를 포함한 광범위한 주제가 다룹니다. 시험은 강렬하며 통과하려면 높은 수준의 숙련도가 필요합니다.
최신 ISO 27001 ISO-IEC-27001-Lead-Auditor 무료샘플문제 (Q246-Q251):
질문 # 246
During a third-party certification audit, you are presented with a list of issues by an auditee. Which four of the following constitute 'internal' issues in the context of a management system to ISO 27001:2022?
- A. Higher labour costs as a result of an aging population
- B. Increased absenteeism as a result of poor management
- C. A reduction in grants as a result of a change in government policy
- D. Poor levels of staff competence as a result of cuts in training expenditure
- E. Inability to source raw materials due to government sanctions
- F. A rise in interest rates in response to high inflation
- G. A fall in productivity linked to outdated production equipment
- H. Poor morale as a result of staff holidays being reduced
정답:B,D,G,H
설명:
Explanation
According to ISO 27001:2022 clause 4.1, the organisation shall determine external and internal issues that are relevant to its purpose and that affect its ability to achieve the intended outcome(s) of its information security management system (ISMS)12 External issues are factors outside the organisation that it cannot control, but can influence or adapt to. They include political, economic, social, technological, legal, and environmental factors that may affect the organisation's information security objectives, risks, and opportunities12 Internal issues are factors within the organisation that it can control or change. They include the organisation's structure, culture, values, policies, objectives, strategies, capabilities, resources, processes, activities, relationships, and performance that may affect the organisation's information security management system12 Therefore, the following issues are considered 'internal' in the context of a management system to ISO
27001:2022:
Poor levels of staff competence as a result of cuts in training expenditure: This is an internal issue because it relates to the organisation's capability, resource, and process of developing and maintaining the competence of its personnel involved in the ISMS. The organisation can control or change its training expenditure and its impact on staff competence12 Poor morale as a result of staff holidays being reduced: This is an internal issue because it relates to the organisation's culture, value, and relationship with its employees. The organisation can control or change its staff holiday policy and its impact on staff morale12 Increased absenteeism as a result of poor management: This is an internal issue because it relates to the organisation's performance, structure, and accountability of its management. The organisation can control or change its management practices and its impact on staff absenteeism12 A fall in productivity linked to outdated production equipment: This is an internal issue because it relates to the organisation's capability, resource, and process of ensuring the availability and suitability of its production equipment. The organisation can control or change its equipment maintenance and upgrade and its impact on productivity12 The following issues are considered 'external' in the context of a management system to ISO 27001:2022:
Higher labour costs as a result of an aging population: This is an external issue because it relates to the social and demographic factor that affects the availability and cost of labour in the market. The organisation cannot control or change the aging population, but can influence or adapt to its impact on labour costs12 A rise in interest rates in response to high inflation: This is an external issue because it relates to the economic and monetary factor that affects the cost and availability of capital in the market. The organisation cannot control or change the interest rates or inflation, but can influence or adapt to its impact on capital costs12 A reduction in grants as a result of a change in government policy: This is an external issue because it relates to the political and legal factor that affects the availability and conditions of public funding for the organisation. The organisation cannot control or change the government policy, but can influence or adapt to its impact on grants12 Inability to source raw materials due to government sanctions: This is an external issue because it relates to the political and legal factor that affects the availability and cost of raw materials in the market. The organisation cannot control or change the government sanctions, but can influence or adapt to its impact on raw materials12 References:
1: ISO/IEC 27001:2022 Lead Auditor (Information Security Management Systems) Course by CQI and IRCA Certified Training 1 2: ISO/IEC 27001 Lead Auditor Training Course by PECB 2
질문 # 247
You are performing an ISMS audit at a residential nursing home that provides healthcare services. The next step in your audit plan is to verify the information security of the business continuity management process.
During the audit, you learned that the organisation activated one of the business continuity plans (BCPs) to make sure the nursing service continued during the recent pandemic. You ask Service Manager to explain how the organisation manages information security during the business continuity management process.
The Service Manager presents the nursing service continuity plan for a pandemic and summarises the process as follows:
Stop the admission of any NEW residents.
70% of administration staff and 30% of medical staff will work from home.
Regular staff self-testing including submitting a negative test report 1 day BEFORE they come to the office.
Install ABC's healthcare mobile app, tracking their footprint and presenting a GREEN Health Status QR-Code for checking on the spot.
You ask the Service Manager how to prevent non-relevant family members or interested parties from accessing residents' personal data when staff work from home. The Service Manager cannot answer and suggests the n" Security Manager should help with that.
You would like to further investigate other areas to collect more audit evidence Select three options that will be in your audit trail.
- A. Collect more evidence on what resources the organisation provides to support the staff working from home. (Relevant to clause 7.1)
- B. Collect more evidence by interviewing more staff about their feeling about working from home.
(Relevant to clause 4.2)
- C. Collect more evidence on how the organisation performs a business risk assessment to evaluate how fast the existing residents can be discharged from the nursing home. (Relevant to clause 6)
- D. Collect more evidence on how the organisation manages information security on mobile devices and during teleworking (Relevant to control A.6.7)
- E. Collect more evidence on how the organisation makes sure only staff with a negative test result can enter the organisation (Relevant to control A.7.2)
- F. Collect more evidence on how and when the Business Continuity Wan has been tested. (Relevant to control A.5.29)
정답:D,E,F
설명:
Explanation
According to ISO/IEC 27001:2022, which specifies the requirements for establishing, implementing, maintaining and continually improving an information security management system (ISMS), control A.5.29 requires an organization to establish and maintain a business continuity management process to ensure the continued availability of information and information systems at the required level following disruptive incidents1. The organization should identify and prioritize critical information assets and processes, assess the risks and impacts of disruptive incidents, develop and implement business continuity plans (BCPs), test and review the BCPs, and ensure that relevant parties are aware of their roles and responsibilities1. Therefore, when verifying the information security of the business continuity management process, an ISMS auditor should verify that these aspects are met in accordance with the audit criteria.
Three options that will be in the audit trail for verifying control A.5.29 are:
* Collect more evidence on how the organisation manages information security on mobile devices and during teleworking (Relevant to control A.6.7): This option is relevant because it can provide evidence of how the organization has implemented appropriate controls to protect the confidentiality, integrity and availability of information and information systems when staff work from home using mobile devices, such as laptops, tablets or smartphones. This is related to control A.6.7, which requires an organization to establish a policy and procedures for teleworking and use of mobile devices1.
* Collect more evidence on how and when the Business Continuity Plan has been tested (Relevant to control A.5.29): This option is relevant because it can provide evidence of how the organization has tested and reviewed the BCPs to ensure their effectiveness and suitability for different scenarios, such as a pandemic. This is related to control A.5.29, which requires an organization to test and review the BCPs at planned intervals or when significant changes occur1.
* Collect more evidence on how the organisation makes sure only staff with a negative test result can enter the organisation (Relevant to control A.7.2): This option is relevant because it can provide evidence of how the organization has implemented appropriate controls to prevent or reduce the risk of infection or transmission of diseases among staff or residents, such as requiring regular staff self-testing and using a health status app. This is related to control A.7.2, which requires an organization to ensure that all employees and contractors are aware of information security threats and concerns, their responsibilities and liabilities, and are equipped to support organizational policies and procedures in this respect1.
The other options are not relevant to verifying control A.5.29, as they are not related to the control or its requirements. For example:
* Collect more evidence by interviewing more staff about their feeling about working from home (Relevant to clause 4.2): This option is not relevant because it does not provide evidence of how the organization has established and maintained a business continuity management process or ensured the continued availability of information and information systems following disruptive incidents. It may be related to clause 4.2, which requires an organization to understand the needs and expectations of interested parties, but not specifically to control A.5.29.
* Collect more evidence on what resources the organisation provides to support the staff working from
* home (Relevant to clause 7.1): This option is not relevant because it does not provide evidence of how the organization has established and maintained a business continuity management process or ensured the continued availability of information and information systems following disruptive incidents. It may be related to clause 7.1, which requires an organization to determine and provide the resources needed for its ISMS, but not specifically to control A.5.29.
* Collect more evidence on how the organisation performs a business risk assessment to evaluate how fast the existing residents can be discharged from the nursing home (Relevant to clause 6): This option is not relevant because it does not provide evidence of how the organization has established and maintained a business continuity management process or ensured the continued availability of information and information systems following disruptive incidents. It may be related to clause 6, which requires an organization to plan actions to address risks and opportunities for its ISMS, but not specifically to control A.5.29.
References: ISO/IEC 27001:2022 - Information technology - Security techniques - Information security management systems - Requirements
질문 # 248
In the context of a third-party certification audit, which two options state the management responsibilities of the audit team leader in managing the audit and the audit team?
- A. Auditing top management
- B. Adopting a risk-based approach to planning the audit
- C. Issuing the management system certificate
- D. Preparing the audit nonconformity reports
- E. Interviewing the ISMS manager
- F. Establishing contact with the auditee
정답:B,F
설명:
In the context of a third-party certification audit, the management responsibilities of the audit team leader in managing the audit and the audit team include adopting a risk-based approach to planning the audit and establishing contact with the auditee. A risk-based approach to planning the audit means that the team leader should consider the risks and opportunities that may affect the achievement of the audit objectives, the scope and criteria, the audit methods and techniques, the allocation of resources and the assignment of tasks to the audit team members. Establishing contact with the auditee means that the team leader should communicate with the auditee before, during and after the audit, to confirm the audit arrangements, to obtain relevant information, to address any issues or concerns, to provide feedback and to report the audit results and conclusions. Reference: = ISO 19011:2022, clauses 6.4.1 and 6.4.2; PECB Candidate Handbook ISO 27001 Lead Auditor, pages 24 and 25.
질문 # 249
Which of the following statements are correct for Clean Desk Policy?
- A. Don't leave highly confidential items.
- B. Don't leave valuable items on your desk if you are not in your work area.
- C. Don't leave laptops without cable lock.
- D. Don't leave confidential documents on your desk.
정답:A,B,D
질문 # 250
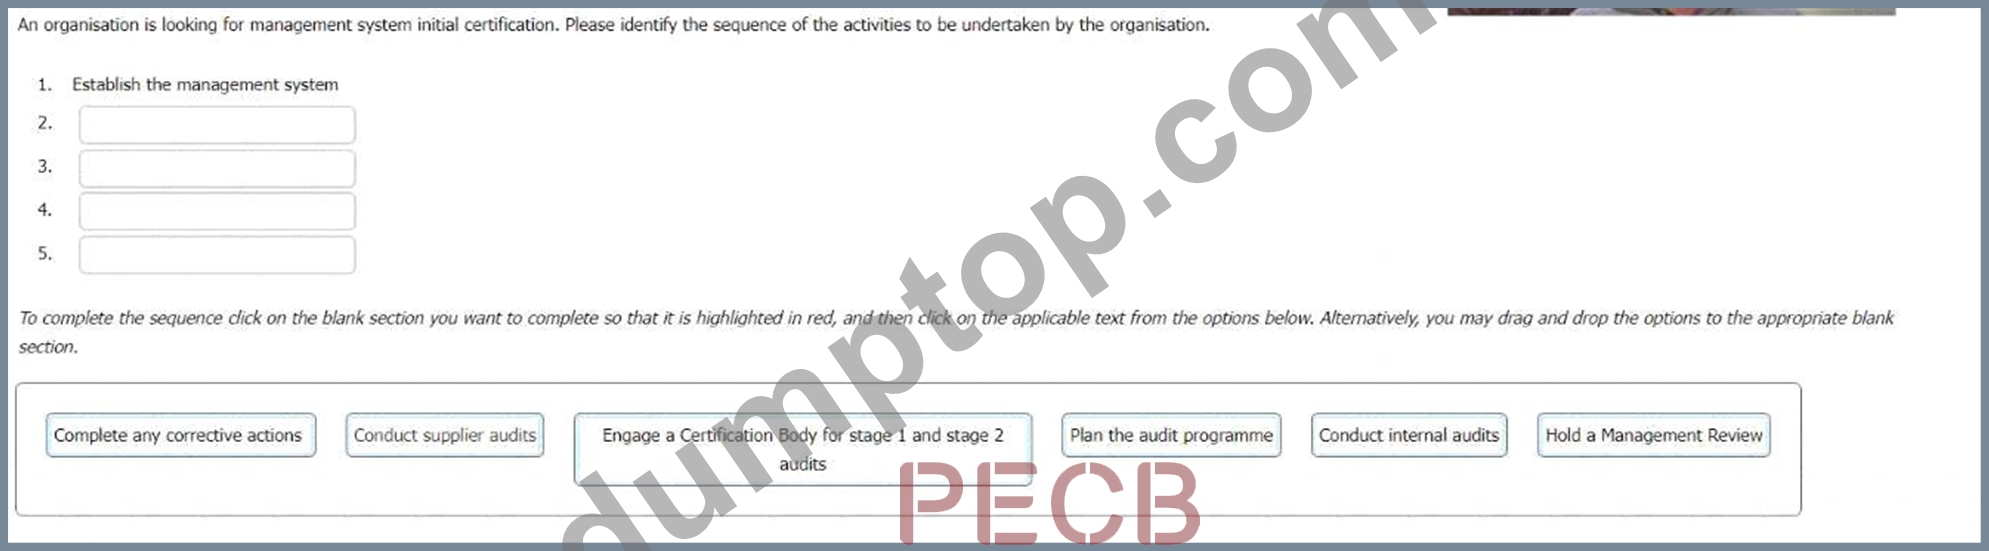
An organisation is looking for management system initial certification. Please identify the sequence of the activities to be undertaken by the organisation.
To complete the sequence click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the options to the appropriate blank section.
정답:
설명:
Explanation:
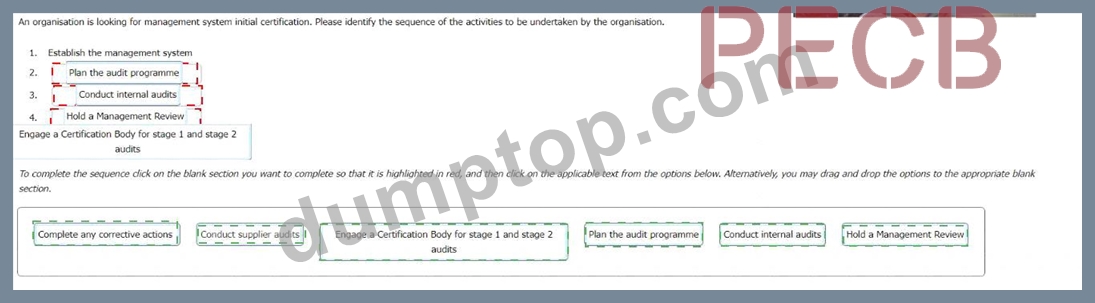
The correct sequence of activities is:
* Establish the management system
* Plan the audit programme
* Conduct internal audits
* Hold a Management Review
* Engage a Certification Body for stage 1 and stage 2 audits
* Complete any corrective actions
Comprehensive but Short Explanation: = According to the PECB Candidate Handbook - ISO/IEC 27001 Lead Auditor, the steps for achieving certification are as follows1:
* Establish the management system: This involves defining the scope, objectives, policies, procedures, and controls of the ISMS, as well as ensuring the availability of resources and top management commitment.
* Plan the audit programme: This involves defining the audit objectives, criteria, scope, frequency, methods, and responsibilities for conducting internal audits of the ISMS.
* Conduct internal audits: This involves verifying the conformity and effectiveness of the ISMS, as well as identifying any nonconformities or opportunities for improvement.
* Hold a Management Review: This involves reviewing the performance and suitability of the ISMS, as well as deciding on any changes or actions needed to improve it.
* Engage a Certification Body for stage 1 and stage 2 audits: This involves selecting a reputable and accredited certification body to conduct an external audit of the ISMS, consisting of two stages: a documentation review and an on-site assessment.
* Complete any corrective actions: This involves addressing any nonconformities or findings identified by the certification body, and providing evidence of their implementation and effectiveness.
References: = 1: PECB Candidate Handbook - ISO/IEC 27001 Lead Auditor, pages 25-26.
질문 # 251
......
ISO-IEC-27001-Lead-Auditor시험덤프: https://www.dumptop.com/PECB/ISO-IEC-27001-Lead-Auditor-dump.html
- ISO-IEC-27001-Lead-Auditor높은 통과율 시험대비 덤프공부 📅 ISO-IEC-27001-Lead-Auditor높은 통과율 공부문제 ❓ ISO-IEC-27001-Lead-Auditor퍼펙트 덤프데모 🧕 오픈 웹 사이트「 www.exampassdump.com 」검색《 ISO-IEC-27001-Lead-Auditor 》무료 다운로드ISO-IEC-27001-Lead-Auditor덤프문제모음
- ISO-IEC-27001-Lead-Auditor퍼펙트 덤프데모 🎾 ISO-IEC-27001-Lead-Auditor높은 통과율 시험대비 공부자료 ✨ ISO-IEC-27001-Lead-Auditor덤프문제모음 👼 시험 자료를 무료로 다운로드하려면➽ www.itdumpskr.com 🢪을 통해➥ ISO-IEC-27001-Lead-Auditor 🡄를 검색하십시오ISO-IEC-27001-Lead-Auditor시험대비 덤프공부자료
- ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제 100%시험패스 인증덤프공부 🎎 「 www.pass4test.net 」에서 검색만 하면{ ISO-IEC-27001-Lead-Auditor }를 무료로 다운로드할 수 있습니다ISO-IEC-27001-Lead-Auditor높은 통과율 공부문제
- 최신 ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제 인증덤프공부자료 🤼 무료로 다운로드하려면➥ www.itdumpskr.com 🡄로 이동하여[ ISO-IEC-27001-Lead-Auditor ]를 검색하십시오ISO-IEC-27001-Lead-Auditor시험문제모음
- 최신 ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제 인증덤프공부자료 💳 【 www.passtip.net 】웹사이트를 열고“ ISO-IEC-27001-Lead-Auditor ”를 검색하여 무료 다운로드ISO-IEC-27001-Lead-Auditor시험문제모음
- ISO-IEC-27001-Lead-Auditor높은 통과율 덤프자료 🏳 ISO-IEC-27001-Lead-Auditor퍼펙트 덤프 최신 샘플 🕔 ISO-IEC-27001-Lead-Auditor시험문제모음 🚪 지금【 www.itdumpskr.com 】에서▷ ISO-IEC-27001-Lead-Auditor ◁를 검색하고 무료로 다운로드하세요ISO-IEC-27001-Lead-Auditor시험대비 덤프공부자료
- ISO-IEC-27001-Lead-Auditor높은 통과율 시험대비 공부자료 👐 ISO-IEC-27001-Lead-Auditor덤프공부 🕉 ISO-IEC-27001-Lead-Auditor높은 통과율 공부문제 🔢 시험 자료를 무료로 다운로드하려면➥ www.pass4test.net 🡄을 통해➥ ISO-IEC-27001-Lead-Auditor 🡄를 검색하십시오ISO-IEC-27001-Lead-Auditor퍼펙트 덤프 최신 샘플
- ISO-IEC-27001-Lead-Auditor 덤프공부, ISO-IEC-27001-Lead-Auditor시험자료 📏 ➤ www.itdumpskr.com ⮘에서 검색만 하면➽ ISO-IEC-27001-Lead-Auditor 🢪를 무료로 다운로드할 수 있습니다ISO-IEC-27001-Lead-Auditor인기자격증 덤프자료
- ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제 인증시험패스하여 자격증 취득하기 🛶 ☀ www.itdumpskr.com ️☀️에서 검색만 하면▶ ISO-IEC-27001-Lead-Auditor ◀를 무료로 다운로드할 수 있습니다ISO-IEC-27001-Lead-Auditor최신버전 덤프샘플문제
- 시험패스에 유효한 ISO-IEC-27001-Lead-Auditor합격보장 가능 덤프문제 최신버전 덤프데모문제 다운받기 🌕 【 www.itdumpskr.com 】은➽ ISO-IEC-27001-Lead-Auditor 🢪무료 다운로드를 받을 수 있는 최고의 사이트입니다ISO-IEC-27001-Lead-Auditor최신버전 인기 덤프문제
- ISO-IEC-27001-Lead-Auditor 덤프공부, ISO-IEC-27001-Lead-Auditor시험자료 🌅 무료로 쉽게 다운로드하려면▛ www.koreadumps.com ▟에서“ ISO-IEC-27001-Lead-Auditor ”를 검색하세요ISO-IEC-27001-Lead-Auditor높은 통과율 덤프자료
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, learn.csisafety.com.au, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes
참고: DumpTOP에서 Google Drive로 공유하는 무료, 최신 ISO-IEC-27001-Lead-Auditor 시험 문제집이 있습니다: https://drive.google.com/open?id=103LydTHWUEd1eRKCe6oJpa9i4AzM-O2O


 icons at the top
right corner of the subsection.