SC-500勉強時間 & SC-500試験勉強書

Drag to rearrange sections
HTML/Embedded Content

SC-500勉強時間, SC-500試験勉強書, SC-500トレーニング費用, SC-500受験方法, SC-500受験対策書

SC-500認定試験はたいへん難しい試験ですね。しかし、難しい試験といっても、試験を申し込んで受験する人が多くいます。なぜかと言うと、もちろんSC-500認定試験がとても大切な試験ですから。IT職員の皆さんにとって、この試験のSC-500認証資格を持っていないならちょっと大変ですね。この認証資格はあなたの仕事にたくさんのメリットを与えられ、あなたの昇進にも助けになることができます。とにかく、これは皆さんのキャリアに大きな影響をもたらせる試験です。こんなに重要な試験ですから、あなたも受験したいでしょう。

Microsoft SC-500 Exam Syllabus Topics:

Section Weight Objectives
Topic 1: Manage and monitor security posture 20–25% - Microsoft Defender for Cloud
  • 1. Multi-cloud (AWS/GCP) integration
    • 2. External Attack Surface Management (EASM)
      • 3. Compliance frameworks evaluation
        • 4. Defender CSPM risk identification
          • 5. Defender Vulnerability Management
            • 6. Workload protection plans
              - Microsoft Sentinel
              • 1. Data collection rules and WEF
                • 2. Automation rules and playbooks
                  • 3. Custom logs and tables
                    • 4. Data connectors (Azure, syslog, CEF)
                      • 5. Workspaces and role assignment
                        • 6. Retention policies
                          - Security Copilot
                          • 1. Security Store agents
                            • 2. Permissions and roles
                              • 3. Plugins and integrations
                                • 4. Workspace configuration
                                  Topic 2: Manage identity, access, and governance 20–25% - Secure access to resources by using Microsoft Entra ID
                                  • 1. Privileged Identity Management (PIM)
                                    • 2. Conditional Access policies
                                      • 3. Managed identities for Azure resources
                                        • 4. OAuth consent and permission grants
                                          • 5. Authentication methods (MFA, passwordless)
                                            • 6. Enterprise applications and app registrations
                                              - Governance and compliance enforcement
                                              • 1. Resource locks
                                                • 2. Infrastructure as Code security controls
                                                  • 3. Microsoft Defender for Cloud compliance
                                                    • 4. Azure Policy (built-in and custom)
                                                      • 5. Azure Backup security controls
                                                        • 6. RBAC and role management (Azure & Entra roles)
                                                          - Secure secrets and keys using Azure Key Vault
                                                          • 1. Defender for Key Vault and CSPM scanning
                                                            • 2. Keys, secrets, and certificates management
                                                              • 3. Key Vault deployment and configuration
                                                                • 4. Access policies and firewall settings
                                                                  Topic 3: Secure compute 20–25% - Servers and virtual machines
                                                                  • 1. Azure Bastion
                                                                    • 2. Just-in-time (JIT) VM access
                                                                      • 3. Disk encryption
                                                                        • 4. Azure Arc hybrid security
                                                                          • 5. Agentless scanning and EDR
                                                                            • 6. Defender for Servers onboarding
                                                                              • 7. Secure boot and vTPM
                                                                                - Application platform security
                                                                                • 1. Web Application Firewall (WAF)
                                                                                  • 2. AKS security and Defender for Containers
                                                                                    • 3. App Service security controls
                                                                                      • 4. Azure Functions security
                                                                                        • 5. Container Registry security
                                                                                          • 6. API Management security policies
                                                                                            - Security for AI workloads
                                                                                            • 1. Microsoft Purview DSPM for AI
                                                                                              • 2. Security Copilot agents and monitoring
                                                                                                • 3. Defender for AI services
                                                                                                  • 4. Microsoft Copilot and AI risk identification
                                                                                                    • 5. Entra Agent ID security and access control
                                                                                                      • 6. AI Gateway (Azure API Management)
                                                                                                        Topic 4: Secure storage, databases, and networking 25–30% - Database security
                                                                                                        • 1. Azure SQL security configuration
                                                                                                          • 2. Database auditing
                                                                                                            • 3. Defender for Databases
                                                                                                              - Network security
                                                                                                              • 1. Azure Firewall
                                                                                                                • 2. Azure Virtual Network Manager
                                                                                                                  • 3. Private endpoints and Private Link
                                                                                                                    • 4. Virtual WAN security
                                                                                                                      • 5. NSGs and ASGs
                                                                                                                        • 6. Network Watcher diagnostics
                                                                                                                          • 7. VPN security
                                                                                                                            - Storage security
                                                                                                                            • 1. Access policies for storage
                                                                                                                              • 2. Defender for Storage
                                                                                                                                • 3. Storage firewall rules
                                                                                                                                  • 4. Storage account security configuration

                                                                                                                                    >> SC-500勉強時間 <<

                                                                                                                                    SC-500試験勉強書、SC-500トレーニング費用

                                                                                                                                    すべての顧客の誠実な要件を考慮して、SC-500テストの質問は、高品質の製品と思いやりのあるアフターサービスを備えた候補者に約束します。試験での99%の合格率、購入前の無料トライアル、安全なプライバシー保護など、SC-500トレーニング資料の多くの利点がよく認識されています。顧客の観点から、最適なSC-500模擬試験へのすべての顧客の信頼とフィードバックを大切にし、最良の選択です。

                                                                                                                                    Microsoft Implementing End-to-End Security Controls for Cloud and AI Workloads 認定 SC-500 試験問題 (Q95-Q100):

                                                                                                                                    質問 # 95
                                                                                                                                    You have an Azure subscription that contains a user named User1 and an Azure Container Registry named ContReg1.
                                                                                                                                    You enable content trust for ContReg1.
                                                                                                                                    You need to ensure that User1 can create trusted images in ContReg1 The solution must use the principle of least privilege.
                                                                                                                                    Which two roles should you assign to User1? Each correct answer presents part of the solution.
                                                                                                                                    NOTE: Each correct selection is worth one point.

                                                                                                                                    • A. AcrImageSigner
                                                                                                                                    • B. AcrQuarantineWriter
                                                                                                                                    • C. Contributor
                                                                                                                                    • D. AcrPush
                                                                                                                                    • E. AcrQuarantineReader

                                                                                                                                    正解:A、D

                                                                                                                                    解説:
                                                                                                                                    To create trusted images, the user must be able to push images and sign them. AcrPush allows pushing image content to the registry, while AcrImageSigner allows signing trusted images. Contributor would be excessive because it grants broad management rights. Quarantine reader/writer roles relate to quarantine workflows, not content trust signing. The combination of AcrPush and AcrImageSigner matches least privilege for trusted image creation. This answer also follows operational scalability. Microsoft security architecture favors policy- driven deployment, agentless assessment, managed identities, and Defender workload plans where possible.
                                                                                                                                    Those mechanisms reduce manual configuration while keeping enforcement tied to the resource type, which is why the selected choice is stronger than manual or after-the-fact alternatives. The result is a direct exam- style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source/topic: SC-500 Study Guide > Azure Container Registry security; Microsoft Learn > ACR roles for push and image signing.


                                                                                                                                    質問 # 96
                                                                                                                                    You have a Microsoft Entra tenant that has the following configurations:
                                                                                                                                    *User consent for applications is disabled.
                                                                                                                                    *Only administrators can grant permissions to applications.
                                                                                                                                    You register an application named App1 that uses delegated Microsoft Graph permissions.
                                                                                                                                    You need to configure App1 to meet the following requirements:
                                                                                                                                    *Enable user sign-ins without interactive consent prompts.
                                                                                                                                    *Enable App1 to access Microsoft Graph on behalf of the signed-in user.
                                                                                                                                    What should you do?

                                                                                                                                    • A. Grant admin consent to App1 for the required delegated permissions.
                                                                                                                                    • B. Configure enterprise applications to require user assignment and assign users to App1.
                                                                                                                                    • C. Add the required delegated Microsoft Graph permissions to the app registration and rely on user consent during sign-in.
                                                                                                                                    • D. Modify the app registration to use application permissions instead of delegated permissions.

                                                                                                                                    正解:A

                                                                                                                                    解説:
                                                                                                                                    Delegated Microsoft Graph permissions allow an application to act on behalf of the signed-in user. Because user consent is disabled and only administrators may grant permissions, users cannot complete the consent prompt themselves. Granting admin consent for the required delegated permissions pre-authorizes the app and removes the interactive consent prompt while still preserving the delegated model. Switching to application permissions would change the operating model and grant app-only access. For SC-500, the decisive distinction is whether the control authenticates an identity, grants authorization, or merely changes configuration visibility. The incorrect choices generally either grant excessive privilege, change the application model, or operate at the wrong scope. Microsoft expects the least-privilege identity path that satisfies the scenario without introducing shared secrets or unnecessary tenant-wide rights. The result is a direct exam-style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source/topic: SC-500 Study Guide > OAuth permission grants and consent; Microsoft Learn > admin consent for delegated permissions.


                                                                                                                                    質問 # 97
                                                                                                                                    Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals.
                                                                                                                                    More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
                                                                                                                                    After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
                                                                                                                                    You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
                                                                                                                                    You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
                                                                                                                                    You need to ensure that VM1 and VM2 can access storage1.
                                                                                                                                    Solution: You create a user-assigned managed identity, assign the identity to each virtual machine, and then add each managed identity to a role on storage1.
                                                                                                                                    Does this meet the goal?

                                                                                                                                    • A. Yes
                                                                                                                                    • B. No

                                                                                                                                    正解:A

                                                                                                                                    解説:
                                                                                                                                    A user-assigned managed identity can be attached to multiple virtual machines and then granted an Azure Storage data role. The applications running on VM1 and VM2 can request tokens for that identity and access storage1 without account keys. Public network access is already enabled, so the missing control is authorization. Assigning the user-assigned managed identity to the correct storage role satisfies the access requirement. For SC-500, the decisive distinction is whether the control authenticates an identity, grants authorization, or merely changes configuration visibility. The incorrect choices generally either grant excessive privilege, change the application model, or operate at the wrong scope. Microsoft expects the least- privilege identity path that satisfies the scenario without introducing shared secrets or unnecessary tenant- wide rights. The result is a direct exam-style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source
                                                                                                                                    /topic: SC-500 Study Guide > managed identities; Microsoft Learn > user-assigned managed identities and role assignment to storage.


                                                                                                                                    質問 # 98
                                                                                                                                    You have a Microsoft 365 subscription.
                                                                                                                                    You use Microsoft Entra Agent ID to manage an agent identity.
                                                                                                                                    You manage AI agents from the Microsoft 365 admin center.
                                                                                                                                    An autonomous agent named Agent1 runs without a signed-in user. The agent must access Microsoft Graph and read secrets from a single Azure key vault.
                                                                                                                                    You need to grant Agent 1 access to Microsoft Graph and Key Vault without requiring user interaction or consent at runtime.
                                                                                                                                    What should you do for the agent identity? To answer, drag the appropriate actions to the correct services.
                                                                                                                                    Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
                                                                                                                                    NOTE: Each correct selection is worth one point.
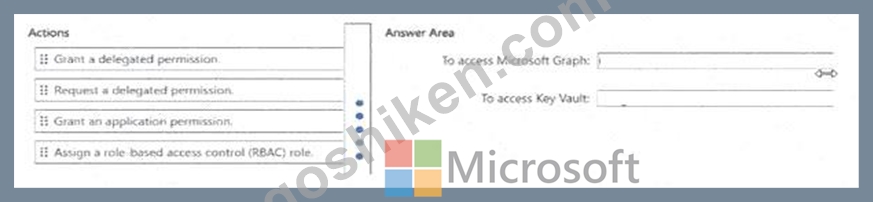
                                                                                                                                    正解:

                                                                                                                                    解説:
                                                                                                                                    Explanation:
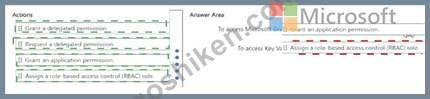
                                                                                                                                    To access Microsoft Graph: Grant an application permission; To access Key Vault: Assign a role-based access control (RBAC) role
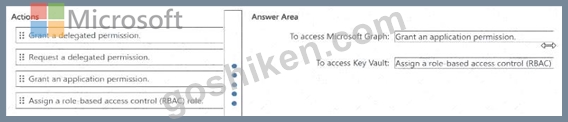
                                                                                                                                    An autonomous agent has no signed-in user at runtime, so Microsoft Graph access must use application permissions rather than delegated permissions. Key Vault is protected through Azure RBAC, so the agent identity should receive an appropriate Key Vault role at the smallest possible scope. This avoids runtime user consent and avoids embedding secrets. Delegated permissions would fail for a background agent because there is no user context. For SC-500, the decisive distinction is whether the control authenticates an identity, grants authorization, or merely changes configuration visibility. The incorrect choices generally either grant excessive privilege, change the application model, or operate at the wrong scope. Microsoft expects the least- privilege identity path that satisfies the scenario without introducing shared secrets or unnecessary tenant- wide rights. The result is a direct exam-style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source
                                                                                                                                    /topic: SC-500 Study Guide > Manage Entra Agent ID access; Microsoft Learn > Graph application permissions and Key Vault RBAC.


                                                                                                                                    質問 # 99
                                                                                                                                    You have a Microsoft Sentinel-enabled Log Analytics workspace named Workspace1.
                                                                                                                                    Your company receives JSON security events from a software as a service (SaaS) application.
                                                                                                                                    You plan to create a custom Microsoft Sentinel data connector.
                                                                                                                                    You need to prepare Workspace1 for the incoming JSON data.
                                                                                                                                    What should you do first?

                                                                                                                                    • A. Create a custom log table in Workspace1.
                                                                                                                                    • B. Create an analytics rule in Microsoft Sentinel.
                                                                                                                                    • C. Configure a diagnostic setting for the SaaS application.
                                                                                                                                    • D. Install a built-in Microsoft Sentinel data connector.

                                                                                                                                    正解:A

                                                                                                                                    解説:
                                                                                                                                    To prepare Workspace1 for incoming JSON security events from your SaaS application, your first step is to create a custom table in the Log Analytics workspace to define how the data will be stored.
                                                                                                                                    Reference:
                                                                                                                                    https://learn.microsoft.com/en-us/azure/sentinel/data-transformation


                                                                                                                                    質問 # 100
                                                                                                                                    ......

                                                                                                                                    SC-500認定試験は試験に関連する書物を学ぶだけで合格できるものではないです。がむしゃらに試験に要求された関連知識を積み込むより、価値がある問題を勉強したほうがいいです。効率のあがる試験問題集は受験生の皆さんにとって欠くことができないツールです。ですから、はやくGoShikenのSC-500問題集を入手しましょう。これは高い的中率を持っている問題集で、ほかのどのような勉強法よりもずっと効果があるのです。これはあなたが一回で楽に成功できるを保証するめぼしい参考書です。

                                                                                                                                    SC-500試験勉強書: https://www.goshiken.com/Microsoft/SC-500-mondaishu.html

                                                                                                                                    html    
                                                                                                                                    Drag to rearrange sections
                                                                                                                                    Rich Text Content
                                                                                                                                    rich_text    

                                                                                                                                    Page Comments