FCP_FGT_AD-7.6受験対策書, FCP_FGT_AD-7.6テスト内容, FCP_FGT_AD-7.6日本語参考, FCP_FGT_AD-7.6対応資料, FCP_FGT_AD-7.6専門知識内容

ちなみに、GoShiken FCP_FGT_AD-7.6の一部をクラウドストレージからダウンロードできます:https://drive.google.com/open?id=1V5yIVwuihVJUNRwHc-DKdyeLH4hSPz8g
話と行動の距離はどのぐらいありますか。これは人の心によることです。意志が強い人にとって、行動は目と鼻の先にあるのです。あなたはきっとこのような人でしょう。FortinetのFCP_FGT_AD-7.6認定試験に申し込んだ以上、試験に合格しなければならないです。これもあなたの意志が強いことを表示する方法です。GoShikenが提供したトレーニング資料はインターネットで最高のものです。FortinetのFCP_FGT_AD-7.6認定試験に合格したいのなら、GoShikenのFortinetのFCP_FGT_AD-7.6試験トレーニング資料を利用してください。
Fortinet FCP_FGT_AD-7.6 Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| Deployment and System Configuration |
20% |
- Resource and connectivity troubleshooting
- Fortinet Security Fabric implementation
- Initial configuration
- FGCP HA cluster configuration
|
| Firewall Policies and Authentication |
25% |
- FSSO deployment and configuration
- Firewall policy configuration
- SNAT and DNAT configuration
- Authentication methods
|
| Content Inspection |
20% |
- Application control
- Antivirus scanning
- Inspection modes and web filtering
- Intrusion Prevention System (IPS)
- Encrypted traffic inspection
|
| Routing |
15% |
- SD-WAN deployment and load balancing
- Static routing configuration
|
| VPN |
20% |
- IPsec VPN deployment
- SSL VPN configuration and implementation
|
>> FCP_FGT_AD-7.6受験対策書 <<
FCP_FGT_AD-7.6試験の準備方法 | 効果的なFCP_FGT_AD-7.6受験対策書試験 | 実際的なFCP - FortiGate 7.6 Administratorテスト内容
急速に発展している世界のすべての人にとって、良い仕事をすることがますます重要になっていることは私たちに知られています。 FCP_FGT_AD-7.6認定を取得することがますます困難になっていることがわかっています。仕事、賃金、およびFCP_FGT_AD-7.6認定が心配な場合、これを変更する場合は、FCP_FGT_AD-7.6試験トレントで高品質の問題を解決するのを手伝います。無料でダウンロードできます。 FCP_FGT_AD-7.6ガイドトレントのウェブ上のデモ。 FCP_FGT_AD-7.6試験の質問に後悔しないことをお約束します。
Fortinet FCP - FortiGate 7.6 Administrator 認定 FCP_FGT_AD-7.6 試験問題 (Q71-Q76):
質問 # 71
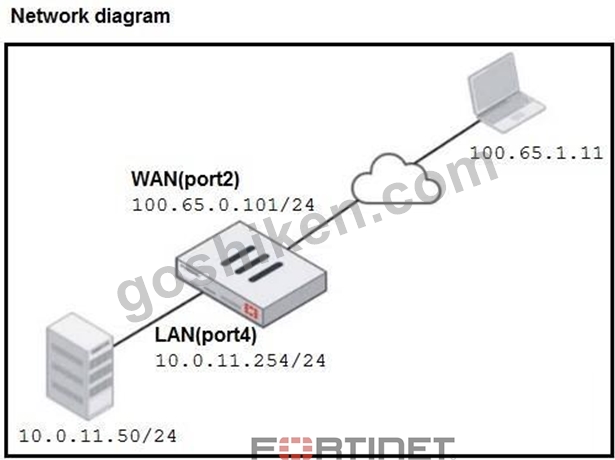
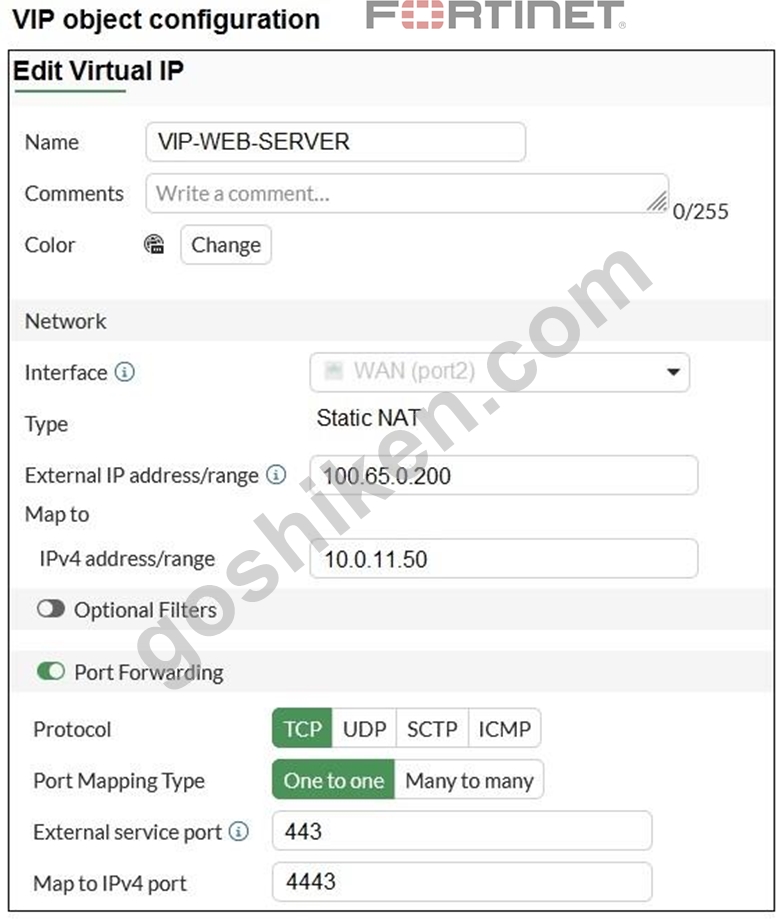
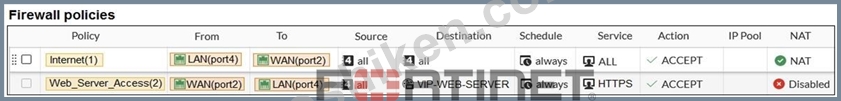
Refer to the exhibits. A diagram of a FortiGate device connected to the network VIP object and firewall policy configurations are shown.
The WAN (port2) interface has the IP address 100.65.0.101/24.
The LAN (port4) interface has the IP address 10.0.11.254/24.
If the host 100.65.1.111sends a TCP SYN packet on port 443 to 100.65.0.200, what will the source address, destination address, and destination port of the packet be at the time FortiGate forwards the packet to the destination?
- A. 10.0.11.254, 100.65.0.200, and 443, respectively
- B. 100.65.1.111, 10.0.11.50, and 4443, respectively
- C. 10.0.11.254, 10.0.15.50, and 4443, respectively
- D. 100.65.1.111, 10.0.11.50and 443, respectively
正解:B
解説:
The VIP object maps the external IP 100.65.0.200:443 to the internal server 10.0.11.50:4443.
Since NAT is disabled on the firewall policy, the source IP is preserved.
So, when host 100.65.1.111 connects to 100.65.0.200:443:
- The source remains 100.65.1.111.
- The destination IP is translated to 10.0.11.50.
- The destination port is translated to 4443.
質問 # 72
An administrator needs to analyze and resolve port conflicts between SSL VPN and HTTPS administrative access on the same interface.
In which two ways can this be done? (Choose two.)
- A. Keep port 443 for both SSL VPN and HTTPS administrative access on the same interface without any problems.
- B. Run SSL VPN on one interface using port 443 and enable HTTPS administrative access on a different interface, also using port 443.
- C. Change the port number for either the SSL VPN service or the HTTPS administrative service if both are on the same interface.
- D. Disable SSL VPN if HTTPS administrative access is using port 443 on any interface.
正解:B、C
解説:
You can keep port 443 for SSL VPN on one interface and also use port 443 for HTTPS admin access on a different interface. Since the services are bound to different interfaces, no conflict occurs.
If both SSL VPN and HTTPS admin access are required on the same interface, you must change the port number for one of the services to avoid a port conflict.
質問 # 73
Refer to the exhibit. A network administrator is troubleshooting an IPsec tunnel between two FortiGate devices. The administrator has determined that phase 1 status is up, but phase 2 fails to come up.
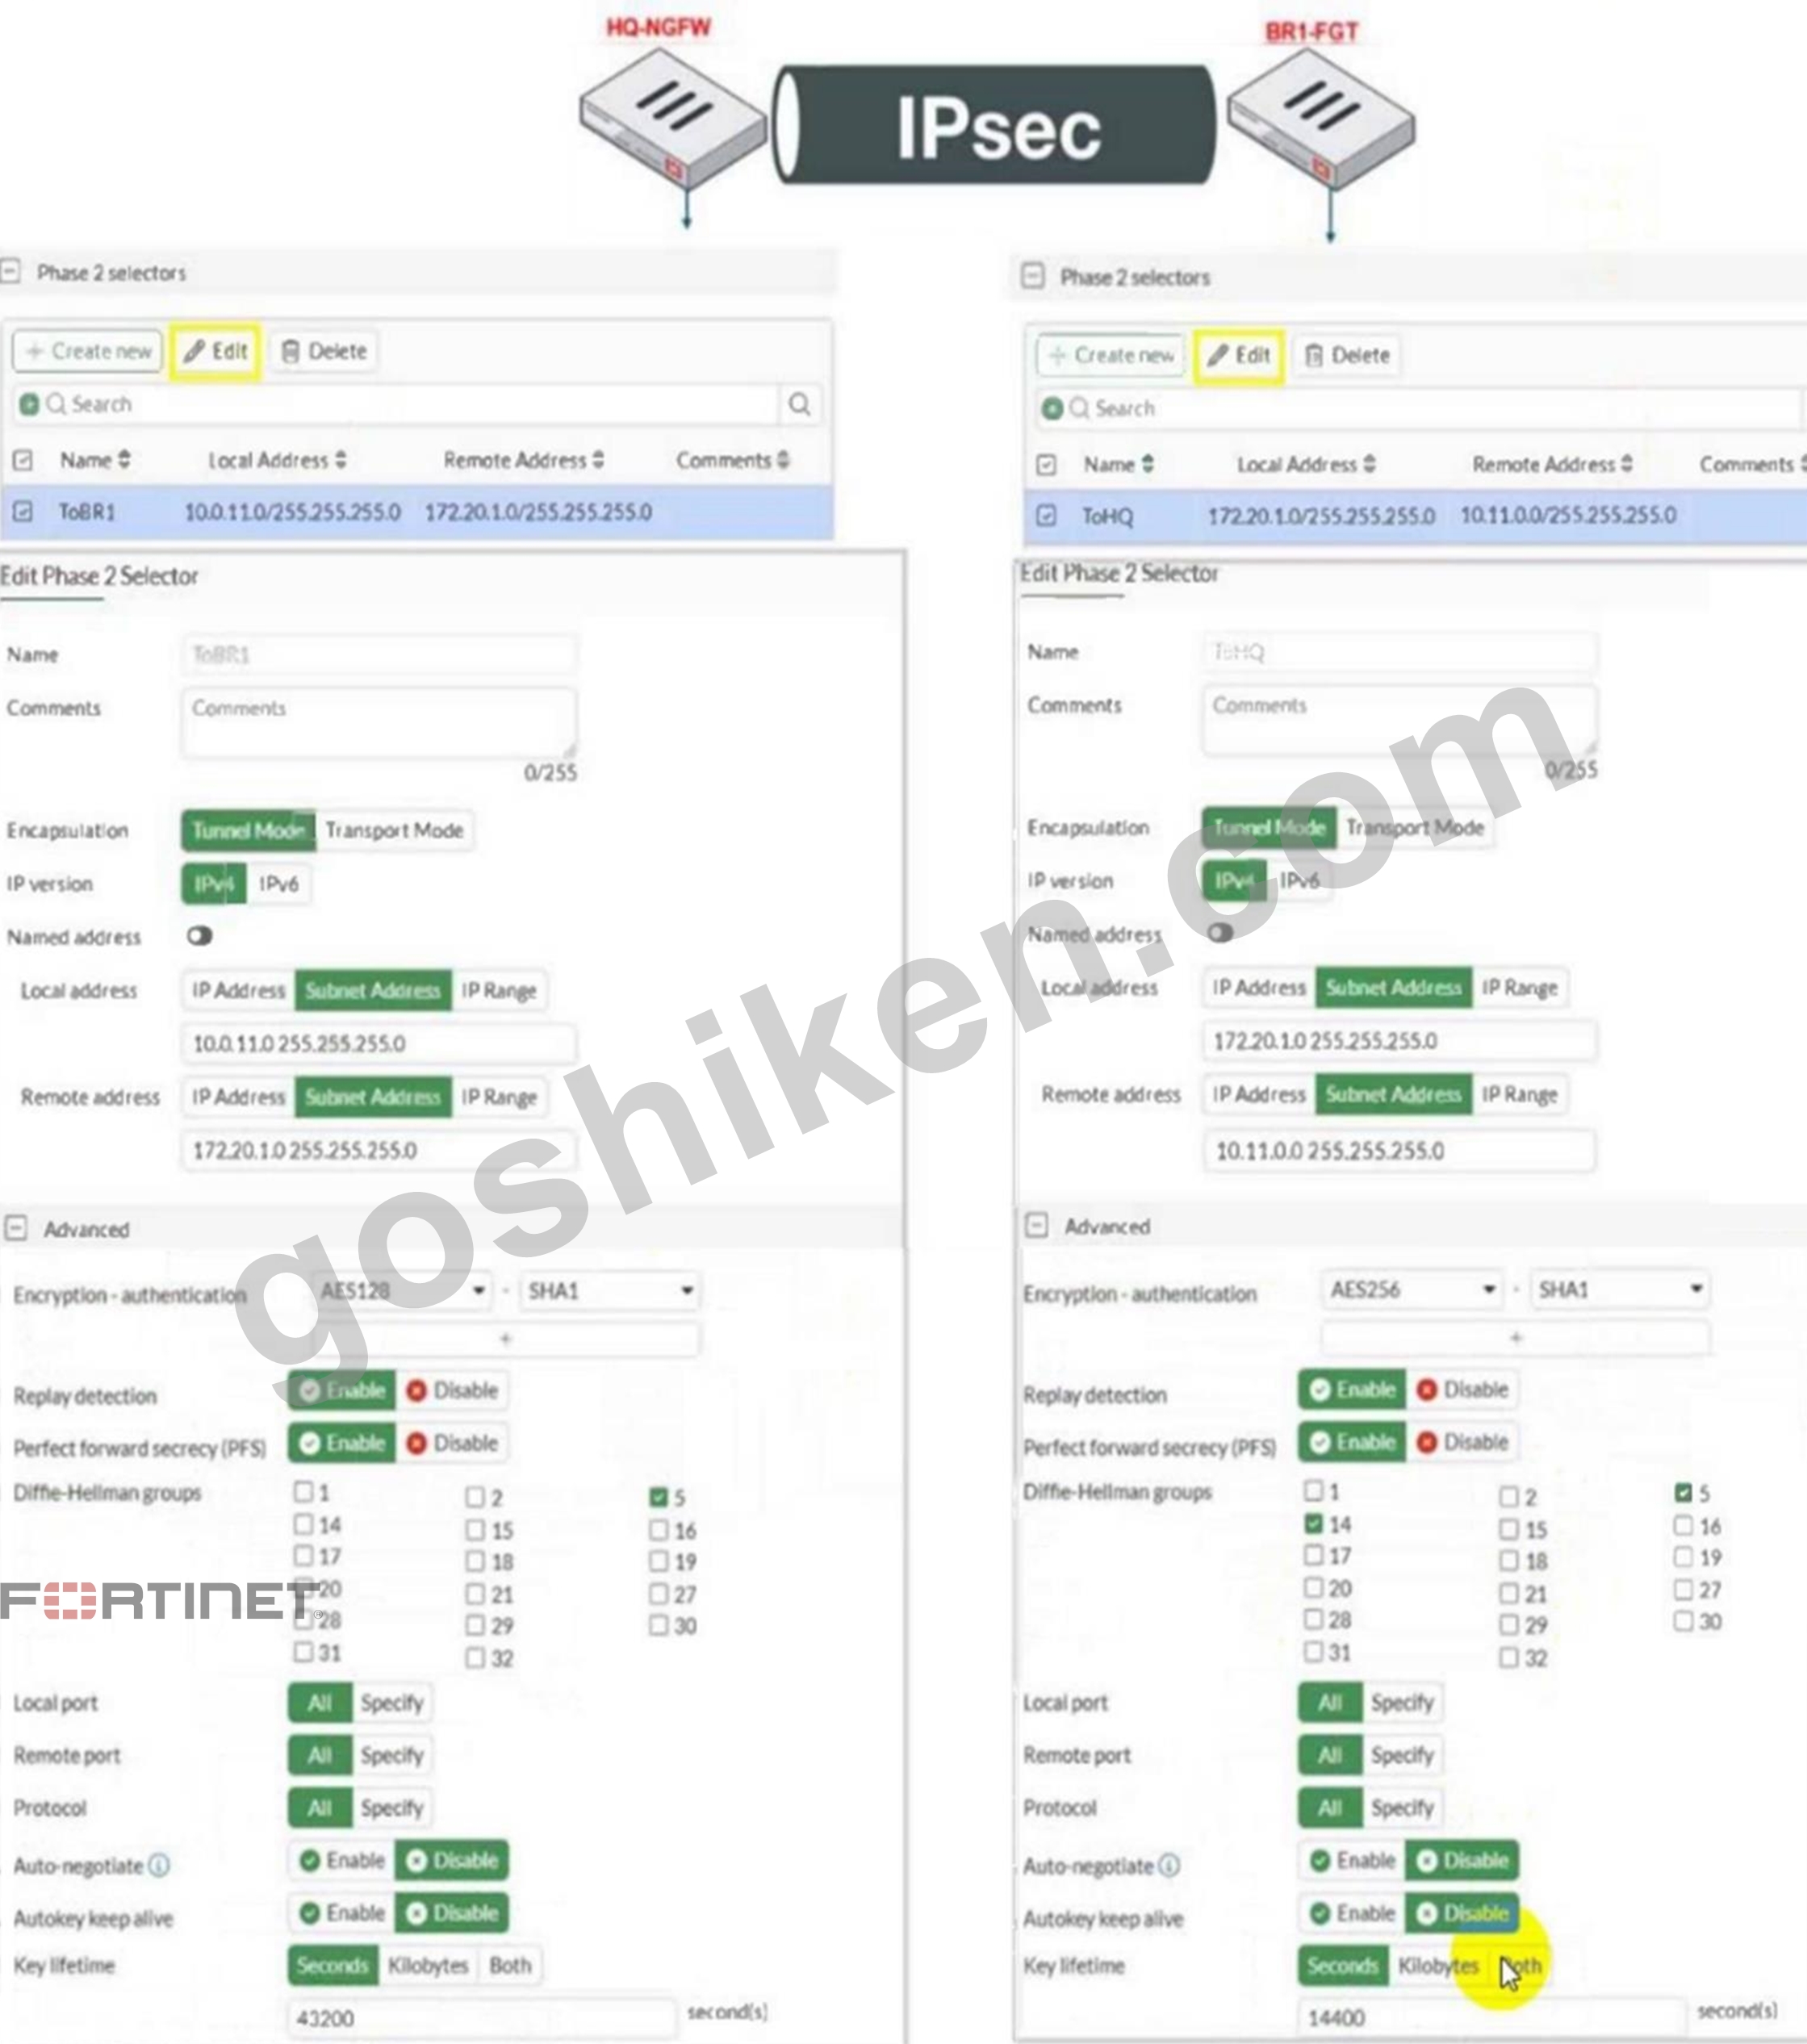
Based on the phase 2 configuration shown in the exhibit, which two configuration changes will bring phase 2 up? (Choose two.)
- A. On BR1-FGT, set Seconds to 43200.
- B. On HQ-NGFW. set Encryption to AES256.
- C. On BR1-FGT, set Remote Address to 10.0.11.0/255.255.255.0.
- D. On HQ-NGFW, enable Diffie-Hellman Group 2.
正解:A、C
解説:
The key lifetime (Seconds) must match on both sides; BR1-FGT is set to 14400, so setting it to
43200 matches HQ-NGFW.
The remote address on BR1-FGT should match the HQ-NGFW's local subnet (10.0.11.0/24), but it is currently set incorrectly as 172.20.1.0/24. Changing it to 10.0.11.0/255.255.255.0 will align the Phase 2 selectors.
質問 # 74
An administrator wants to configure dead peer detection (DPD) on IPsec VPN for detecting dead tunnels. The requirement is that FortiGate sends DPD probes only when there is no inbound traffic.
Which DPD mode on FortiGate meets this requirement?
- A. On Demand
- B. Enabled
- C. On Idle
- D. Disabled
正解:A
質問 # 75
An administrator has configured the following settings:
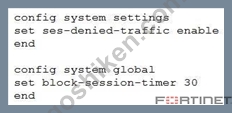
What are the two results of this configuration? (Choose two.)
- A. A session for denied traffic is created.
- B. The number of logs generated by denied traffic is reduced.
- C. Session helpers are disabled for denied traffic.
- D. Denied users are blocked for 30 minutes.
正解:A、B
解説:
set ses-denied-traffic enable → ensures FortiGate creates a session entry even for denied traffic.
set block-session-timer 30 → sets the duration (30 seconds) that denied sessions remain in the session table. This prevents repeated logging for every packet in the same denied flow, thereby reducing the number of logs generated.
質問 # 76
......
FCP_FGT_AD-7.6試験に実際に参加して資料を選択する前に、このような証明書を保持することの重要性を思い出してください。このようなFCP_FGT_AD-7.6証明書を取得することで、昇給、昇進の機会、上司や同僚からの信頼など、将来の多くの同意結果を習得できます。これらすべての快い結果は、もはやあなたにとって夢ではありません。そして、FCP_FGT_AD-7.6試験準備により、成績を改善し、生活の状態を変え、キャリアの驚くべき変化を得ることができ、すべてが可能になります。それはすべて、FCP_FGT_AD-7.6学習の質問から始まります。
FCP_FGT_AD-7.6テスト内容: https://www.goshiken.com/Fortinet/FCP_FGT_AD-7.6-mondaishu.html
- FCP_FGT_AD-7.6日本語版試験勉強法 🥮 FCP_FGT_AD-7.6対策学習 👻 FCP_FGT_AD-7.6最新テスト 🕔 ウェブサイト▶ www.it-passports.com ◀を開き、⏩ FCP_FGT_AD-7.6 ⏪を検索して無料でダウンロードしてくださいFCP_FGT_AD-7.6受験資料更新版
- FCP_FGT_AD-7.6テスト模擬問題集 😠 FCP_FGT_AD-7.6最新試験情報 😒 FCP_FGT_AD-7.6テスト模擬問題集 🐟 ➥ www.goshiken.com 🡄に移動し、“ FCP_FGT_AD-7.6 ”を検索して、無料でダウンロード可能な試験資料を探しますFCP_FGT_AD-7.6最新テスト
- 試験の準備方法-便利なFCP_FGT_AD-7.6受験対策書試験-実用的なFCP_FGT_AD-7.6テスト内容 ➰ ➡ www.passtest.jp ️⬅️で使える無料オンライン版▷ FCP_FGT_AD-7.6 ◁ の試験問題FCP_FGT_AD-7.6資格認定
- FCP_FGT_AD-7.6テスト模擬問題集 😚 FCP_FGT_AD-7.6過去問題 🕵 FCP_FGT_AD-7.6合格率書籍 🔟 サイト“ www.goshiken.com ”で▛ FCP_FGT_AD-7.6 ▟問題集をダウンロードFCP_FGT_AD-7.6受験資料更新版
- 試験の準備方法-認定するFCP_FGT_AD-7.6受験対策書試験-一番優秀なFCP_FGT_AD-7.6テスト内容 🕕 サイト[ www.passtest.jp ]で➤ FCP_FGT_AD-7.6 ⮘問題集をダウンロードFCP_FGT_AD-7.6認定試験トレーリング
- FCP_FGT_AD-7.6過去問題 🐵 FCP_FGT_AD-7.6受験内容 🕕 FCP_FGT_AD-7.6試験勉強攻略 ☣ [ FCP_FGT_AD-7.6 ]を無料でダウンロード{ www.goshiken.com }で検索するだけFCP_FGT_AD-7.6試験攻略
- 試験の準備方法-真実的なFCP_FGT_AD-7.6受験対策書試験-実用的なFCP_FGT_AD-7.6テスト内容 🔖 { www.goshiken.com }サイトにて( FCP_FGT_AD-7.6 )問題集を無料で使おうFCP_FGT_AD-7.6過去問題
- 試験の準備方法-素敵なFCP_FGT_AD-7.6受験対策書試験-効率的なFCP_FGT_AD-7.6テスト内容 🍜 ➠ www.goshiken.com 🠰から簡単に☀ FCP_FGT_AD-7.6 ️☀️を無料でダウンロードできますFCP_FGT_AD-7.6ブロンズ教材
- 最高のFCP_FGT_AD-7.6受験対策書一回合格-権威のあるFCP_FGT_AD-7.6テスト内容 🤮 【 jp.fast2test.com 】の無料ダウンロード【 FCP_FGT_AD-7.6 】ページが開きますFCP_FGT_AD-7.6テストサンプル問題
- 素晴らしいFCP_FGT_AD-7.6受験対策書 - 資格試験のリーダー - 100% パスレートFCP_FGT_AD-7.6: FCP - FortiGate 7.6 Administrator 🎤 ➤ www.goshiken.com ⮘サイトにて最新☀ FCP_FGT_AD-7.6 ️☀️問題集をダウンロードFCP_FGT_AD-7.6ブロンズ教材
- 最高のFCP_FGT_AD-7.6受験対策書一回合格-権威のあるFCP_FGT_AD-7.6テスト内容 Ⓜ ➠ jp.fast2test.com 🠰にて限定無料の⏩ FCP_FGT_AD-7.6 ⏪問題集をダウンロードせよFCP_FGT_AD-7.6最新テスト
-
learn.csisafety.com.au, devfolio.co, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, app.intigriti.com, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, zenwriting.net, www.stes.tyc.edu.tw, Disposable vapes
さらに、GoShiken FCP_FGT_AD-7.6ダンプの一部が現在無料で提供されています:https://drive.google.com/open?id=1V5yIVwuihVJUNRwHc-DKdyeLH4hSPz8g


 icons at the top
right corner of the subsection.