SC-200시험대비 덤프데모문제, SC-200적중율 높은 시험대비덤프, SC-200높은 통과율 시험대비자료, SC-200인기덤프문제, SC-200완벽한 시험기출자료
참고: Itcertkr에서 Google Drive로 공유하는 무료 2026 Microsoft SC-200 시험 문제집이 있습니다: https://drive.google.com/open?id=1MU6snQyTll7bWzuvCV0ch3MuNS_NKIUl
우리 Itcertkr 에는 최신의Microsoft SC-200학습가이드가 있습니다. Itcertkr의 부지런한 IT전문가들이 자기만의 지식과 끊임없는 노력과 경험으로 최고의Microsoft SC-200합습자료로Microsoft SC-200인증시험을 응시하실 수 있습니다.Microsoft SC-200인증시험은 IT업계에서의 비중은 아주 큽니다. 시험신청하시는분들도 많아지고 또 많은 분들이 우리Itcertkr의Microsoft SC-200자료로 시험을 패스했습니다. 이미 패스한 분들의 리뷰로 우리Itcertkr의 제품의 중요함과 정확함을 증명하였습니다.
Microsoft SC-200 Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| Topic 1: Mitigate threats using Microsoft 365 Defender |
25-30% |
- Hunt threats in Microsoft 365 Defender
- 1. Hunt for threats across devices, users, and mailboxes
- 2. Create custom detection rules
- 3. Use advanced hunting queries
- Investigate and respond to threats in Microsoft 365 Defender
- 1. Respond to compromised identities
- 2. Investigate alerts and incidents
- 3. Implement threat remediation actions
- 4. Manage investigations
- 5. Analyze evidence and threat intelligence
- Configure Microsoft 365 Defender settings
- 1. Configure alert notification settings
- 2. Configure Microsoft 365 Defender portal settings
- 3. Configure role-based access control
|
| Topic 2: Mitigate threats using Microsoft Defender for Identity |
15-20% |
- Hunt threats using Defender for Identity
- 1. Analyze security posture and recommendations
- 2. Investigate domain trust issues
- 3. Use identity evidence and timeline
- Investigate and respond to identity threats
- 1. Investigate compromised accounts
- 2. Investigate suspicious activities
- 3. Investigate lateral movement path alerts
- 4. Respond to identity-based alerts
- Configure Microsoft Defender for Identity
- 1. Configure sensor settings
- 2. Configure detection thresholds
- 3. Configure alert notifications
- 4. Configure role-based access control
|
| Topic 3: Mitigate threats using Microsoft Defender for Cloud Apps |
20-25% |
- Investigate and respond to threats
- 1. Investigate app activities and events
- 2. Investigate compromised user accounts
- 3. Investigate file activities
- 4. Respond to app alerts and governance actions
- Configure Microsoft Defender for Cloud Apps
- 1. Configure Conditional Access App Control
- 2. Configure app connectors and OAuth apps
- 3. Configure policies and alerts
- 4. Configure Cloud Discovery
- Hunt threats using Cloud Apps data
- 1. Use Cloud Discovery for shadow IT investigation
- 2. Create activity policies
- 3. Create anomaly detection policies
|
| Topic 4: Mitigate threats using Microsoft Defender for Endpoint |
25-30% |
- Hunt threats using advanced hunting
- 1. Investigate Zero Trust incidents
- 2. Monitor file and network activity
- 3. Create and execute KQL queries for threat hunting
- Configure Microsoft Defender for Endpoint environment
- 1. Configure attack surface reduction rules
- 2. Configure Windows Security settings
- 3. Configure device grouping and labeling
- 4. Configure role-based access control
- Manage devices and monitor threats
- 1. Onboard and offboard devices
- 2. Configure device proxy and connectivity settings
- 3. Respond to device alerts and incidents
- 4. Monitor devices and triage alerts
|
>> SC-200시험대비 덤프데모문제 <<
SC-200덤프공부 SC-200시험대비자료
Itcertkr 의 학습가이드에는Microsoft SC-200인증시험의 예상문제, 시험문제와 답입니다. 그리고 중요한 건 시험과 매우 유사한 시험문제와 답도 제공해드립니다. Itcertkr 을 선택하면 Itcertkr 는 여러분을 빠른시일내에 시험관련지식을 터득하게 할 것이고Microsoft SC-200인증시험도 고득점으로 패스하게 해드릴 것입니다.
최신 Microsoft Certified: Security Operations Analyst Associate SC-200 무료샘플문제 (Q316-Q321):
질문 # 316
HOTSPOT
From Azure Sentinel, you open the Investigation pane for a high-severity incident as shown in the following exhibit.
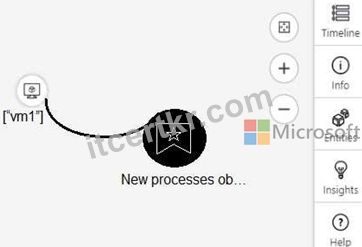
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Hot Area:
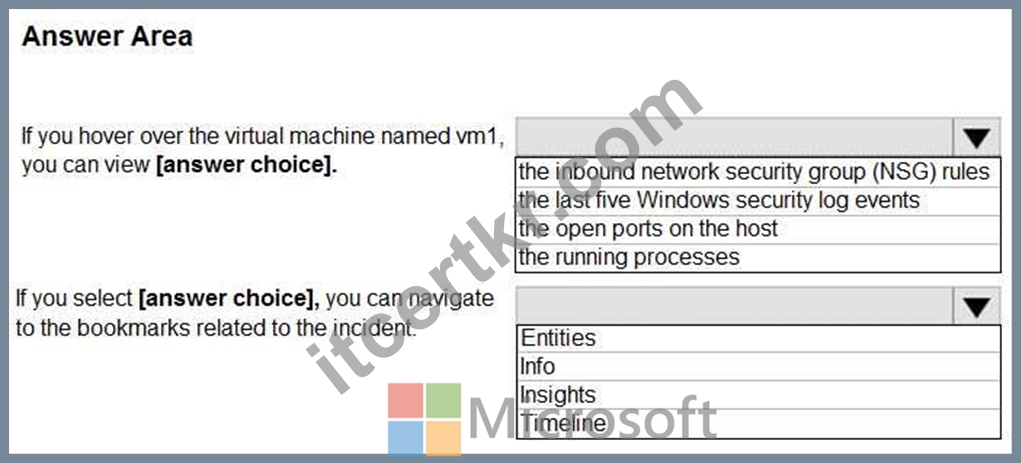
정답:
설명:
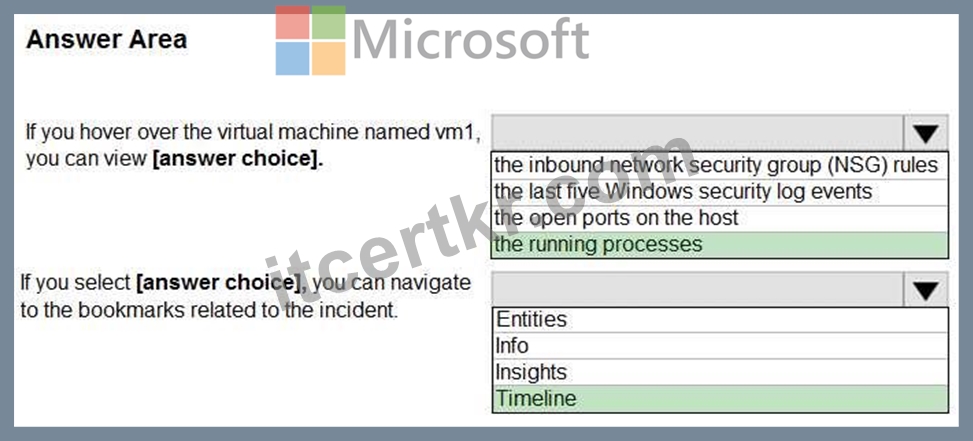
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-investigate-cases#use-the-investigation-graph-to-deep- dive
질문 # 317
You need to modify the anomaly detection policy settings to meet the Cloud App Security requirements.
Which policy should you modify?
- A. Activity from suspicious IP addresses
- B. Impossible travel
- C. Risky sign-in
- D. Activity from anonymous IP addresses
정답:B
설명:
The requirement states that Cloud App Security (Defender for Cloud Apps) must determine whether a user's connection is anomalous based on tenant-level patterns, and the current false positives occur when users connect through two office egress points at the same time. These symptoms align with the Impossible travel anomaly detection policy, which learns normal sign-in geolocation patterns and flags sign-ins from distant locations within an unrealistically short time window. To meet the requirement and reduce false positives, you modify the Impossible travel policy settings-such as excluding trusted corporate IP ranges/VPN egress points and tuning sensitivity-so detections better reflect tenant-wide behavior rather than isolated user hops via different office exits. Policies like Activity from anonymous/suspicious IP addresses rely on threat-intel lists of anonymizers or known-bad sources and don't address the "two-office" scenario. Risky sign-in is part of Azure AD Identity Protection, not the MCAS anomaly policy to tune here. Thus, the policy to modify is Impossible travel.
질문 # 318
You have an Azure subscription that contains the following resources:
* A virtual machine named VM1 that runs Windows Server
* A Microsoft Sentinel workspace named Sentinel1 that has User and Entity Behavior Analytics (UEBA) enabled You have a scheduled query rule named Rule1 that tracks sign-in attempts to VM1.
You need to update Rule 1 to detect when a user from outside the IT department of your company signs in to VM1. The solution must meet the following requirements:
* Utilize UEBA results.
* Maximize query performance.
* Minimize the number of false positives.
How should you complete the rule definition? To answer select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
정답:
설명:
Explanation:
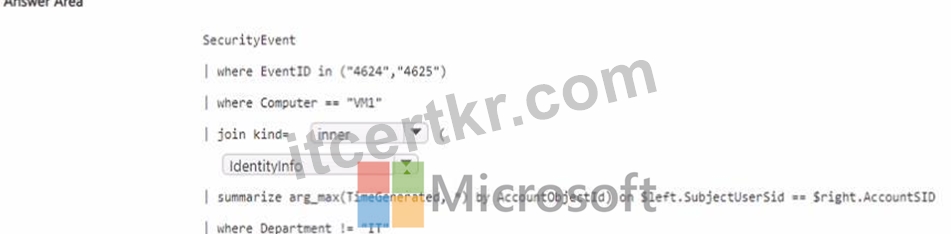
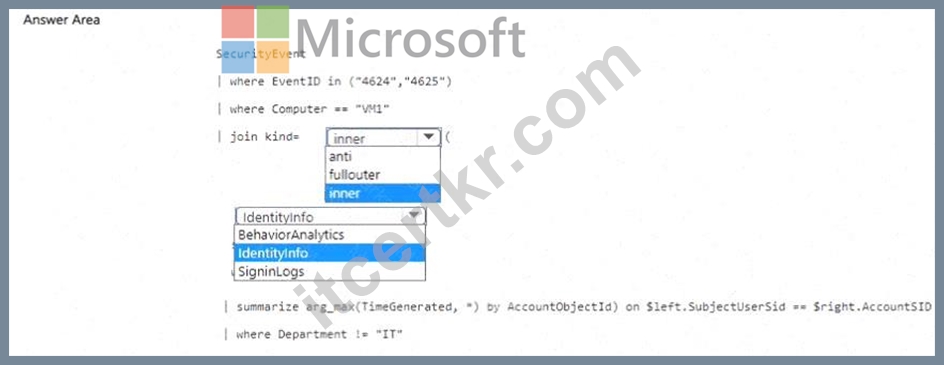
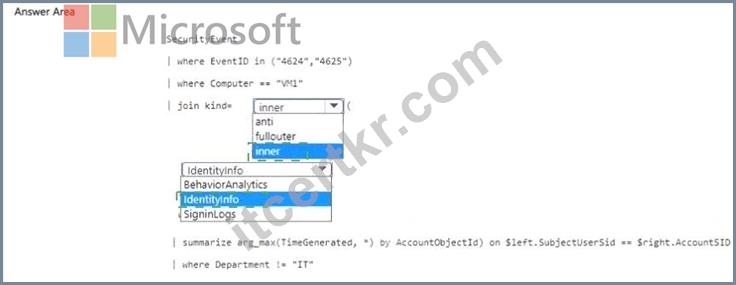
To detect sign-ins to VM1 by users outside the IT department while leveraging UEBA, you should enrich Windows security events with identity attributes from UEBA's enrichment tables . In Microsoft Sentinel, UEBA writes organizational attributes (e.g., Department, Title, AAD object IDs/SIDs) to the IdentityInfo table. Joining SecurityEvent (Event IDs 4 624/4625) with IdentityInfo on the user SID lets you filter with where Department != " IT " -meeting the requirement to utilize UEBA results .
For performance and fewer false positives, use join kind=inner . An inner join only returns rows where the user in Sec urityEvent has a corresponding identity record in IdentityInfo , avoiding unmatched and potentially noisy events. Options like fullouter would introduce non-matching rows (increasing noise), and anti would return only unmatched rows (the opposite of what's needed).
BehaviorAnalytics contains anomaly scores/events rather than static attributes like department, and SigninLogs is raw AAD sign-in telemetry (not the UEBA-enriched identity inventory needed for department filtering). Therefore, IdentityInfo is the correct enrichment source.
Thus, to satisfy use UEBA, maximize performance, and minimize false positives : join kind=inner with IdentityInfo and then filter Department != " IT " .
질문 # 319
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint Plan 2 and contains a macOS device named Device1.
You need to investigate a Defender for Endpoint agent alert on Device1. The solution must meet the following requirements:
- Identify all the active network connections on Device1.
- Identify all the running processes on Device1.
- Retrieve the login history of Device1.
- Minimize administrative effort.
What should you do first from the Microsoft Defender portal?
- A. From Devices, initiate a live response session on Device1.
- B. From Advanced features in Endpoints, disable Authenticated telemetry.
- C. From Devices, click Collect investigation package for Device1.
- D. From Advanced features in Endpoints, enable Live Response unsigned script execution.
정답:C
설명:
The investigation package collected by defender includes all the required information and is considerable less admin effort than running a live response session and collecting this information interactively.
https://learn.microsoft.com/en-us/defender-endpoint/respond-machine-alerts?view=o365- worldwide#collect-investigation-package-from-devices
질문 # 320
You have an Azure subscription that has Azure Defender enabled for all supported resource types.
You create an Azure logic app named LA1.
You plan to use LA1 to automatically remediate security risks detected in Defenders for Cloud .
You need to test LA1 in Defender for Cloud .
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
정답:
설명:
Explanation:
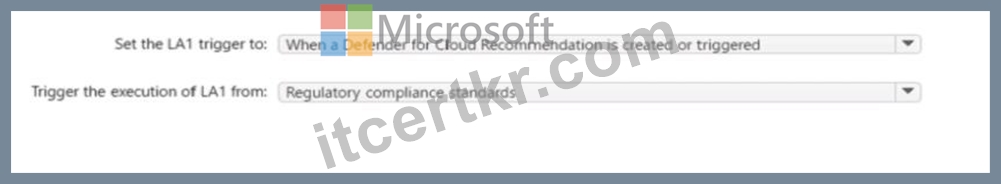
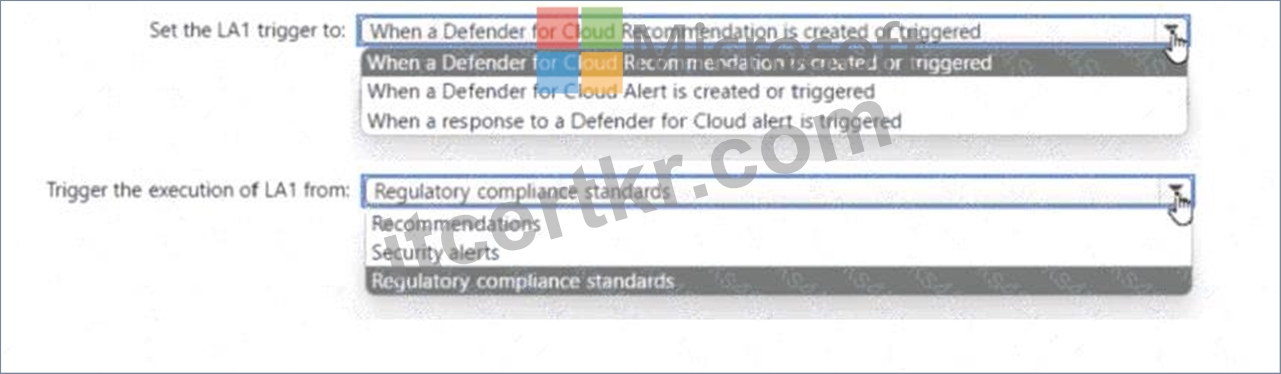
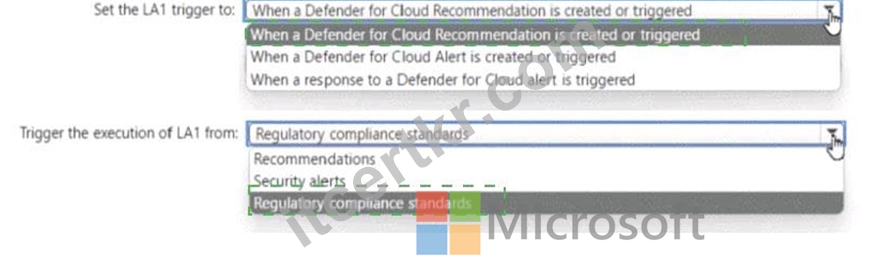
According to Microsoft Defender for Cloud automation documentation, Logic Apps can be integrated to automatically respond to recommendations or alerts. To test or automate remediation from Defender for Cloud , you must configure an automation workflow (Logic App) that triggers when a recommendation is created or updated.
Microsoft defines the available triggers for Defender for Cloud automation as follows:
* When a Defender for Cloud Recommendation is created or triggered - This event type initiates the Logic App whenever a new se curity recommendation appears or an existing one changes state. It's the proper trigger for remediation scenarios because recommendations typically indicate a detected security misconfiguration or risk requiring action.
* When a Defender for Cloud Alert is c reated or triggered - This applies to security alerts, not recommendations.
* When a response to a Defender for Cloud alert is triggered - Used for incident-response workflows, not for testing remediation logic.
In the context of the question, the goal is to test automatic remediation for detected configuration issues (security risks). Those are surfaced as recommendations within Defender for Cloud, not as alerts.
Next, the execution source should be configured under:
* Trigger the execution of LA1 from: Recomm endations
This ensures that Defender for Cloud will execute the Logic App (LA1) automatically when relevant recommendations are triggered, allowing immediate testing and validation of the remediation logic.
In summary:
To test the Logic App remediation wor kflow in Defender for Cloud, you must:
* Set the trigger type to "When a Defender for Cloud Recommendation is created or triggered" .
* Configure it to execute from "Recommendations" .
Thus, the verified correct answers are:
# Set the LA1 trigger to: When a Defender for Cloud Recommendation is created or triggered
# Trigger the execution of LA1 from: Recommendations
질문 # 321
......
Itcertkr의 Microsoft인증 SC-200덤프로 시험공부를 하신다면 고객님의 시간은 물론이고 거금을 들여 학원등록하지 않아도 되기에 금전상에서도 많은 절약을 해드리게 됩니다. Microsoft인증 SC-200덤프 구매의향이 있으시면 무료샘플을 우선 체험해보세요.
SC-200적중율 높은 시험대비덤프: https://www.itcertkr.com/SC-200_exam.html
- SC-200최고품질 인증시험 기출문제 🧏 SC-200최고덤프공부 👰 SC-200시험대비 덤프문제 🥠 ➡ www.dumptop.com ️⬅️을 통해 쉽게⏩ SC-200 ⏪무료 다운로드 받기SC-200최신 업데이트버전 덤프문제공부
- SC-200시험대비 덤프데모문제최신버전 인증공부문제 🦸 ▶ SC-200 ◀를 무료로 다운로드하려면[ www.itdumpskr.com ]웹사이트를 입력하세요SC-200시험대비 덤프문제
- 시험패스에 유효한 SC-200시험대비 덤프데모문제 덤프문제 ⚜ 검색만 하면“ kr.fast2test.com ”에서{ SC-200 }무료 다운로드SC-200시험대비 최신 덤프문제
- SC-200시험대비 덤프데모문제최신버전 인증공부문제 🕺 오픈 웹 사이트➽ www.itdumpskr.com 🢪검색{ SC-200 }무료 다운로드SC-200최신 업데이트버전 덤프문제공부
- SC-200시험대비 덤프데모문제 완벽한 덤프문제 ◀ 무료 다운로드를 위해⏩ SC-200 ⏪를 검색하려면➤ kr.fast2test.com ⮘을(를) 입력하십시오SC-200최신 시험 예상문제모음
- SC-200 100%시험패스 공부자료 🏵 SC-200최신 업데이트 인증덤프자료 🕥 SC-200최신버전 인기 시험자료 💼 ➤ www.itdumpskr.com ⮘에서 검색만 하면⮆ SC-200 ⮄를 무료로 다운로드할 수 있습니다SC-200최신버전 시험덤프문제
- SC-200최신버전 시험덤프문제 🕎 SC-200합격보장 가능 시험 🕐 SC-200퍼펙트 인증공부 😣 《 www.koreadumps.com 》을 통해 쉽게“ SC-200 ”무료 다운로드 받기SC-200덤프샘플문제
- SC-200덤프샘플문제 📅 SC-200덤프샘플문제 ⏬ SC-200최신버전 시험덤프문제 ⬇ [ www.itdumpskr.com ]을 통해 쉽게「 SC-200 」무료 다운로드 받기SC-200최고품질 인증시험 기출문제
- SC-200덤프샘플문제 🛸 SC-200최고덤프공부 ↪ SC-200높은 통과율 시험대비 공부문제 📩 무료로 다운로드하려면( www.dumptop.com )로 이동하여「 SC-200 」를 검색하십시오SC-200인기자격증 인증시험덤프
- SC-200시험대비 최신 덤프문제 🚝 SC-200최신 업데이트 인증덤프자료 🕯 SC-200인증덤프샘플 다운 📔 { www.itdumpskr.com }웹사이트를 열고“ SC-200 ”를 검색하여 무료 다운로드SC-200최고품질 인증시험 기출문제
- SC-200시험대비 덤프데모문제 완벽한 덤프문제 🔭 ➤ kr.fast2test.com ⮘은⏩ SC-200 ⏪무료 다운로드를 받을 수 있는 최고의 사이트입니다SC-200덤프샘플문제
-
mayagriffiths253.blogspot.com, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, github.com, www.stes.tyc.edu.tw, Disposable vapes
참고: Itcertkr에서 Google Drive로 공유하는 무료, 최신 SC-200 시험 문제집이 있습니다: https://drive.google.com/open?id=1MU6snQyTll7bWzuvCV0ch3MuNS_NKIUl


 icons at the top
right corner of the subsection.