FCSS_EFW_AD-7.6対応内容, FCSS_EFW_AD-7.6基礎問題集, FCSS_EFW_AD-7.6試験解説問題, FCSS_EFW_AD-7.6日本語, FCSS_EFW_AD-7.6テスト参考書

さらに、GoShiken FCSS_EFW_AD-7.6ダンプの一部が現在無料で提供されています:https://drive.google.com/open?id=1Fpvu2R-c9egBzktd5btfo1q67AfECuYP
近年、社会の急速な発展に伴って、IT業界は人々に爱顾されました。Fortinet FCSS_EFW_AD-7.6IT認定試験を受験して認証資格を取ることを通して、IT事業を更に上がる人は多くになります。そのときは、あなたにとって必要するのはあなたのFortinet FCSS_EFW_AD-7.6試験合格をたすけってあげるのGoShikenというサイトです。GoShikenの素晴らしい問題集はIT技術者が長年を重ねて、総括しました経験と結果です。先人の肩の上に立って、あなたも成功に一歩近付くことができます。
Fortinet FCSS_EFW_AD-7.6 Exam Syllabus Topics:
| Section |
Objectives |
| Topic 1: VPN Technologies |
- SSL VPN
- 1. Remote access configuration
- IPsec VPN
- 1. Site-to-site VPN configuration
- 2. Route-based vs policy-based VPN
|
| Topic 2: Security Policies and Profiles |
- Security profiles
- 1. Antivirus, IPS, Web filtering
- 2. Application control and SSL inspection
- Firewall policies
- 1. Central NAT and policy order
|
| Topic 3: Monitoring, Logging, and Troubleshooting |
- System monitoring
- 1. Logs, reports, and diagnostics
- Troubleshooting tools
- 1. Packet capture and flow debugging
|
| Topic 4: High Availability and Redundancy |
- HA clustering
- 1. Failover behavior and synchronization
- 2. Active-passive and active-active modes
|
| Topic 5: FortiGate Deployment and Administration |
- Initial system setup and configuration
- 1. Basic system settings and interfaces
- 2. Device onboarding and licensing
|
| Topic 6: Routing and SD-WAN |
- Dynamic and static routing
- 1. Policy-based routing
- 2. OSPF/BGP integration basics
- SD-WAN configuration
- 1. Performance SLA and traffic steering
|
>> FCSS_EFW_AD-7.6対応内容 <<
FCSS_EFW_AD-7.6基礎問題集、FCSS_EFW_AD-7.6試験解説問題
ほぼ100%の通過率は我々のお客様からの最高のプレゼントです。我々は弊社のFortinetのFCSS_EFW_AD-7.6試験の資料はより多くの夢のある人にFortinetのFCSS_EFW_AD-7.6試験に合格させると希望します。我々のチームは毎日資料の更新を確認していますから、ご安心ください、あなたの利用しているソフトは最も新しく全面的な資料を含めています。
Fortinet FCSS - Enterprise Firewall 7.6 Administrator 認定 FCSS_EFW_AD-7.6 試験問題 (Q74-Q79):
質問 # 74
Refer to the exhibits. The exhibits show a network topology, a firewall policy, and an SSL/SSH inspection profile configuration.
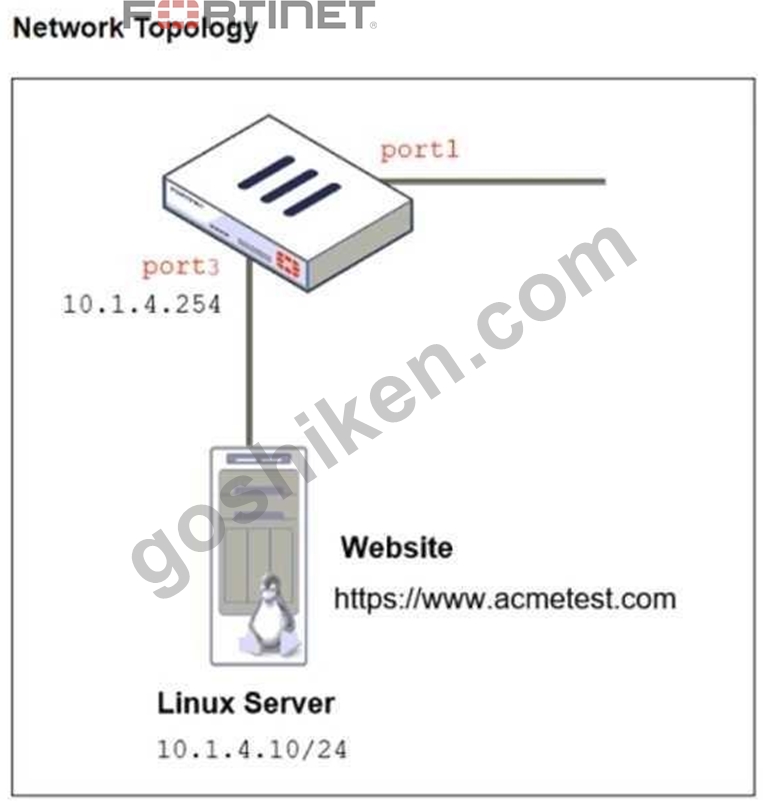
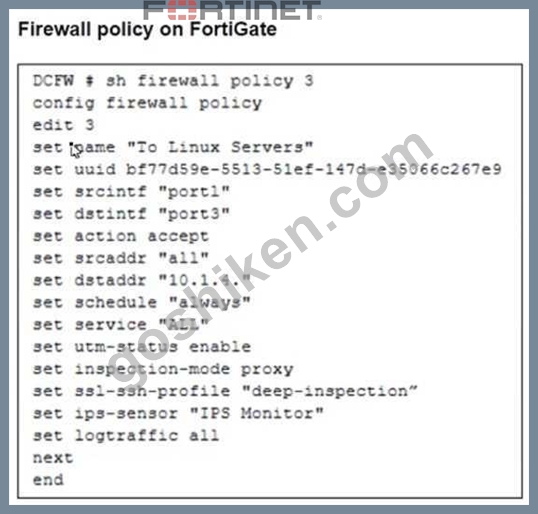
Why is FortiGate unable to detect HTTPS attacks on firewall policy ID 3 targeting the Linux server?
- A. The administrator must enable SSL inspection of the SSL server and upload the certificate of the Linux server website to the SSL/SSH inspection profile.
- B. The administrator must enable HTTPS in the protocol port mapping of the deep- inspection SSL/SSH inspection profile.
- C. The administrator must enable cipher suites in the SSL/SSH inspection profile to decrypt the message.
- D. The administrator must set the policy to inspection mode to analyze the HTTPS packets as expected.
正解:A
解説:
The FortiGate SSL/SSH inspection profile is configured for Full SSL Inspection, which is necessary to analyze encrypted HTTPS traffic. However, the firewall policy is protecting an SSL server (the Linux server hosting the website), and currently, the SSL/SSH profile only applies to client-side SSL inspection.
To detect HTTPS-based attacks targeting the Linux server:
FortiGate must act as an SSL intermediary to inspect encrypted traffic destined for the web server. The administrator must upload the SSL certificate of the Linux web server to FortiGate so that the server-side SSL inspection can decrypt incoming HTTPS traffic before analyzing it.
質問 # 75
Refer to the exhibit, which shows an enterprise network connected to an internet service provider.
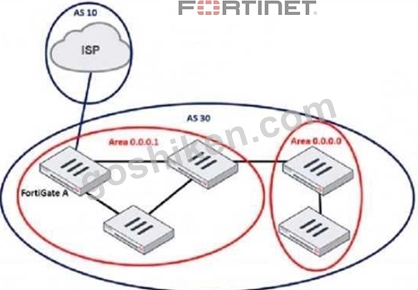
The administrator must configure the BGP section of FortiGate A to give internet access to the enterprise network.
Which command must the administrator use to establish a connection with the internet service provider?
- A. config neighbor
- B. config redistribute bgp
- C. config redistribute ospf
- D. config router route-map
正解:A
解説:
In BGP (Border Gateway Protocol), a neighbor (peer) configuration is required to establish a connection between two BGP routers. Since FortiGate A is connecting to the ISP (Autonomous System 10) from AS 30, the administrator must define the ISP's BGP router as a neighbor.
The config neighbor command is used to:
Define the ISP's IP address as a BGP peer
Specify the remote AS (AS 10 in this case)
Allow BGP route exchanges between FortiGate A and the ISP
質問 # 76
Refer to the exhibits.
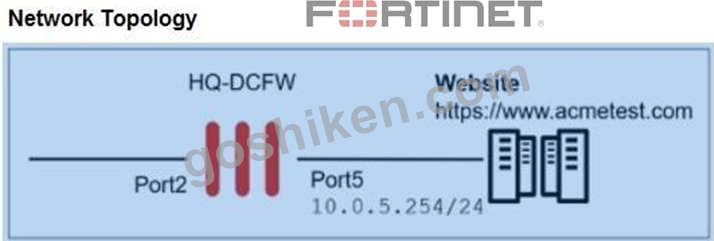
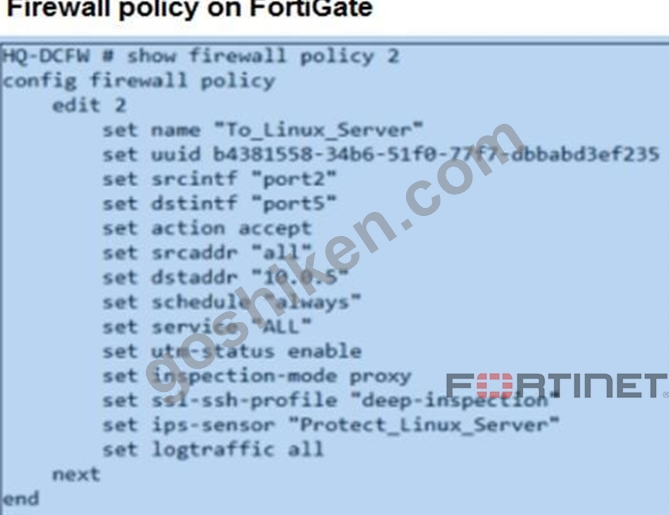
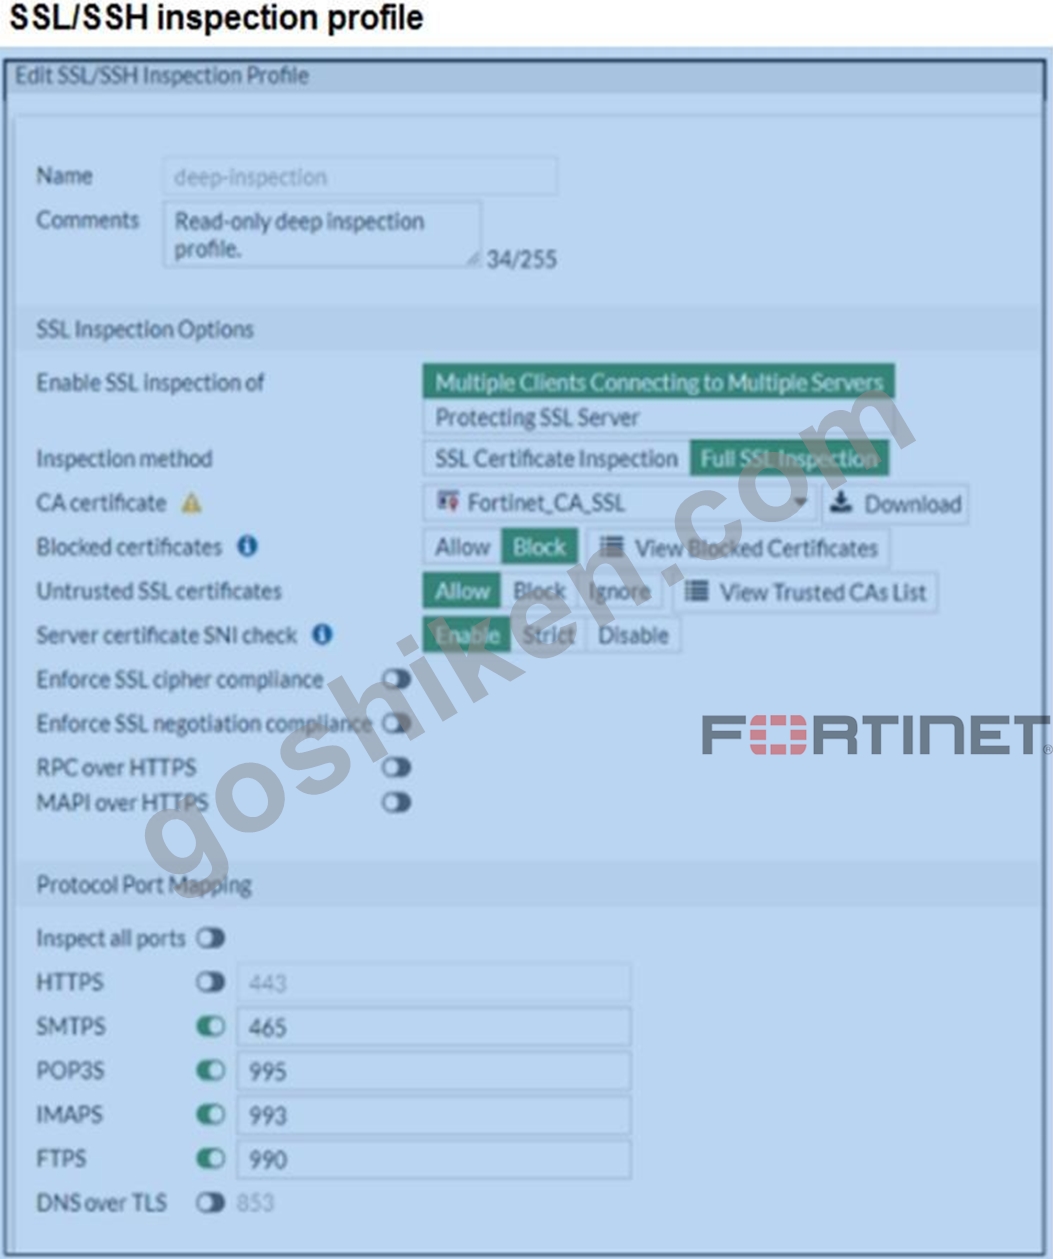
A network topology, firewall policy, and SSL/SSH inspection profile configuration are shown.
What must you configure on firewall policy ID 2 to detect HTTPS attacks that target a Linux server hosting the website
- A. Enable SSL inspection of the SSL server and upload the certificate of the Linux server website to the SSL/SSH inspection profile.
- B. Set inspection-mode to f1ow to analyze the HTTPS packets and make sure that they are as expected.
- C. Set ips-sensor to IPS_block in the firewall policy.
- D. Enable HTTPS in the protocol port mapping of the deep-inspection SSL/SSH inspection profile.
正解:A
解説:
To detect attacks hidden inside inbound HTTPS traffic destined for the Linux web server, FortiGate must decrypt that server-side SSL traffic before the IPS sensor can inspect it. That requires configuring the SSL/SSH inspection profile to protect an SSL server and importing the website certificate used by the Linux server so FortiGate can perform full inspection of the HTTPS session.
質問 # 77
Refer to the exhibit, which shows a LAN interface connected from FortiGate to two FortiSwitch devices.
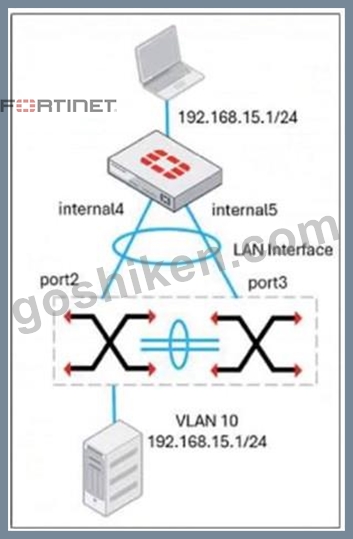
What two conclusions can you draw from the corresponding LAN interface? (Choose two.)
- A. This connection is using a FortiLInk to manage VLANs on FortiGate.
- B. FortiGate is using an SD-WAN-type interface to connect to a FortiSwitch device with MCLAG.
- C. The LAN interface must use a 802.3ad type interface.
- D. You must enable STP or RSTP on FortiGate and FortiSwitch to avoid layer 2 loopbacks.
正解:A、C
解説:
The diagram shows a FortiGate connected to two FortiSwitches, which suggests the use of FortiLink, Fortinet's protocol for managing switches directly from a FortiGate. Since multiple connections are being used, the LAN interface must be set to 802.3ad (LAG) mode to aggregate the links for redundancy and load balancing.
This setup allows FortiGate to handle VLAN assignments dynamically, as seen with VLAN 10 (192.168.15.1/24). FortiLink ensures seamless integration between FortiGate and FortiSwitches, making STP unnecessary because Fortinet's MCLAG prevents loops at Layer 2. SD-WAN, on the other hand, is used for WAN interfaces and does not apply to switch connectivity in this scenario.
質問 # 78
How do you allow IPS inspection of inbound HTTPS traffic?
- A. Disable inspection
- B. Enable HTTP
- C. Enable HTTPS mapping
- D. Enable SMTPS
正解:C
質問 # 79
......
FortinetのFCSS_EFW_AD-7.6試験に合格するためにたくさんの方法がありますが、我々GoShikenの提供する方法は一番効果的なのです。我々IT専門かたちの作成するFortinetのFCSS_EFW_AD-7.6ソフトを利用しているとき、あなたは自分の能力の高めを明らかに感じることができます。FortinetのFCSS_EFW_AD-7.6試験は常に更新されていますから、あなたに一番新しい資料を提供するために、我々はご購入の後で一年間の無料更新サービスを提供してあなたに安心させます。
FCSS_EFW_AD-7.6基礎問題集: https://www.goshiken.com/Fortinet/FCSS_EFW_AD-7.6-mondaishu.html
- FCSS_EFW_AD-7.6模擬試験最新版 ✅ FCSS_EFW_AD-7.6資格練習 🏅 FCSS_EFW_AD-7.6試験関連情報 🦄 サイト《 www.xhs1991.com 》で➥ FCSS_EFW_AD-7.6 🡄問題集をダウンロードFCSS_EFW_AD-7.6科目対策
- FCSS_EFW_AD-7.6試験情報 🧇 FCSS_EFW_AD-7.6資格取得講座 🧧 FCSS_EFW_AD-7.6資格練習 🌼 ▛ www.goshiken.com ▟は、✔ FCSS_EFW_AD-7.6 ️✔️を無料でダウンロードするのに最適なサイトですFCSS_EFW_AD-7.6資格取得講座
- 便利なFCSS_EFW_AD-7.6対応内容 - 合格スムーズFCSS_EFW_AD-7.6基礎問題集 | 有効的なFCSS_EFW_AD-7.6試験解説問題 🕡 ( www.passtest.jp )を開いて【 FCSS_EFW_AD-7.6 】を検索し、試験資料を無料でダウンロードしてくださいFCSS_EFW_AD-7.6資格問題集
- FCSS_EFW_AD-7.6資格問題集 ✌ FCSS_EFW_AD-7.6資格取得講座 🏡 FCSS_EFW_AD-7.6試験情報 💁 今すぐ{ www.goshiken.com }で✔ FCSS_EFW_AD-7.6 ️✔️を検索し、無料でダウンロードしてくださいFCSS_EFW_AD-7.6日本語版問題集
- FCSS_EFW_AD-7.6模試エンジン 💧 FCSS_EFW_AD-7.6日本語対策問題集 🚍 FCSS_EFW_AD-7.6試験参考書 🌜 ➤ www.passtest.jp ⮘は、➡ FCSS_EFW_AD-7.6 ️⬅️を無料でダウンロードするのに最適なサイトですFCSS_EFW_AD-7.6ファンデーション
- FCSS_EFW_AD-7.6日本語版復習指南 🦞 FCSS_EFW_AD-7.6模擬試験最新版 🔌 FCSS_EFW_AD-7.6科目対策 🛢 ➤ www.goshiken.com ⮘で使える無料オンライン版➠ FCSS_EFW_AD-7.6 🠰 の試験問題FCSS_EFW_AD-7.6資格問題集
- 真実的なFCSS_EFW_AD-7.6対応内容試験-試験の準備方法-ハイパスレートのFCSS_EFW_AD-7.6基礎問題集 📐 ➤ www.it-passports.com ⮘で使える無料オンライン版▷ FCSS_EFW_AD-7.6 ◁ の試験問題FCSS_EFW_AD-7.6試験問題解説集
- FCSS_EFW_AD-7.6科目対策 🚣 FCSS_EFW_AD-7.6資格練習 ⛪ FCSS_EFW_AD-7.6模擬試験最新版 🍆 サイト☀ www.goshiken.com ️☀️で[ FCSS_EFW_AD-7.6 ]問題集をダウンロードFCSS_EFW_AD-7.6日本語版問題集
- 便利なFCSS_EFW_AD-7.6対応内容 - 合格スムーズFCSS_EFW_AD-7.6基礎問題集 | 有効的なFCSS_EFW_AD-7.6試験解説問題 🖱 ⏩ www.passtest.jp ⏪サイトにて⏩ FCSS_EFW_AD-7.6 ⏪問題集を無料で使おうFCSS_EFW_AD-7.6日本語対策問題集
- 素敵なFCSS_EFW_AD-7.6対応内容試験-試験の準備方法-更新するFCSS_EFW_AD-7.6基礎問題集 🥅 ▶ www.goshiken.com ◀に移動し、“ FCSS_EFW_AD-7.6 ”を検索して、無料でダウンロード可能な試験資料を探しますFCSS_EFW_AD-7.6模擬試験最新版
- 便利なFCSS_EFW_AD-7.6対応内容 - 合格スムーズFCSS_EFW_AD-7.6基礎問題集 | 有効的なFCSS_EFW_AD-7.6試験解説問題 🦳 ➠ www.mogiexam.com 🠰には無料の➤ FCSS_EFW_AD-7.6 ⮘問題集がありますFCSS_EFW_AD-7.6練習問題集
-
www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes
さらに、GoShiken FCSS_EFW_AD-7.6ダンプの一部が現在無料で提供されています:https://drive.google.com/open?id=1Fpvu2R-c9egBzktd5btfo1q67AfECuYP


 icons at the top
right corner of the subsection.