NSE7_SSE_AD-25認定試験, NSE7_SSE_AD-25関連資料, NSE7_SSE_AD-25日本語版対策ガイド, NSE7_SSE_AD-25日本語学習内容, NSE7_SSE_AD-25関連日本語内容

BONUS!!! GoShiken NSE7_SSE_AD-25ダンプの一部を無料でダウンロード:https://drive.google.com/open?id=15Xxb2V_wSb3NasrNV33gkVrvf4hQtr4a
GoShikenはあなたの100パーセントの合格率を保証します。例外がないです。いまGoShikenを選んで、あなたが始めたいトレーニングを選んで、しかも次のテストに受かったら、最も良いソース及び市場適合性と信頼性を得ることができます。GoShikenのFortinetのNSE7_SSE_AD-25問題集と解答はNSE7_SSE_AD-25認定試験に一番向いているソフトです。
Fortinet NSE7_SSE_AD-25 認定試験の出題範囲:
| トピック |
出題範囲 |
| トピック 1 |
- SASE architecture and integration: This domain covers integrating FortiSASE into existing networks, identifying core SASE components, and evaluating their roles in advanced deployment scenarios.
|
| トピック 2 |
- SASE deployment and management: This section focuses on deploying and managing FortiSASE for branch and remote users, configuring advanced inspection features, and managing endpoint profiles and compliance rules.
|
| トピック 3 |
- Secure Private Access (SPA): This domain includes designing SPA use cases, deploying SPA with SD-WAN, and implementing ZTNA with tagging rules and access proxy configurations.
|
| トピック 4 |
- Analytics: This section covers troubleshooting connectivity and endpoint issues, analyzing dashboards and logs, and reviewing reports related to user traffic and security events.
|
>> NSE7_SSE_AD-25認定試験 <<
Fortinet NSE7_SSE_AD-25関連資料 & NSE7_SSE_AD-25日本語版対策ガイド
当社は長年にわたり、クライアントに最高のNSE7_SSE_AD-25練習問題を提供し、テストNSE7_SSE_AD-25認定試験にスムーズに合格できるように常に努めています。当社は、国内の有名な業界の専門家を募集し、優秀な人材をNSE7_SSE_AD-25学習ガイドを編集し、お客様に心から奉仕するために最善を尽くしました。当社は、お客様が私たちの神であり、NSE7_SSE_AD-25トレーニング資料の品質に関する厳格な基準であるというサービス理念を設定しています。
Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator 認定 NSE7_SSE_AD-25 試験問題 (Q73-Q78):
質問 # 73
Refer to the exhibit.
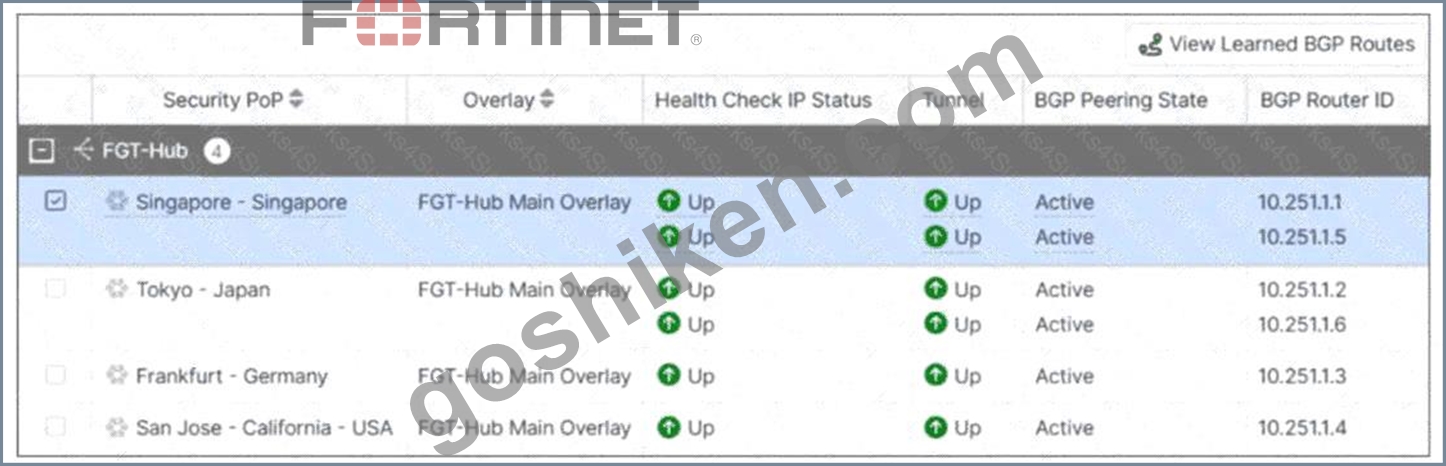
An SPA service connection is experiencing connectivity problems. Which configuration setting should the administrator verify and correct first? (Choose one answer)
- A. BGP Peer IP
- B. Network overlay ID
- C. Remote Gateway
- D. Authentication Method
正解:A
解説:
In FortiSASE Secure Private Access (SPA) deployments, establishing a stable connection between the FortiSASE PoPs and the corporate FortiGate hub relies on two primary layers: the IPsec Tunnel and the BGP Peering .
* Exhibit Analysis: The exhibit (image_577e17.jpg) shows the status of several Security PoPs (Singapore, Tokyo, Frankfurt, and San Jose) connected to an " FGT-Hub " .
* Tunnel Status vs. BGP Status: For all listed PoPs, the Health Check IP Status and Tunnel status are both shown with a green " Up " icon. This confirms that the underlying IPsec connectivity and the physical path between the SASE cloud and the hub are functioning correctly.
* Identifying the Failure: The BGP Peering State is reported as Active . In BGP terminology, the " Active " state specifically indicates that the router is attempting to initiate a TCP connection with its peer but has not yet received a response. A fully functional and successful BGP connection must reach the Established state.
* Root Cause Determination: Since the tunnel is up (eliminating Gateway or Authentication Method issues as the primary suspects) but the BGP state remains stuck in " Active, " the most likely cause is a mismatch or misconfiguration in the BGP Peer IP or BGP neighbor settings. This prevents the exchange of routing information necessary for users to access private applications.
To resolve the connectivity problem, the administrator must ensure that the BGP neighbor IPs configured on the FortiGate hub match those assigned by the FortiSASE orchestration and that firewall policies on the hub allow BGP traffic (TCP port 179) across the tunnel.
質問 # 74
Refer to the exhibits.
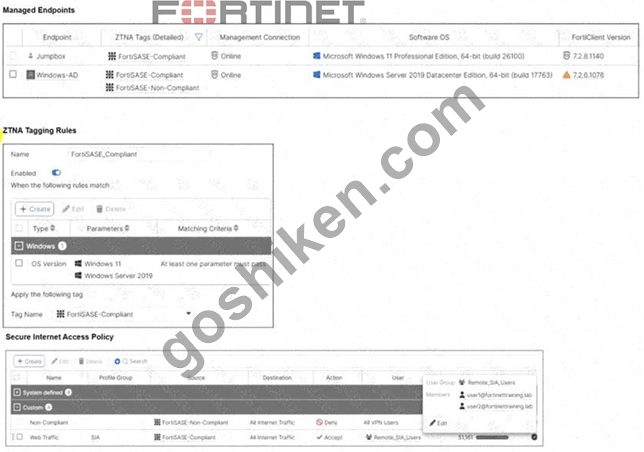
Jumpbox and Windows-AD are endpoints from the same remote location. Jumpbox can access the internet through FortiSASE, while Windows-AD can no longer access the internet. Based on the information in the exhibits, which reason explains the outage on Windows-AD? (Choose one answer)
- A. The FortiClient version installed on Windows-AD does not match the expected version on FortiSASE.
- B. The device security posture for Windows-AD has changed.
- C. Windows-AD is excluded from FortiSASE management.
- D. The remote VPN user on Windows-AD no longer matches any VPN policy.
正解:B
解説:
In FortiSASE, Zero Trust Network Access (ZTNA) tags-also known as security posture tags-are used to dynamically grant or deny access based on the real-time security state of an endpoint. This mechanism ensures that only devices meeting specific compliance requirements can access protected resources or the internet.
* Endpoint Analysis: The Managed Endpoints exhibit shows that while Jumpbox only has the FortiSASE-Compliant tag, the Windows-AD endpoint has been assigned both FortiSASE-Compliant and FortiSASE-Non-Compliant tags. This indicates that a security posture check on the Windows-AD device has failed, triggering a rule that applies the non-compliant tag.
* Policy Evaluation: The Secure Internet Access Policy table shows two custom policies. The first policy, named Non-compliant , uses the FortiSASE-Non-Compliant tag as its source and has the action set to Deny . The second policy, Web Traffic , allows access for FortiSASE-Compliant users.
* Root Cause of Outage: Because FortiSASE (powered by FortiOS) processes security policies in a top- down sequence, the " Non-compliant " policy is evaluated first. Since Windows-AD matches the source criteria for this " Deny " policy, its traffic is blocked before it can reach the " Accept " policy.
Although the exhibit shows a warning icon for the FortiClient version on Windows-AD, the direct cause of the internet outage is the explicit Deny policy triggered by the change in the device ' s security posture (the application of the Non-Compliant tag).
質問 # 75
Refer to the exhibits.
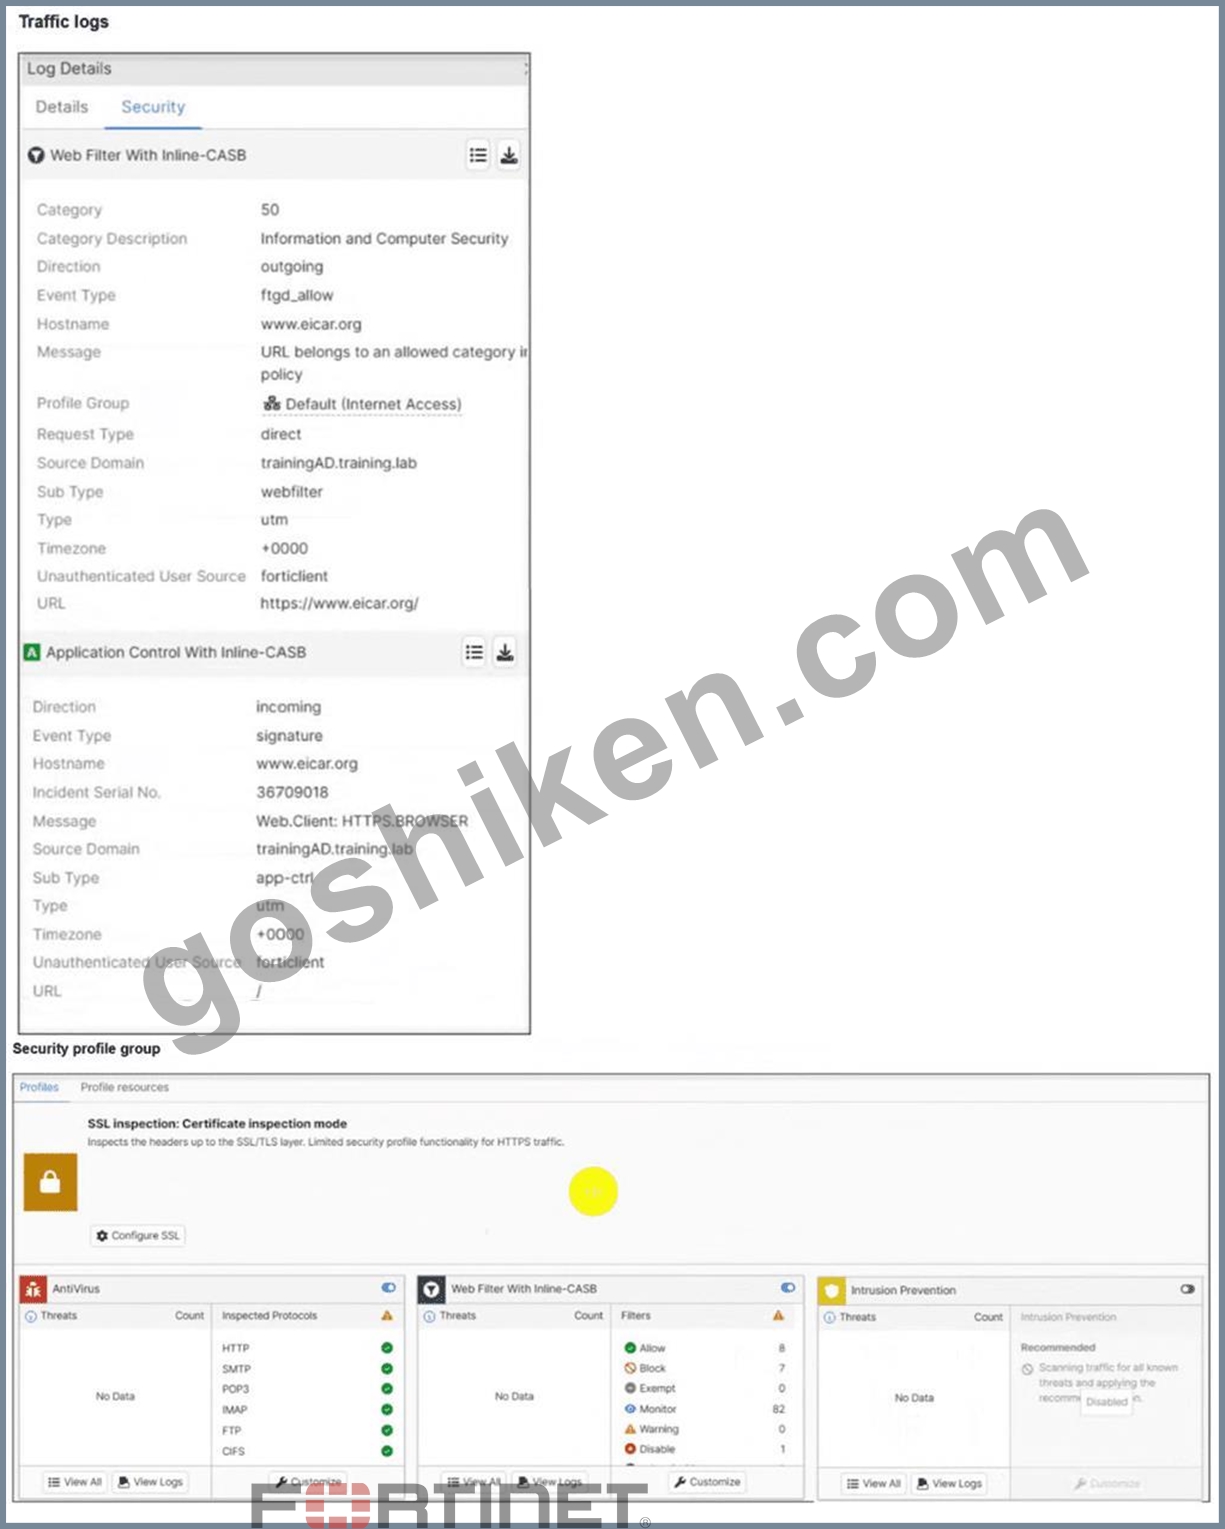
A FortiSASE administrator has configured an antivirus profile in the security profile group and applied it to the internet access policy. Remote users are still able to download the eicar.com-zip file from https://eicar.org.
Which configuration on FortiSASE is allowing users to perform the download? (Choose one answer)
- A. Deep inspection is not enabled.
- B. Web filter is allowing the URL.
- C. Intrusion prevention is disabled.
- D. Application control is exempting all the browser traffic.
正解:A
解説:
The core of the issue shown in the exhibits is the lack of visibility into encrypted traffic.
* HTTPS Encryption: The eicar.org website uses the HTTPS protocol for its downloads. This means the data payload, including the test malware file, is encrypted as it traverses the network.
* SSL Inspection Modes: As seen in the Security profile group exhibit (image_5705fc.jpg), the SSL inspection mode is explicitly set to Certificate inspection mode.
* Visibility Gap: Certificate inspection only analyzes the initial SSL handshake, such as the server certificate and SNI (Server Name Indication). It does not decrypt the traffic payload. Consequently, the antivirus engine in FortiSASE cannot "see" or scan the eicar.com-zip file hidden within the encrypted session.
* Resolution Requirement: To detect and block malicious files over HTTPS, SSL Deep Inspection must be enabled. Deep inspection allows FortiSASE to act as a proxy, decrypting the traffic for full content scanning by the antivirus and IPS engines before re-encrypting it for the endpoint.
* Log Analysis: While the web filtering logs (image_5704e5.jpg) show the traffic is "Allowed" because the URL is not blocked by a web filter category, this is only the first step of inspection. The antivirus engine is present but ineffective because it is blind to the encrypted content due to the lack of deep inspection.
質問 # 76
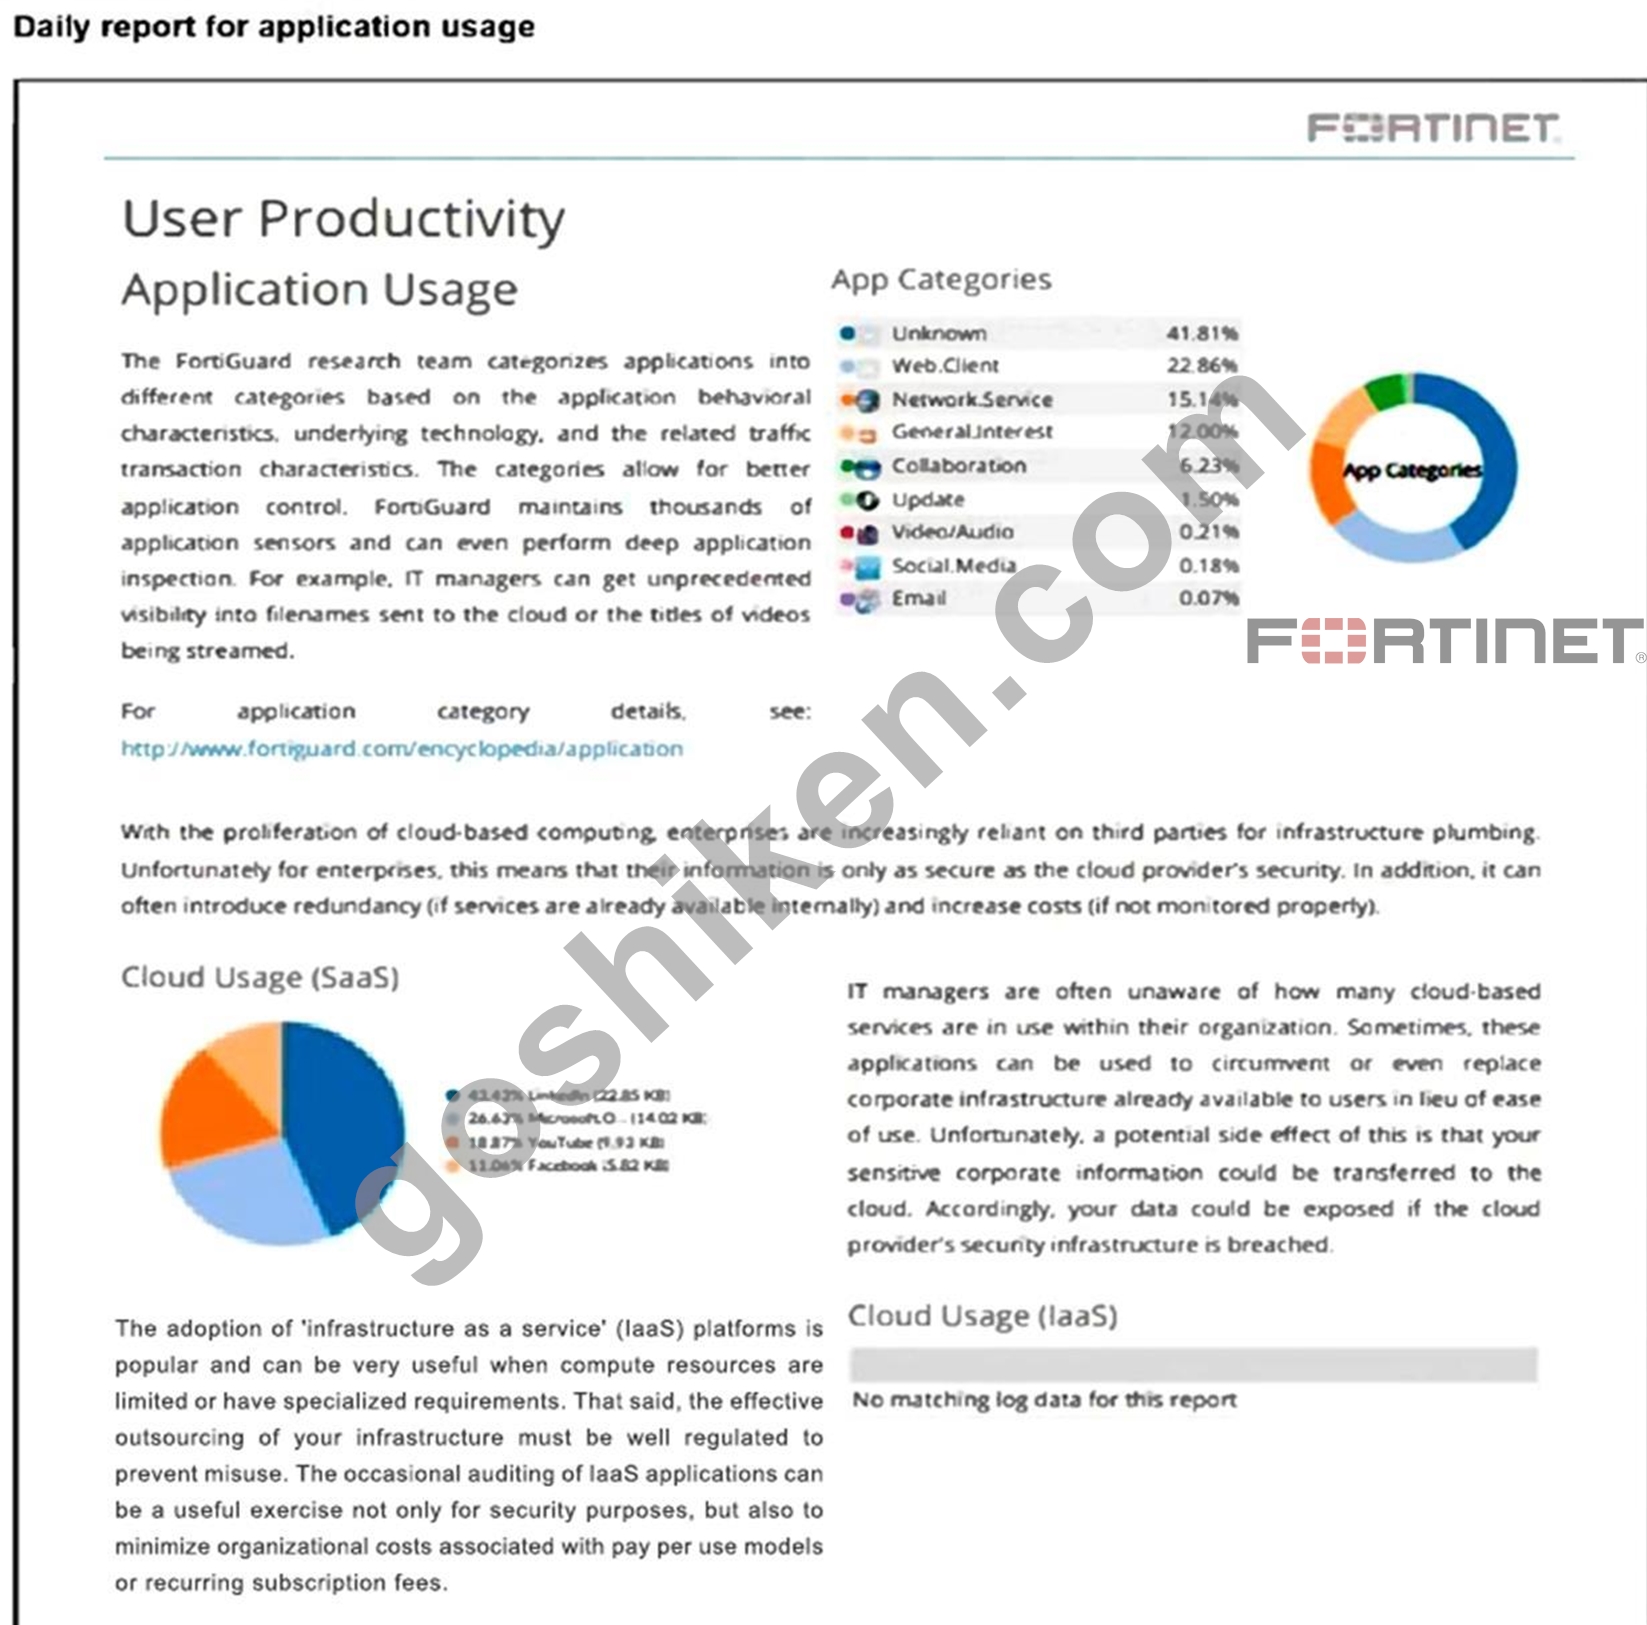
Refer to the exhibit. The daily report for application usage for internet traffic shows an unusually high number of unknown applications by category.
What are two possible explanations for this? (Choose two.)
- A. Deep inspection is not being used to scan traffic.
- B. The inline-CASB application control profile does not have application categories set to Monitor.
- C. Certificate inspection is not being used to scan application traffic.
- D. The private access policy must be to set to log Security Events.
正解:A、C
解説:
A high percentage of unknown applications often indicates that encrypted traffic is not being properly inspected. Without certificate inspection or deep inspection, FortiSASE cannot decrypt and analyze HTTPS traffic to identify applications, resulting in them being classified as
"unknown."
質問 # 77
Which two deployment methods are used to connect a FortiExtender as a FortiSASE LAN extension?
(Choose two.)
- A. Enable Control and Provisioning Wireless Access Points (CAPWAP) access on the FortiSASE portal.
- B. Configure an IPsec tunnel on FortiSASE to connect to FortiExtender.
- C. Enter the FortiSASE domain name in the FortiExtender GUI as a static discovery server
- D. Connect FortiExtender to FortiSASE using FortiZTP
正解:C、D
解説:
There are two deployment methods used to connect a FortiExtender as a FortiSASE LAN extension:
* Connect FortiExtender to FortiSASE using FortiZTP:
* FortiZero Touch Provisioning (FortiZTP) simplifies the deployment process by allowing FortiExtender to automatically connect and configure itself with FortiSASE.
* This method requires minimal manual configuration, making it efficient for large-scale deployments.
* Enter the FortiSASE domain name in the FortiExtender GUI as a static discovery server:
* Manually configuring the FortiSASE domain name in the FortiExtender GUI allows the extender to discover and connect to the FortiSASE infrastructure.
* This static discovery method ensures that FortiExtender can establish a connection with FortiSASE using the provided domain name.
References:
FortiOS 7.6 Administration Guide: Details on FortiExtender deployment methods and configurations.
FortiSASE 23.2 Documentation: Explains how to connect and configure FortiExtender with FortiSASE using FortiZTP and static discovery.
質問 # 78
......
GoShikenが提供したFortinetのNSE7_SSE_AD-25トレーニング資料を持っていたら、美しい未来を手に入れるということになります。GoShikenが提供したFortinetのNSE7_SSE_AD-25トレーニング資料はあなたの成功への礎になれることだけでなく、あなたがIT業種でもっと有効な能力を発揮することも助けられます。このトレーニングはカバー率が高いですから、あなたの知識を豊富させる以外、操作レベルを高められます。もし今あなたがFortinetのNSE7_SSE_AD-25「Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator」試験にどうやって合格することに困っているのなら、心配しないでください。GoShikenが提供したFortinetのNSE7_SSE_AD-25トレーニング資料はあなたの問題を解決することができますから。
NSE7_SSE_AD-25関連資料: https://www.goshiken.com/Fortinet/NSE7_SSE_AD-25-mondaishu.html
- NSE7_SSE_AD-25試験内容 🏧 NSE7_SSE_AD-25復習対策 💛 NSE7_SSE_AD-25英語版 🎦 ⮆ NSE7_SSE_AD-25 ⮄を無料でダウンロード「 www.jpexam.com 」で検索するだけNSE7_SSE_AD-25復習時間
- 人気の有るFortinet NSE7_SSE_AD-25認定試験 - 信頼できるGoShiken - 認定試験のリーダー 🧰 ➡ www.goshiken.com ️⬅️で「 NSE7_SSE_AD-25 」を検索して、無料で簡単にダウンロードできますNSE7_SSE_AD-25必殺問題集
- NSE7_SSE_AD-25学習教材 ⌛ NSE7_SSE_AD-25学習教材 🕉 NSE7_SSE_AD-25学習教材 🗺 ➤ NSE7_SSE_AD-25 ⮘の試験問題は➤ www.goshiken.com ⮘で無料配信中NSE7_SSE_AD-25復習対策
- NSE7_SSE_AD-25英語版 🔋 NSE7_SSE_AD-25受験記 🧃 NSE7_SSE_AD-25復習対策 🚞 ウェブサイト☀ www.goshiken.com ️☀️を開き、⮆ NSE7_SSE_AD-25 ⮄を検索して無料でダウンロードしてくださいNSE7_SSE_AD-25試験内容
- 試験の準備方法-実際的なNSE7_SSE_AD-25認定試験試験-一番優秀なNSE7_SSE_AD-25関連資料 🔵 今すぐ《 www.mogiexam.com 》を開き、▛ NSE7_SSE_AD-25 ▟を検索して無料でダウンロードしてくださいNSE7_SSE_AD-25復習時間
- NSE7_SSE_AD-25試験過去問 🛑 NSE7_SSE_AD-25必殺問題集 🍩 NSE7_SSE_AD-25全真問題集 🥌 時間限定無料で使える{ NSE7_SSE_AD-25 }の試験問題は▛ www.goshiken.com ▟サイトで検索NSE7_SSE_AD-25学習教材
- NSE7_SSE_AD-25難易度 ➿ NSE7_SSE_AD-25日本語版受験参考書 🐨 NSE7_SSE_AD-25難易度 ▛ ▛ NSE7_SSE_AD-25 ▟を無料でダウンロード「 www.xhs1991.com 」ウェブサイトを入力するだけNSE7_SSE_AD-25模擬問題
- NSE7_SSE_AD-25試験の準備方法 | 検証するNSE7_SSE_AD-25認定試験試験 | 有難いFortinet NSE 7 - FortiSASE 25 Enterprise Administrator関連資料 🌒 サイト➡ www.goshiken.com ️⬅️で【 NSE7_SSE_AD-25 】問題集をダウンロードNSE7_SSE_AD-25問題例
- NSE7_SSE_AD-25更新される学習資料、有効なNSE7_SSE_AD-25pdf問題集、Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator勉強資料 ⚖ 時間限定無料で使える“ NSE7_SSE_AD-25 ”の試験問題は⏩ www.shikenpass.com ⏪サイトで検索NSE7_SSE_AD-25全真問題集
- NSE7_SSE_AD-25日本語独学書籍 ⏫ NSE7_SSE_AD-25復習時間 📝 NSE7_SSE_AD-25学習教材 🛴 今すぐ⏩ www.goshiken.com ⏪を開き、⏩ NSE7_SSE_AD-25 ⏪を検索して無料でダウンロードしてくださいNSE7_SSE_AD-25必殺問題集
- NSE7_SSE_AD-25日本語独学書籍 ‼ NSE7_SSE_AD-25日本語版と英語版 🔹 NSE7_SSE_AD-25試験内容 🏣 ウェブサイト⏩ www.passtest.jp ⏪から➥ NSE7_SSE_AD-25 🡄を開いて検索し、無料でダウンロードしてくださいNSE7_SSE_AD-25模擬問題
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.blackhatprotools.info, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, Disposable vapes
ちなみに、GoShiken NSE7_SSE_AD-25の一部をクラウドストレージからダウンロードできます:https://drive.google.com/open?id=15Xxb2V_wSb3NasrNV33gkVrvf4hQtr4a


 icons at the top
right corner of the subsection.