KCNA受験トレーリング, KCNA関連日本語版問題集, KCNAテスト難易度, KCNA試験問題, KCNA資格勉強
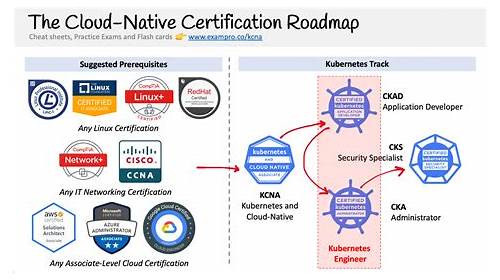
P.S.GoShikenがGoogle Driveで共有している無料の2026 Linux Foundation KCNAダンプ:https://drive.google.com/open?id=1Sbb0bRMxXgTq8wso_vJNV1KmeqDV0lHQ
KCNA試験準備は専門家によって作成され、お客様がKCNA試験に合格し、短時間で証明書を取得するのに非常に役立ちます。購入前にKCNAガイドブレインダンプの品質を知りたい場合は、KCNA試験問題のデモを無料でダウンロードできます。 KCNAトレーニングガイドが証明書の取得に役立つことを確認できます。私たちを信じて、KCNA試験トレントを学ぼうとすると、予期しない結果が得られます。
KubernetesとCloud Native Associate(KCNA)認定試験は、オープンソーステクノロジーを促進およびサポートすることを目的とした非営利組織であるLinux Foundationによって提供されています。この認定試験は、Kubernetesやクラウドネイティブテクノロジーの操作に関心のある個人の知識とスキルをテストするように設計されています。この試験では、コンテナ化、Kubernetesアーキテクチャ、展開、管理など、さまざまなトピックをカバーしています。
Linux Foundation KCNA認定試験は、コンテナ化、Kubernetesアーキテクチャ、展開とスケーリング、トラブルシューティング、セキュリティなど、Kubernetesとクラウドネイティブ技術に関連する幅広いトピックをカバーしています。この試験は、90分以内に完了しなければならない50個の多肢選択問題から構成されています。試験に合格した候補者は、LinkedInプロフィールや他のプロフェッショナルネットワーキングサイトに表示できるデジタルバッジを受け取り、Kubernetesとクラウドネイティブ技術における専門知識を証明できます。この認定資格は、クラウドネイティブコンピューティング分野でキャリアの展望を拡大するための優れた方法です。
>> Linux Foundation KCNA受験トレーリング <<
KCNA関連日本語版問題集、KCNAテスト難易度
Linux FoundationのKCNA試験にもっと首尾よく合格したいのですか。そうしたら速くGoShikenを選びましょう。GoShikenは様々なIT認証試験を受ける人々に正確な試験資料を提供するサイトです。GoShikenはIT職員としてのあなたに昇進するチャンスを与えられます。GoShiken が提供したLinux FoundationのKCNA試験に関する一部の無料の問題と解答を利用してみることができます。そうすると、我々の信頼性をテストできます。
Linux FoundationのKCNA(Kubernetes and Cloud Native Associate)認定試験は、Kubernetesとクラウドネイティブ技術に関する知識とスキルを検証するグローバルに認められた認定プログラムです。Kubernetesは、コンテナ化されたアプリケーションの展開、スケーリング、管理を自動化するオープンソースのコンテナオーケストレーションシステムです。一方、クラウドネイティブ技術は、クラウドネイティブ環境でのアプリケーションの開発と展開を可能にするツールとプラクティスのセットを指します。
Linux Foundation Kubernetes and Cloud Native Associate 認定 KCNA 試験問題 (Q44-Q49):
質問 # 44
Which of the following are tasks performed by a container orchestration tool?
- A. Schedule, scale, and manage the health of containers.
- B. Store images, scale, and manage the health of containers.
- C. Debug applications, and manage the health of containers.
- D. Create images, scale, and manage the health of containers.
正解:A
質問 # 45
What is the role of the ingressClassName field in a Kubernetes Ingress resource?
- A. It defines the type of protocol (HTTP or HTTPS) that the Ingress Controller should process.
- B. It specifies the backend Service used by the Ingress Controller to route external requests.
- C. It determines how routing rules are prioritized when multiple Ingress objects are applied.
- D. It indicates which Ingress Controller should implement the rules defined in the Ingress resource.
正解:D
解説:
The ingressClassName field in a Kubernetes Ingress resource is used to explicitly specify which Ingress Controller is responsible for processing and enforcing the rules defined in that Ingress. This makes option D the correct answer.
In Kubernetes clusters, it is common to have multiple Ingress Controllers running at the same time. For example, a cluster might run an NGINX Ingress Controller, a cloud-provider-specific controller, and an internal-only controller simultaneously. Without a clear mechanism to select which controller should handle a given Ingress resource, multiple controllers could attempt to process the same rules, leading to conflicts or undefined behavior.
The ingressClassName field solves this problem by referencing an IngressClass object. The IngressClass defines the controller implementation (via the controller field), and the Ingress resource uses ingressClassName to declare which class-and therefore which controller-should act on it. This creates a clean and explicit binding between an Ingress and its controller.
Option A is incorrect because protocol handling (HTTP vs HTTPS) is defined through TLS configuration and service ports, not by ingressClassName. Option B is incorrect because backend Services are defined in the rules and backend sections of the Ingress specification. Option C is incorrect because routing priority is determined by path matching rules and controller-specific logic, not by ingressClassName.
Historically, annotations were used to select Ingress Controllers, but ingressClassName is now the recommended and standardized approach. It improves clarity, portability, and compatibility across different Kubernetes distributions and controllers.
In summary, the primary purpose of ingressClassName is to indicate which Ingress Controller should implement the routing rules for a given Ingress resource, making Option D the correct and verified answer.
質問 # 46
What feature must a CNI support to control specific traffic flows for workloads running in Kubernetes?
- A. IP Address Management
- B. Network Policies
- C. Pod Security Policy
- D. Border Gateway Protocol
正解:B
解説:
To control which workloads can communicate with which other workloads in Kubernetes, you use NetworkPolicy resources-but enforcement depends on the cluster's networking implementation. Therefore, for traffic-flow control, the CNI/plugin must support Network Policies, making D correct.
Kubernetes defines the NetworkPolicy API as a declarative way to specify allowed ingress and egress traffic based on selectors (Pod labels, namespaces, IP blocks) and ports/protocols. However, Kubernetes itself does not enforce NetworkPolicy rules; enforcement is provided by the network plugin (or associated dataplane components). If your CNI does not implement NetworkPolicy, the objects may exist in the API but have no effect-Pods will communicate freely by default.
Option B (IP Address Management) is often part of CNI responsibilities, but IPAM is about assigning addresses, not enforcing L3/L4 security policy. Option A (BGP) is used by some CNIs to advertise routes (for example, in certain Calico deployments), but BGP is not the general requirement for policy enforcement.
Option C (Pod Security Policy) is a deprecated/removed Kubernetes admission feature related to Pod security settings, not network flow control.
From a Kubernetes security standpoint, NetworkPolicies are a key tool for implementing least privilege at the network layer-limiting lateral movement, reducing blast radius, and segmenting environments. But they only work when the chosen CNI supports them. Thus, the correct answer is D: Network Policies.
=========
質問 # 47
You need to deploy a pod that requires access to a specific GPU device. How can you ensure that
the pod is scheduled on a node with the required GPU?
- A. Use the 'tolerations' field to tolerate the 'GPU' taint.
- B. Use the 'nodeSelector' field to target nodes with the 'gpu' label.
- C. Use the 'podAffinity' field to group pods with GPU requirements together.
- D. Use the 'affinity' field to prefer nodes with the 'GPU* label.
- E. Use the 'resources' field to specify the GPU requirements in the container's definition.
正解:E
解説:
You can use both the •nodeselector• and •resources' fields to achieve this: 'nodeselector•: Targets nodes with a label indicating the presence of GPUs (e.g., •gpu: true). •resources': Specify the GPU resource requirements within the container's definition. This provides a more precise way to request specific GPUs and their capabilities. While •tolerations' and 'affinity' can be used for other scheduling needs, they are not directly designed for GPU resource allocation.
質問 # 48
What edge and service proxy tool is designed to be integrated with cloud native applications?
- A. Envoy
- B. CoreDNS
- C. CNI
- D. gRPC
正解:A
解説:
The correct answer is D: Envoy. Envoy is a high-performance edge and service proxy designed for cloud-native environments. It is commonly used as the data plane in service meshes and modern API gateways because it provides consistent traffic management, observability, and security features across microservices without requiring every application to implement those capabilities directly.
Envoy operates at Layer 7 (application-aware) and supports protocols like HTTP/1.1, HTTP/2, gRPC, and more. It can handle routing, load balancing, retries, timeouts, circuit breaking, rate limiting, TLS termination, and mutual TLS (mTLS). Envoy also emits rich telemetry (metrics, access logs, tracing) that integrates well with cloud-native observability stacks.
Why the other options are incorrect:
CoreDNS (A) provides DNS-based service discovery within Kubernetes; it is not an edge/service proxy.
CNI (B) is a specification and plugin ecosystem for container networking (Pod networking), not a proxy.
gRPC (C) is an RPC protocol/framework used by applications; it's not a proxy tool. (Envoy can proxy gRPC traffic, but gRPC itself isn't the proxy.) In Kubernetes architectures, Envoy often appears in two places: (1) at the edge as part of an ingress/gateway layer, and (2) sidecar proxies alongside Pods in a service mesh (like Istio) to standardize service-to-service communication controls and telemetry. This is why it is described as "designed to be integrated with cloud native applications": it's purpose-built for dynamic service discovery, resilient routing, and operational visibility in distributed systems.
So the verified correct choice is D (Envoy).
質問 # 49
......
KCNA関連日本語版問題集: https://www.goshiken.com/Linux-Foundation/KCNA-mondaishu.html
- KCNA受験準備 🚞 KCNA関連資格知識 🎒 KCNA問題と解答 👤 ▷ www.mogiexam.com ◁の無料ダウンロード⇛ KCNA ⇚ページが開きますKCNA関連資格知識
- KCNA試験の準備方法|最高のKCNA受験トレーリング試験|一番優秀なKubernetes and Cloud Native Associate関連日本語版問題集 🕌 【 www.goshiken.com 】サイトにて最新⏩ KCNA ⏪問題集をダウンロードKCNA関連資格知識
- KCNA全真問題集 😂 KCNAテスト問題集 🎱 KCNA関連試験 😉 サイト➥ www.shikenpass.com 🡄で▛ KCNA ▟問題集をダウンロードKCNA資格試験
- KCNA試験概要 🗽 KCNA資格試験 🐄 KCNA問題トレーリング 🚼 ▷ www.goshiken.com ◁を入力して【 KCNA 】を検索し、無料でダウンロードしてくださいKCNA的中関連問題
- 素晴らしいKCNA受験トレーリング | 最初の試行で簡単に勉強して試験に合格する - 正確的なLinux Foundation Kubernetes and Cloud Native Associate 🔉 ➽ KCNA 🢪を無料でダウンロード➥ www.shikenpass.com 🡄で検索するだけKCNAテストトレーニング
- 実用的KCNA | 検証するKCNA受験トレーリング試験 | 試験の準備方法Kubernetes and Cloud Native Associate関連日本語版問題集 ⤵ ▶ www.goshiken.com ◀にて限定無料の➽ KCNA 🢪問題集をダウンロードせよKCNA関連日本語版問題集
- KCNA的中関連問題 🍺 KCNA受験料過去問 🎻 KCNA試験関連情報 🤔 [ www.mogiexam.com ]は、➡ KCNA ️⬅️を無料でダウンロードするのに最適なサイトですKCNA問題と解答
- 真実的-更新するKCNA受験トレーリング試験-試験の準備方法KCNA関連日本語版問題集 ⭐ 検索するだけで✔ www.goshiken.com ️✔️から➤ KCNA ⮘を無料でダウンロードKCNA日本語対策
- 効率的なKCNA受験トレーリング - 資格試験におけるリーダーオファー - 無料PDF Linux Foundation Kubernetes and Cloud Native Associate 🅾 時間限定無料で使える【 KCNA 】の試験問題は“ www.passtest.jp ”サイトで検索KCNA資格試験
- KCNA資格試験 🦇 KCNA専門知識内容 ⏩ KCNA試験概要 🦞 URL 「 www.goshiken.com 」をコピーして開き、➽ KCNA 🢪を検索して無料でダウンロードしてくださいKCNA問題と解答
- KCNA関連試験 🎇 KCNA専門知識内容 🅰 KCNA問題と解答 🤰 今すぐ⇛ www.mogiexam.com ⇚で《 KCNA 》を検索し、無料でダウンロードしてくださいKCNA日本語参考
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes
無料でクラウドストレージから最新のGoShiken KCNA PDFダンプをダウンロードする:https://drive.google.com/open?id=1Sbb0bRMxXgTq8wso_vJNV1KmeqDV0lHQ


 icons at the top
right corner of the subsection.