NSE5_FSW_AD-7.6過去問無料, NSE5_FSW_AD-7.6復習対策書, NSE5_FSW_AD-7.6ブロンズ教材, NSE5_FSW_AD-7.6復習資料, NSE5_FSW_AD-7.6必殺問題集

P.S. JPNTestがGoogle Driveで共有している無料かつ新しいNSE5_FSW_AD-7.6ダンプ:https://drive.google.com/open?id=1Fwqeo4zu2avi0LxOQd7lQJGdC0KwccX4
一般的な教育トレーニングソフトウェアとは異なり、NSE5_FSW_AD-7.6試験の質問では、学生がシミュレーション問題を提供するプラットフォームで20〜30時間練習するだけでよいため、NSE5_FSW_AD-7.6試験に合格する自信があります。一部の労働者にとって、それはどれほど効率的か。時は金なりです。今日では効率にますます注意を払っています。適切な場所で時間を使い、低い時間で見返りに高いスコアを得る必要があります。NSE5_FSW_AD-7.6最新の試験トレントはこれを行うのに非常に良いです。
Fortinet NSE5_FSW_AD-7.6 Exam Syllabus Topics:
| Section |
Objectives |
| Topic 1: VLANs and Segmentation |
- VLAN creation and tagging
- Inter-VLAN routing considerations
|
| Topic 2: Security Integration with FortiGate |
- Security policies for switched networks
- Device identity and access control
|
| Topic 3: FortiSwitch Fundamentals |
- FortiSwitch operating modes
- Switch architecture and hardware overview
|
| Topic 4: Redundancy and High Availability |
- Redundant switch design
- Link aggregation (LACP)
|
| Topic 5: Switch Configuration and Management |
- Initial setup and provisioning
- Switch ports and profiles
|
| Topic 6: Spanning Tree Protocol |
- Loop prevention mechanisms
- STP/RSTP configuration
|
| Topic 7: Monitoring and Troubleshooting |
- Common switching issues
- Diagnostics and logging
|
| Topic 8: FortiLink Integration |
- FortiLink topology and design
- FortiGate-managed switching
|
>> Fortinet NSE5_FSW_AD-7.6過去問無料 <<
NSE5_FSW_AD-7.6試験の準備方法|最高のNSE5_FSW_AD-7.6過去問無料試験|実用的なFortinet NSE 5 - FortiSwitch 7.6 Administrator復習対策書
Fortinetは、短時間でNSE5_FSW_AD-7.6認定を取得するために最善を尽くす必要があります。 認定資格を取得することが決まっている場合、NSE5_FSW_AD-7.6質問トレントは喜んであなたに手を差し伸べます。 弊社のNSE5_FSW_AD-7.6学習教材は、認定を取得するための最適な学習ツールになるためです。 ここで、NSE5_FSW_AD-7.6試験問題を詳細に紹介します。紹介を注意深くお読みください。多くのメリットを得ることができます。 NSE5_FSW_AD-7.6試験の資料に興味がある場合は、今すぐ購入できます。
Fortinet NSE 5 - FortiSwitch 7.6 Administrator 認定 NSE5_FSW_AD-7.6 試験問題 (Q41-Q46):
質問 # 41
What feature can network administrators use to segment network operations and the administration of managed FortiSwitch devices on FortiGate?
- A. FortiGate clustering protocol
- B. Multi-chassis link aggregation trunk
- C. FortiGate multi-tenancy
- D. FortiLink split interface
正解:C
解説:
FortiGate's multi-tenancy feature, specifically Virtual Domains (VDOMs), is the most appropriate tool for segmenting network operations and the administration of managed FortiSwitch devices on FortiGate. Here's why:
* VDOMs as Virtual Firewalls:VDOMs function as independent virtual firewalls within a single FortiGate device. Each VDOM can have its own:
* Security policies
* Interfaces (Including FortiLink interfaces for FortiSwitch management)
* Routing table
* Administrative access
* Segmenting Network Operations:By assigning different FortiSwitch devices (or groups of ports) to separate VDOMs, you effectively partition your network. Network administrators can manage specific FortiSwitches through their assigned VDOMs, maintaining operational isolation.
* Enhanced Administration:VDOMs offer granular administrative control. Different administrators can be assigned to specific VDOMs, limiting their management scope and reducing the risk of accidental configuration changes.
Why Other Options Are Less Suitable:
* B. Multi-chassis link aggregation trunk:This focuses on link redundancy and bandwidth aggregation, not network segmentation.
* C. FortiGate clustering protocol:This is aimed at high availability and scalability of the firewall functions themselves, not the management of switches.
* D. FortiLink split interface:This allows dividing a FortiLink interface on the FortiGate for managing multiple FortiSwitches, but it doesn't provide the true segmentation and administrative isolation that VDOMs offer.
References:
Fortinet Document Library - VDOMs:[invalid URL removed]
Fortinet Document Library - FortiSwitch Multi-tenancy (using VDOMS):https://docs.fortinet.com/document
/fortiswitch/7.4.2/fortilink-guide/801172/multitenancy-and-vdoms
質問 # 42
(Full question statement start from here)
Refer to the exhibit.
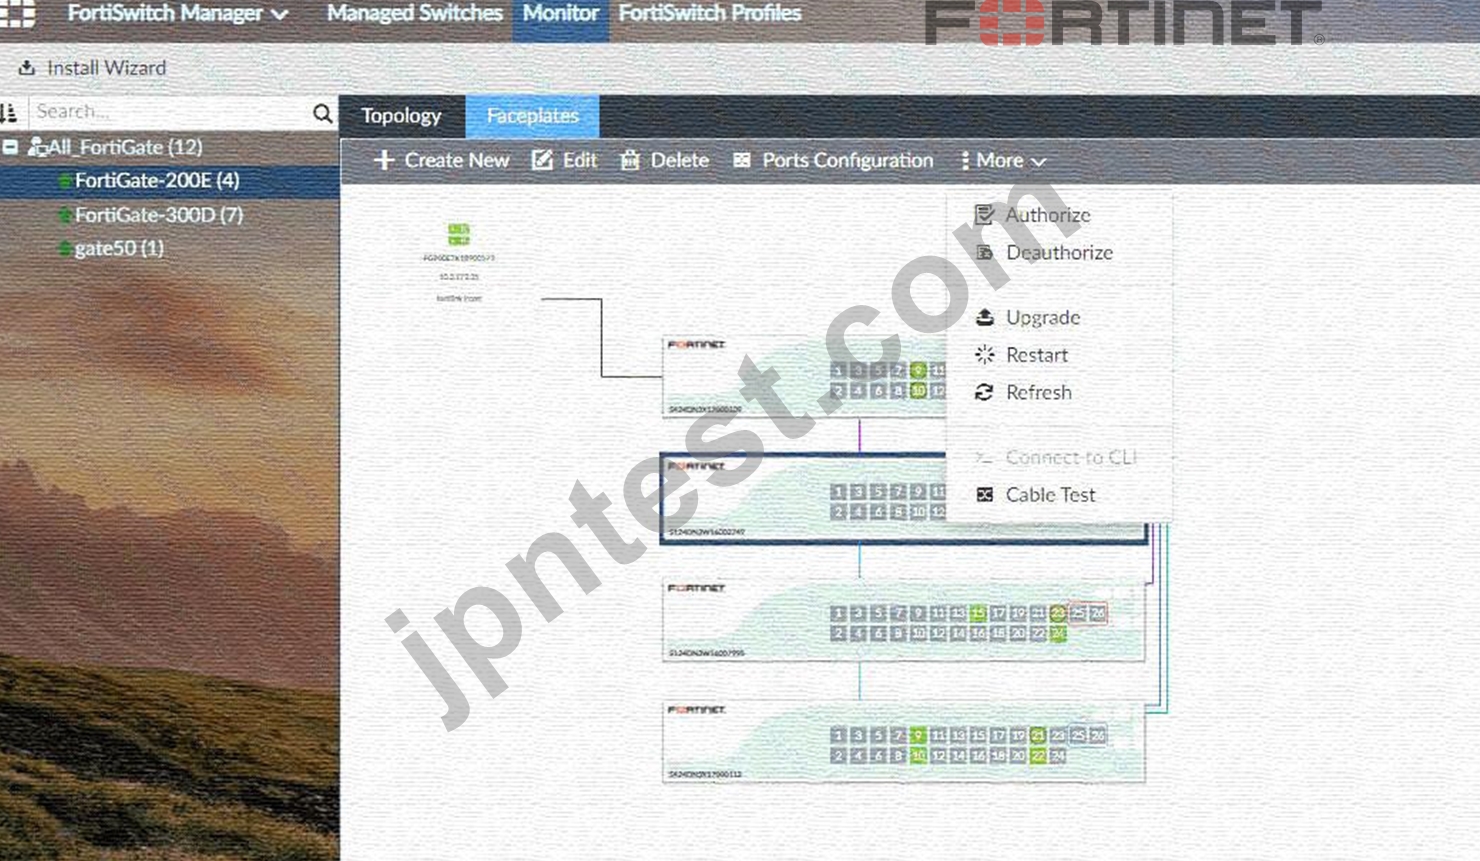
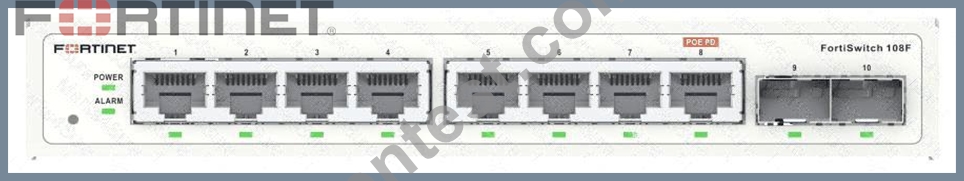
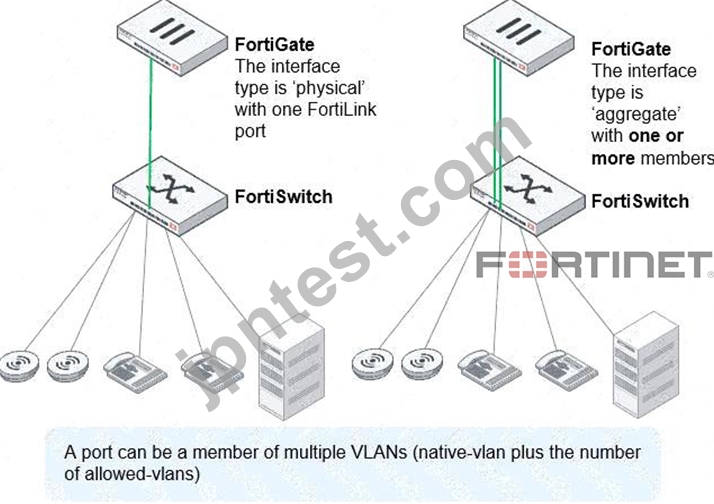
Which information does FortiGate use to generate the port details in the FortiSwitch Faceplates view?
(Choose one answer)
- A. The Cisco Discovery Protocol (CDP) advertisements from FortiSwitch
- B. The LLDP advertisements received from the FortiSwitch
- C. The FortiLink discovery frames sent by FortiSwitch
- D. The FortiSwitch model
正解:B
解説:
In a FortiLink-managed switching architecture, the FortiGate firewall acts as the centralized controller for downstream FortiSwitch devices. TheFortiSwitch Faceplatesview in the FortiGate GUI provides a physical- style representation of switch ports, including port numbers, operational status, link state, speed, duplex, and connected neighbor information. According to FortiOS 7.6 and FortiSwitchOS 7.6 documentation fromFortinet, this port-level intelligence is derived fromLink Layer Discovery Protocol (LLDP) advertisements received from the FortiSwitch.
LLDP is an IEEE 802.1AB standard protocol used for vendor-neutral Layer 2 neighbor discovery.
FortiSwitch periodically sends LLDP frames that include detailed port descriptors such as chassis ID, port ID, port description, system name, system capabilities, and VLAN-related attributes. When FortiGate receives these LLDP advertisements over the FortiLink interface, it correlates the information with the managed FortiSwitch inventory and renders accurate port details in the Faceplates view.
Other options are incorrect for the following reasons. The FortiSwitch model alone is insufficient to populate per-port operational details. Cisco Discovery Protocol (CDP) is a Cisco-proprietary protocol and is not used by FortiGate for Faceplates visualization. FortiLink discovery frames are used to establish and maintain the FortiLink management relationship, but they do not carry the granular per-port metadata required for the Faceplates display.
Therefore, the Faceplates view relies specifically onLLDP advertisements received from the FortiSwitch, making optionCthe correct and fully verified answer based on FortiOS 7.6 and FortiSwitchOS 7.6 behavior.
質問 # 43
(Full question statement start from here)
Refer to the exhibits.
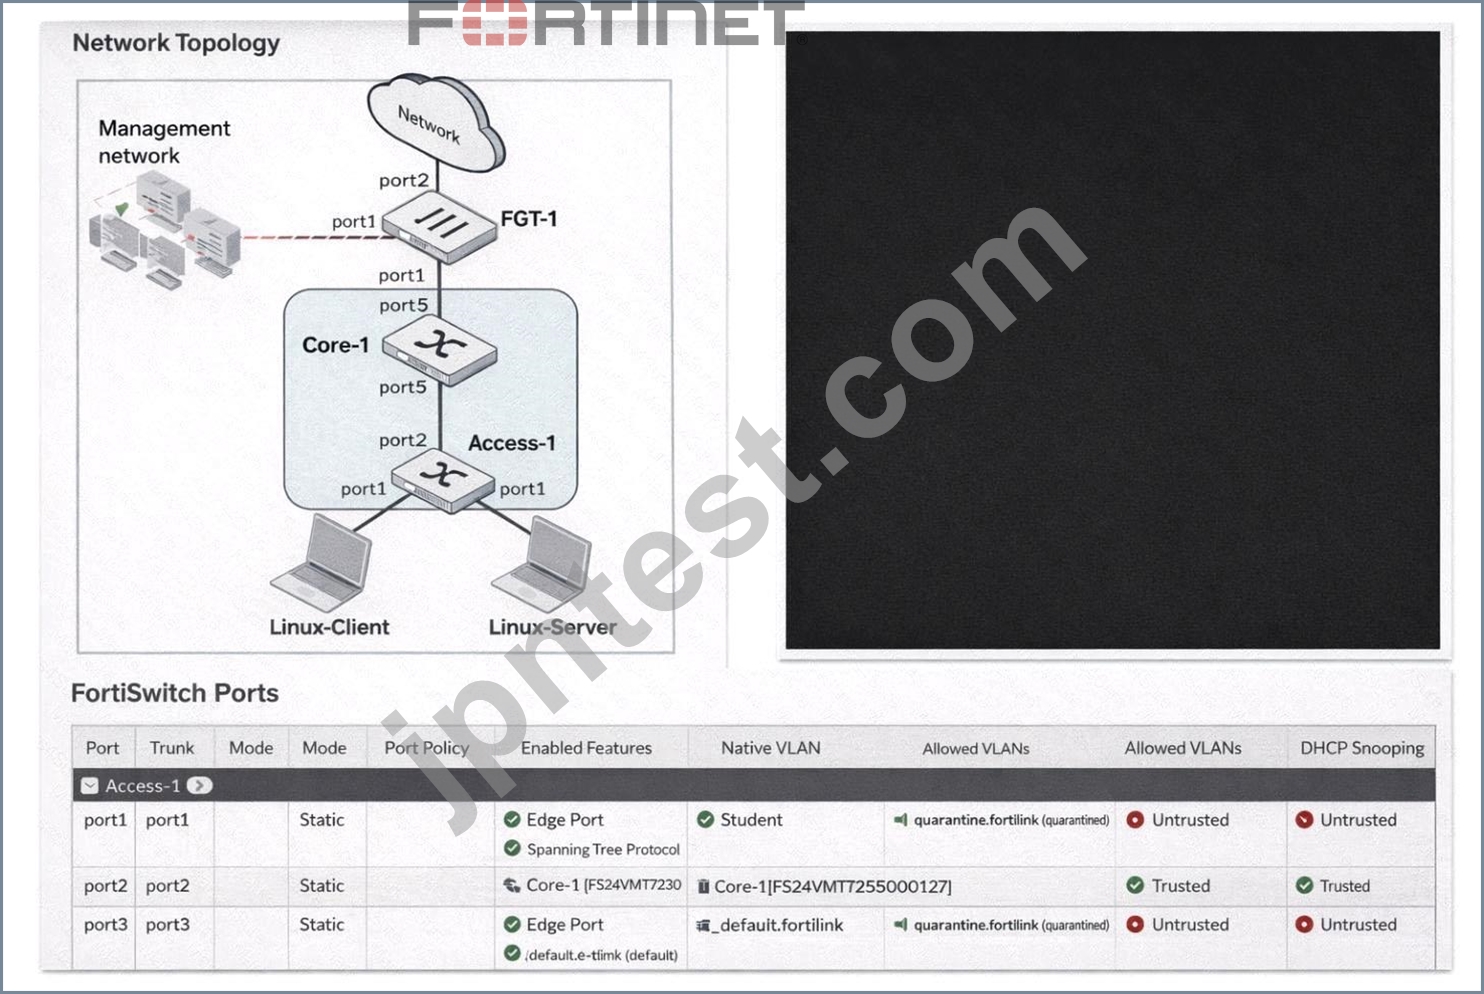
You enable Dynamic Host Configuration Protocol (DHCP) snooping on the VLAN,Student. The Linux- Client VM sends DHCP requests, and tcpdump confirms the broadcasts. However, the Linux-Server VM, acting as a DHCP server, receives no DHCP traffic. What is the most likely cause of this intra-VLAN traffic being blocked? (Choose one answer)
- A. Port1 is configured as an untrusted port.
- B. The Student VLAN must be configured as an allowed VLAN on port1.
- C. The DHCP requests are being sent on the wrong VLAN.
- D. Port4 is not configured as a trusted port.
正解:A
解説:
In FortiSwitchOS 7.6,DHCP snoopingis a Layer 2 security feature that validates DHCP traffic and protects the LAN from rogue DHCP servers. The feature enforces atrust modelon switch ports: ports connected toward legitimate DHCP server infrastructure must be markedtrusted, while edge/access ports facing clients are typicallyuntrusted. When DHCP snooping is enabled on a VLAN (in this case,Student), FortiSwitch inspects DHCP messages and applies filtering rules based on port trust status.
From the exhibit, bothport1(connected to the Linux-Server DHCP server) andport4(connected to the Linux- Client) showDHCP Snooping: Untrusted. In this configuration, the switch treats the DHCP server-facing port as untrusted and, by design, willblock DHCP server-originated messages(such as DHCPOFFER
/DHCPACK) arriving on that interface. This prevents the DHCP handshake from completing and effectively stops DHCP from functioning across that VLAN segment. Operationally, this is commonly observed as "no DHCP traffic" at the server/application layer because the exchange cannot progress normally when the server side is not trusted.
Option C is incorrect because the client-facing port is expected to be untrusted. Options A and D do not align with the exhibit: the ports are already placed in the Student VLAN as native VLAN, so the primary issue is the DHCP snooping trust role.
Therefore, the most likely cause is thatport1 is configured as an untrusted port(it must be trusted for a DHCP server), makingBthe correct answer.
質問 # 44
Refer to the diagnostic output:
What makes the use of the sniffer command on the FortiSwitch CLI unreliable on__port__23?
- A. The types of packets captured is limited.
- B. The switch port might be used as a trunk member
- C. Just the port egress payloads are printed on CLI.
- D. Only untagged VLAN traffic can be captured.
正解:A
解説:
Page 452 of 7.6 study guide, specifically states " Although you can use the sniffer command to capture traffic on switch ports, the types of packets capture by the sniffer are very limited.
The use of the sniffer command on FortiSwitch CLI can be unreliable on port 23 for specific reasons related to the nature of traffic on the port:
D).The switch port might be used as a trunk member.When a switch port is configured as a trunk, it can carry traffic for multiple VLANs. If the sniffer is set up without specifying VLAN tags or a range of VLANs to capture, it may not accurately capture or display all the VLAN traffic due to the volume and variety of VLAN- tagged packets passing through the trunk port. This limitation makes using the sniffer on a trunk port unreliable for capturing specific VLAN traffic unless properly configured to handle tagged traffic.
References:
For guidelines on how to properly use sniffer commands on trunk ports and configure VLAN filtering, consult the FortiSwitch CLI reference available through Fortinet support channels, including theFortinet Knowledge Base.
質問 # 45
You need to deploy routing on a standalone FortiSwitch and want to maximize routing performance. Which type of routing is best for this deployment? (Choose one answer)
- A. Hardware-based routing because the routing is performed directly by the kernel
- B. Software-based routing because it is preferred for high-speed backbone networks
- C. Hardware-based routing because it relies on ASIC for faster performance1
- D. Software-based routing because it bypasses the CPU to increase routing speed
正解:C
解説:
According to theFortiSwitchOS 7.6 Administration Guideand theFortiSwitch 7.6.1 Administration Guide- Standalone Mode, FortiSwitch units support two primary methods for processing Layer 3 traffic: software- based routing and hardware-based routing. To maximize performance, the documentation specifies thatHardware-based routing (Option A)is the superior choice for high-speed environments.
The primary technical reason for this performance advantage is the use ofApplication-Specific Integrated Circuits (ASICs). In hardware-based routing, the routing table and forwarding information are programmed directly into the switch ' s specialized hardware silicon. This allows the FortiSwitch to perform packet lookups and forwarding decisions at " wire speed, " which refers to the full throughput capacity of the physical ports.
By offloading these tasks to the ASIC, the switch minimizes latency and prevents the performance bottlenecks associated with general-purpose CPU processing.
In contrast,software-based routing(Options B and D) requires the main system CPU and kernel to process every packet, which is significantly slower and can lead to high CPU utilization during heavy traffic loads.
Option C is factually incorrect because hardware-based routing specifically avoids the kernel ' s software path to increase speed. Therefore, for a deployment focused on maximizing routing performance, especially in a backbone or high-density branch environment, utilizing the ASIC-driven hardware forwarding path is the recommended approach in FortiSwitchOS 7.6.
質問 # 46
......
多くの人は、NSE5_FSW_AD-7.6の有効な学習ガイド教材を購入することを好みます。なぜなら、購入するだけで間違いなくテストに合格できると深く信じているからです。 NSE5_FSW_AD-7.6ガイドの質問を好む理由は、教材の品質が非常に高いためです。長年、私たちは常にNSE5_FSW_AD-7.6学習教材の完成に専念しています。一流の研究チームと一流の販売サービスを強化します。 NSE5_FSW_AD-7.6ガイドの質問とNSE5_FSW_AD-7.6学習教材の更新を担当する専門スタッフの研究と制作を専門とするエキスパートチームを後押しします。
NSE5_FSW_AD-7.6復習対策書: https://jpntest.com/shiken/NSE5_FSW_AD-7.6-mondaishu
- NSE5_FSW_AD-7.6日本語認定対策 🚗 NSE5_FSW_AD-7.6試験資料 ✌ NSE5_FSW_AD-7.6試験資料 🌀 ➥ www.topexam.jp 🡄サイトにて▶ NSE5_FSW_AD-7.6 ◀問題集を無料で使おうNSE5_FSW_AD-7.6試験資料
- ユニークなNSE5_FSW_AD-7.6過去問無料 - 合格スムーズNSE5_FSW_AD-7.6復習対策書 | 認定するNSE5_FSW_AD-7.6ブロンズ教材 Fortinet NSE 5 - FortiSwitch 7.6 Administrator 🖐 Open Webサイト“ www.goshiken.com ”検索⏩ NSE5_FSW_AD-7.6 ⏪無料ダウンロードNSE5_FSW_AD-7.6試験問題集
- 正確的なNSE5_FSW_AD-7.6過去問無料 - 保証するFortinet NSE5_FSW_AD-7.6 信頼できる試験の成功NSE5_FSW_AD-7.6復習対策書 ☕ 最新▶ NSE5_FSW_AD-7.6 ◀問題集ファイルは⏩ www.mogiexam.com ⏪にて検索NSE5_FSW_AD-7.6資格認証攻略
- 試験の準備方法-真実的なNSE5_FSW_AD-7.6過去問無料試験-素晴らしいNSE5_FSW_AD-7.6復習対策書 🍢 今すぐ➠ www.goshiken.com 🠰で➡ NSE5_FSW_AD-7.6 ️⬅️を検索して、無料でダウンロードしてくださいNSE5_FSW_AD-7.6全真問題集
- NSE5_FSW_AD-7.6資格問題集 🍂 NSE5_FSW_AD-7.6関連資料 🏳 NSE5_FSW_AD-7.6トレーニング費用 🚆 { www.mogiexam.com }を開き、( NSE5_FSW_AD-7.6 )を入力して、無料でダウンロードしてくださいNSE5_FSW_AD-7.6復習テキスト
- NSE5_FSW_AD-7.6資格問題集 😅 NSE5_FSW_AD-7.6試験対応 🎦 NSE5_FSW_AD-7.6関連資料 🍨 ⮆ NSE5_FSW_AD-7.6 ⮄を無料でダウンロード➡ www.goshiken.com ️⬅️で検索するだけNSE5_FSW_AD-7.6資格認証攻略
- NSE5_FSW_AD-7.6トレーニング費用 🦟 NSE5_FSW_AD-7.6日本語版テキスト内容 🏏 NSE5_FSW_AD-7.6トレーニング費用 🧮 時間限定無料で使える➽ NSE5_FSW_AD-7.6 🢪の試験問題は《 www.topexam.jp 》サイトで検索NSE5_FSW_AD-7.6試験問題集
- NSE5_FSW_AD-7.6試験問題集 ⚜ NSE5_FSW_AD-7.6復習テキスト 🚴 NSE5_FSW_AD-7.6問題トレーリング 🔥 ☀ www.goshiken.com ️☀️サイトにて最新☀ NSE5_FSW_AD-7.6 ️☀️問題集をダウンロードNSE5_FSW_AD-7.6最新テスト
- 高品質なNSE5_FSW_AD-7.6過去問無料試験-試験の準備方法-効率的なNSE5_FSW_AD-7.6復習対策書 📽 サイト➥ www.passtest.jp 🡄で➠ NSE5_FSW_AD-7.6 🠰問題集をダウンロードNSE5_FSW_AD-7.6必殺問題集
- 実用的NSE5_FSW_AD-7.6過去問無料 - 資格試験のリーダー - 高パスレートNSE5_FSW_AD-7.6復習対策書 👤 最新➽ NSE5_FSW_AD-7.6 🢪問題集ファイルは➥ www.goshiken.com 🡄にて検索NSE5_FSW_AD-7.6最新テスト
- NSE5_FSW_AD-7.6問題トレーリング ✈ NSE5_FSW_AD-7.6日本語版テキスト内容 🍎 NSE5_FSW_AD-7.6技術問題 ⚛ [ www.it-passports.com ]は、⏩ NSE5_FSW_AD-7.6 ⏪を無料でダウンロードするのに最適なサイトですNSE5_FSW_AD-7.6試験問題集
-
www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.blackhatprotools.info, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, backloggd.com, Disposable vapes
2026年JPNTestの最新NSE5_FSW_AD-7.6 PDFダンプおよびNSE5_FSW_AD-7.6試験エンジンの無料共有:https://drive.google.com/open?id=1Fwqeo4zu2avi0LxOQd7lQJGdC0KwccX4


 icons at the top
right corner of the subsection.