200-301測試引擎, 200-301考試證照, 200-301真題材料, 200-301認證考試解析, 200-301考試資料
從Google Drive中免費下載最新的KaoGuTi 200-301 PDF版考試題庫:https://drive.google.com/open?id=11tkFWQYFrNp7vmwrwdjEtR6gBAu0NLPj
即將參加Cisco的200-301認證考試的你沒有信心通過考試嗎?不用害怕,因為KaoGuTi可以提供給你最好的資料。KaoGuTi的200-301考古題是最新最全面的考試資料,一定可以給你通過考試的勇氣與自信。这是经过很多人证明过的事实。
Cisco 200-301 Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| IP Connectivity |
25% |
- Configure and verify single area OSPFv2
- Determine how a router makes a forwarding decision by default
- Configure and verify IPv4 and IPv6 static routing
- Interpret the components of routing table
- Describe the purpose of first hop redundancy protocol
|
| Network Fundamentals |
20% |
- Describe the need for private IPv4 addressing
- Describe switching concepts
- Describe characteristics of network topology architectures
- Configure and verify IPv4 addressing and subnetting
- Describe wireless principles
- Explain the role and function of network components
- Compare TCP to UDP
- Compare physical interface and cabling types
- Identify interface and cable issues (collisions, errors, mismatch)
- Verify IP parameters for Client OS (Windows, Mac OS, Linux)
- Compare IPv6 address types
- Configure and verify IPv6 addressing and prefix
- Explain virtualization fundamentals (virtual machines)
|
| Automation and Programmability |
10% |
- Recognize the capabilities of configuration management mechanisms Puppet, Chef, and Ansible
- Describe controller-based and software defined architectures (overlay, underlay, and fabric)
- Compare traditional networks with controller-based networking
- Compare traditional campus device management with Cisco DNA Center enabled device management
- Explain how automation impacts network management
- Interpret JSON encoded data
- Describe characteristics of REST-based APIs (CRUD, HTTP verbs, and data encoding)
|
| Network Access |
20% |
- Describe the need for and basic operations of Rapid PVST+ Spanning Tree Protocol
- Describe AP and WLC management access connections (Telnet, SSH, HTTP, HTTPS, console, and TACACS+/RADIUS)
- Describe physical infrastructure connections of WLAN components (AP, WLC, access/trunk ports, and LAG)
- Configure and verify Layer 2 discovery protocols (Cisco Discovery Protocol and LLDP)
- Configure and verify VLANs (normal range) spanning multiple switches
- Configure the components of a wireless LAN access for client connectivity using GUI only such as WLAN creation, security settings, QoS profiles, and advanced WLAN settings
- Configure and verify interswitch connectivity
- Describe Cisco Wireless Architectures and AP modes
- Configure and verify (Layer 2/Layer 3) EtherChannel (LACP)
|
| Security Fundamentals |
15% |
- Describe wireless security protocols (WPA, WPA2, and WPA3)
- Define key security concepts (threats, vulnerabilities, exploits, and mitigation techniques)
- Differentiate authentication, authorization, and accounting concepts
- Describe security program elements (user awareness, training, and physical access control)
- Configure and verify access control lists
- Configure device access control using local passwords
- Describe security password policies elements, such as management, complexity, and password alternatives (multifactor authentication, certificates, and biometrics)
- Configure Layer 2 security features (DHCP snooping, dynamic ARP inspection, and port security)
- Describe remote access and site-to-site VPNs
- Configure WLAN using WPA2 PSK using the GUI
|
| IP Services |
10% |
- Configure network devices for remote access using SSH
- Configure and verify inside source NAT using static and pools
- Configure and verify NTP operating in a client and server mode
- Explain the function of SNMP in network operations
- Explain the role of DHCP and DNS within the network
- Configure and verify DHCP client and relay
- Describe the capabilities and function of TFTP/FTP in the network
- Describe the use of syslog features including facilities and levels
- Explain the forwarding per-hop behavior (PHB) for QoS such as classification, marking, queuing, congestion, policing, shaping
|
>> 200-301測試引擎 <<
最優質的Cisco 200-301測試引擎是行業領先材料&授權的200-301:Cisco Certified Network Associate Exam
在你決定購買KaoGuTi的Cisco的200-301的考題之前,你將有一個免費的部分試題及答案作為試用,這樣一來你就知道KaoGuTi的Cisco的200-301考試的培訓資料的品質,希望KaoGuTi的Cisco的200-301考試資料使你的最佳選擇。
最新的 CCNA 200-301 免費考試真題 (Q13-Q18):
問題 #13
Refer to Exhibit.
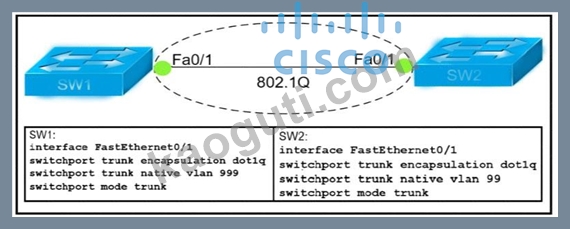
Which action do the switches take on the trunk link?
- A. The trunk forms but the mismatched native VLANs are merged into a single broadcast domain.
- B. The trunk does not form and the ports go into an err-disabled status.
- C. The trunk forms but VLAN 99 and VLAN 999 are in a shutdown state.
- D. The trunk does not form, but VLAN 99 and VLAN 999 are allowed to traverse the link.
答案:A
解題說明:
Explanation
The trunk still forms with mismatched native VLANs and the traffic can actually flow between mismatched switches. But it is absolutely necessary that the native VLANs on both ends of a trunk link match; otherwise a native VLAN mismatch occurs, causing the two VLANs to effectively merge.
For example with the above configuration, SW1 would send untagged frames for VLAN 999. SW2 receives them but would think they are for VLAN 99 so we can say these two VLANs are merged.
問題 #14
How do predictive models enhance network resource allocation?
- A. They assign IP addresses to devices.
- B. They solely monitor historical traffic volumes.
- C. They anticipate future traffic spikes.
- D. They select correct cabling types for deployment.
答案:C
解題說明:
Predictive models analyze historical data and patterns in network traffic to anticipate future demands, such as potential traffic spikes. By forecasting these trends, network administrators can proactively allocate resources, ensuring that the network has sufficient capacity to handle anticipated load increases. This approach helps maintain optimal performance and minimizes the risk of congestion or bottlenecks.
問題 #15
When a site-to-site VPN is configured which IPsec mode provides encapsulation and encryption of the entire original IP packet?
- A. IPsec transport mode with AH
- B. IPsec tunnel mode with AH
- C. IPsec transport mode with ESP
- D. IPsec tunnel mode with ESP
答案:D
問題 #16
Which device separates networks by security domains?
- A. firewall
- B. intrusion protection system
- C. access point
- D. wireless controller
答案:A
解題說明:
Firewalls are devices that are used to separate networks into different security domains.
They act as a barrier between two networks and control the flow of traffic between them.
Firewalls use a set of rules to determine what types of traffic are allowed to pass through and what is blocked. This helps protect a network from malicious traffic and unauthorized access. Additionally, firewalls can be configured to log traffic and provide additional security measures such as packet filtering and stateful inspection.
問題 #17
Refer to the exhibit.
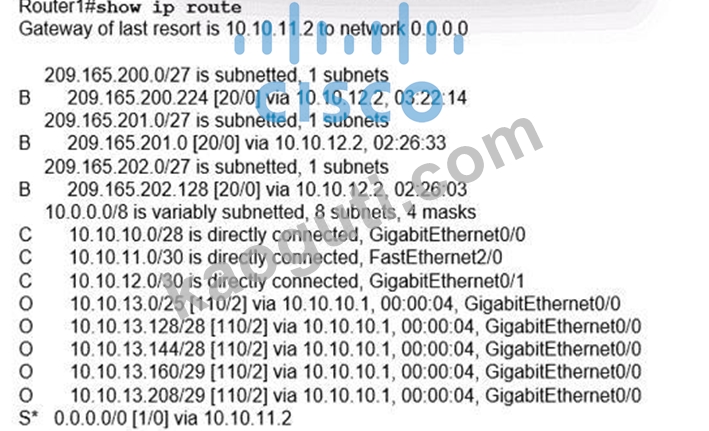
What is the subnet mask of the route to the 10.10.13.160 prefix?
- A. 255.255.255.128
- B. 255.255.255.248
- C. 255.255.248.
- D. 255.255.255.240
答案:B
問題 #18
......
你瞭解KaoGuTi的200-301考試考古題嗎?為什麼用過的人都讚不絕口呢?是不是很想試一試它是否真的那麼有效果?趕快點擊KaoGuTi的網站去下載吧,每個問題都有提供demo,覺得好用可以立即購買。你購買了考古題以後還可以得到一年的免費更新服務,一年之內,只要你想更新你擁有的資料,那麼你就可以得到最新版。有了這個資料你就能輕鬆通過200-301考試,獲得資格認證。
200-301考試證照: https://kaoguti.com/200-301_exam-pdf.html
- 200-301考古题推薦 🔑 200-301考試證照綜述 🥜 200-301證照信息 👯 透過{ tw.fast2test.com }搜索➠ 200-301 🠰免費下載考試資料200-301證照信息
- 資格考試中的最佳200-301測試引擎和領先供應商&最近更正的Cisco Cisco Certified Network Associate Exam 🙇 「 www.newdumpspdf.com 」上搜索☀ 200-301 ️☀️輕鬆獲取免費下載200-301 PDF題庫
- 由最新的200-301考試指南編訂的題庫資料 - 提高Cisco Certified Network Associate Exam考試的通過率 🏐 透過[ www.newdumpspdf.com ]輕鬆獲取☀ 200-301 ️☀️免費下載200-301最新考古題
- 高質量的200-301測試引擎,免費下載200-301考試資料得到妳想要的Cisco證書 👖 在【 www.newdumpspdf.com 】網站下載免費✔ 200-301 ️✔️題庫收集200-301熱門證照
- 200-301考古題更新 🆎 200-301考試證照綜述 🍿 200-301證照信息 🦏 透過⏩ www.newdumpspdf.com ⏪輕鬆獲取➡ 200-301 ️⬅️免費下載200-301在線題庫
- 200-301最新考古題 🎎 200-301認證考試解析 🥯 200-301證照指南 ⛴ “ www.newdumpspdf.com ”是獲取☀ 200-301 ️☀️免費下載的最佳網站200-301更新
- 高質量的200-301測試引擎,免費下載200-301考試資料得到妳想要的Cisco證書 🤕 透過⇛ tw.fast2test.com ⇚搜索《 200-301 》免費下載考試資料200-301證照信息
- 200-301在線題庫 🎱 200-301認證資料 😃 200-301考題套裝 🔭 免費下載➠ 200-301 🠰只需在⇛ www.newdumpspdf.com ⇚上搜索200-301考題套裝
- 200-301更新 📇 200-301更新 🐚 200-301證照指南 🤑 來自網站“ www.newdumpspdf.com ”打開並搜索⇛ 200-301 ⇚免費下載200-301認證資料
- 200-301 PDF題庫 😑 200-301熱門考古題 🔆 200-301熱門考古題 🌞 在➤ www.newdumpspdf.com ⮘網站下載免費➤ 200-301 ⮘題庫收集200-301證照信息
- 200-301測試引擎:Cisco Certified Network Associate Exam考試即時下載|更新的200-301 🥏 在“ www.kaoguti.com ”網站上免費搜索➽ 200-301 🢪題庫200-301 PDF題庫
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes
順便提一下,可以從雲存儲中下載KaoGuTi 200-301考試題庫的完整版:https://drive.google.com/open?id=11tkFWQYFrNp7vmwrwdjEtR6gBAu0NLPj


 icons at the top
right corner of the subsection.