NSE7_FSN_AR-7.6題庫下載, NSE7_FSN_AR-7.6最新考古題, NSE7_FSN_AR-7.6考古題更新, NSE7_FSN_AR-7.6證照考試, 最新NSE7_FSN_AR-7.6考證

想獲得Fortinet NSE7_FSN_AR-7.6認證,就來KaoGuTi網站!為您提供最好的學習資料,讓您不僅可以通過NSE7_FSN_AR-7.6考試,還可以在短時間內獲得良好的成績。我們已經幫助很多的考生順利順利通過NSE7_FSN_AR-7.6考試,獲取證書,這是一個難得的機會。現在,購買Fortinet NSE7_FSN_AR-7.6題庫之后,您的郵箱會收到我們的郵件,您可以及時下載您購買的NSE7_FSN_AR-7.6題庫并訪問,這樣可以全面地了解詳細的考試試題以及答案。
Fortinet NSE7_FSN_AR-7.6 Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| System Architecture & Design |
20% |
- FortiOS 7.6 architecture & components
- Security Fabric integration & scaling
- Hardware sizing & resource planning
- VDOM design & multi-tenant deployment
|
| Security Policy & Services |
10% |
- Identity-based policies
- Advanced firewall & security profile design
- NAT & IP pool optimization
|
| Monitoring & Troubleshooting |
10% |
- Connectivity & performance troubleshooting
- Diagnostic tools & CLI analysis
- Fabric synchronization issues
|
| Advanced Routing & VPN |
25% |
- SD-WAN design & SLA management
- OSPF, BGP, IS-IS configuration & optimization
- IPsec VPN & ADVPN architecture
- Route redistribution & filtering
|
| High Availability & Redundancy |
15% |
- Cross-data center redundancy
- Session synchronization & failover
- FGCP/FGSP/vCluster deployment
|
| Centralized Management |
20% |
- Configuration provisioning & version control
- Policy packages & object templates
- FortiAnalyzer logging & reporting
- FortiManager 7.6 deployment & role assignment
|
>> NSE7_FSN_AR-7.6題庫下載 <<
NSE7_FSN_AR-7.6最新考古題 - NSE7_FSN_AR-7.6考古題更新
獲得 Fortinet Fortinet 認證對於考生而言有很多好處,相對于考生尋找工作而言,一張 Fortinet 的 NSE7_FSN_AR-7.6 認證會讓你倍受青睞的企業信任狀,帶來更好的工作機會。要想通過此認證學習過程中要注意方法,最重要的是需要毅力,如果有相關的工作經驗,學起來可能輕鬆一點,否則的話,你需要付出更多的勞動。Fortinet 的 NSE7_FSN_AR-7.6 證照作為全球IT領域專家 Fortinet 證照之一,是許多大中IT企業選擇人才標準的必備條件。
最新的 NSE 7 Network Security Architect NSE7_FSN_AR-7.6 免費考試真題 (Q15-Q20):
問題 #15
Refer to the exhibit.
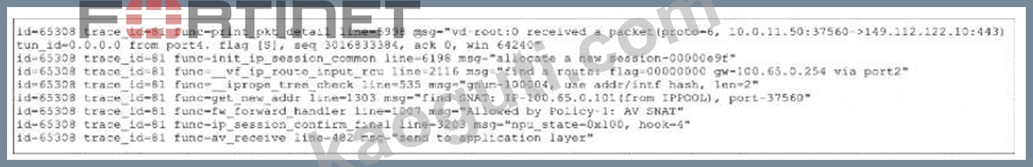
Which two observations can you make about the web filter traffic captured using the flow tool? (Choose two.)
- A. The firewall policy is configured with proxy-based inspection mode.
- B. The session is offloaded to the NPU.
- C. The web filter profile is configured with proxy-based inspection mode.
- D. The HTTPS port is mapped to 443 in the SSL/SSH Inspection Profile
答案:A,C
解題說明:
Analyze the " Send to Application Layer " Message:
The most critical line in the debug output is: id=65308 ... func=av_receive ... msg= " send to application layer
"
Meaning: This message indicates that the FortiGate kernel is handing the packet over to a user-space daemon (specifically the WAD/Proxy process, indicated by av_receive handlers) for deep inspection.
Implication: This behavior is the hallmark of Proxy-based inspection. In Flow-based inspection, the traffic is handled by the IPS engine (often within the kernel or via specific IPS handlers like ips_measure), and you would not typically see a " send to application layer " message for standard web filtering.
Evaluate Option B (Firewall Policy Mode):
Since the traffic is being sent to the application layer proxy, the Firewall Policy controlling this traffic (Policy ID 1, as seen in Allowed by Policy-1) must be configured with Inspection Mode = Proxy. If it were Flow- based, the traffic would stay in the flow path. Thus, Option B is correct.
Evaluate Option C (Web Filter Profile Mode):
In FortiOS, when a firewall policy is set to Proxy-based inspection, the security profiles (like Web Filter) applied to that policy also operate in Proxy-based inspection mode. The presence of the av_receive function confirms that the content inspection (Web Filter/AV) is being performed by the proxy engine. Thus, Option C is correct.
Why Option A is Incorrect (NPU Offload):
The output shows npu_state=0x100. In the context of a flow trace where traffic is being " sent to application layer, " this confirms the session is not fully offloaded to the NPU (Network Processor). Offloaded traffic (Fast Path) is handled by the hardware and would not generate these specific CPU-level debug logs for the payload inspection phase. The proxying process requires CPU intervention.
Why Option D is Incorrect (Port Mapping):
While valid protocol mapping is necessary for inspection, the specific debug output shown is a direct result of the Inspection Mode (Proxy vs. Flow). The observation of the traffic moving to the application layer is primarily caused by the policy and profile mode settings, making B and C the direct " observations " derived from the log data.
Reference:
FortiGate Troubleshooting (Debug Flow): " If the debug flow shows msg= ' send to application layer ' , it confirms the traffic is being handled by the proxy (WAD) for Proxy-based inspection. "
問題 #16
Refer to the exhibit, which shows a truncated output of a real-time LDAP debug.
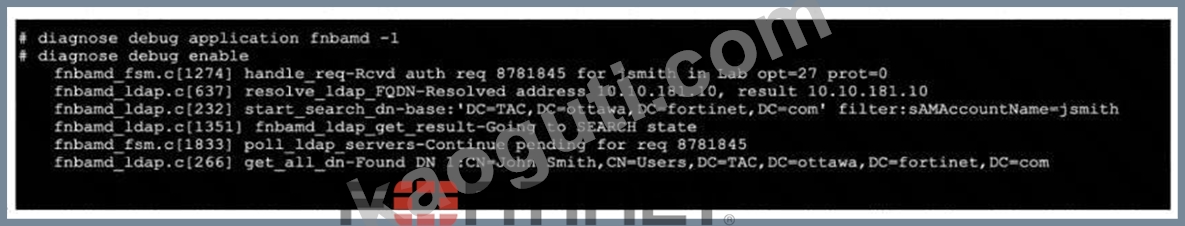
What two conclusions can you draw from the output? (Choose two.)
- A. FortiOS is able to locate the user in step 3 (Bind Request) of the LDAP authentication process.
- B. The name of the configured LDAP server is Lab.
- C. The user is authenticating using CN=John Smith.
- D. FortiOS is performing the second step (Search Request) in the LDAP authentication process.
答案:B,D
解題說明:
The exhibit shows these key lines:
handle_req-Rcvd auth req ... for jsmith in Lab
start_search_dn-base: ' DC=TAC,DC=ottawa,DC=fortinet,DC=com ' filter:sAMAccountName=jsmith get_all_dn-Found DN 1:CN=John Smith,CN=Users,DC=TAC,DC=ottawa,DC=fortinet,DC=com The study guide explicitly shows the same LDAP real-time debug pattern and says the request line includes the LDAP server object name:
handle_req-Rcvd auth req ... for jsmith in Lab ...
That supports A: Lab is the configured LDAP server name being used for this authentication request.
For the LDAP flow stage, the study guide states:
"An fnbamd_ldap_build_dn_search_req-base message indicates that FortiGate is performing step two:
searching for the user in the LDAP tree." It also says that if the LDAP server finds the user, the output shows the user's full DN.
That matches the exhibit's start_search_dn-base ... filter:sAMAccountName=jsmith and Found DN ...
CN=John Smith... lines, so D is correct.
Why the other options are wrong:
B is wrong because the exhibit shows FortiOS has found the user DN CN=John Smith,..., but that does not mean the user is already authenticating with that DN in this step. The study guide says this DN is discovered in step 2, and only in step 3 does FortiGate bind using the user DN.
C is wrong because the exhibit is showing step 2 (Search Request), not step 3 (Bind Request). The study guide separates these steps clearly and shows step 3 with fnbamd_ldap_build_userbind_req-Trying DN ... and
__ldap_build_bind_req-Binding to ' CN=John Smith,... '
問題 #17
A VPN tunnel is up. To monitor traffic flow, the administrator enters the following CLI commands on an SSH session on FortiGate:
# diagnose debug enable
# diagnose sniffer packet any ' udp and port 500 ' 4
However, the sniffer does not show any output. Assuming default configuration values, what are two possible reasons there is no output? (Choose two answers)
- A. The sniffer output will be ignored because running diagnose debug enable shows only application real- time debugs.
- B. The filter should be modified to also capture packets for TCP port 443 or UDP port 4500.
- C. NAT Traversal is enabled.
- D. The sniffer must be restricted to the remote peer IP address.
答案:B,C
解題說明:
The correct answers are A and B.
The study guide says:
"If NAT-T is enabled, and there is a FortiGate located in the middle that is running NAT, the sniffer command must use a different filter. In this case, IKE traffic uses UDP port 500, but switches to UDP port
4500 during the tunnel negotiation. Additionally, ESP traffic is encapsulated inside the UDP 4500 channel." It also says:
"In some networks, UDP is blocked by firewalls or ISPs. In those cases, you can configure your VPN tunnel to use IKE over TCP in the phase 1 configuration. The default IKE TCP port is 443..." And the study guide gives the correct capture examples:
No NAT: host < remote-gw > and udp port 500
With NAT and NAT-T: host < remote-gw > and (udp port 500 or udp port 4500) So:
B is correct because with NAT Traversal enabled, the tunnel may no longer be using only UDP 500. It can move to UDP 4500, so the current filter may miss the traffic.
A is correct because the filter may need to be expanded to include UDP 4500 for NAT-T, or TCP 443 when IKE over TCP is used.
Why the other options are wrong:
C is wrong because restricting the filter to the remote peer IP can make the capture more precise, but it is not required for the sniffer to display output. The problem here is the port/protocol choice, not the lack of a host filter. The study guide examples use host filtering as an aid, not as a requirement.
D is wrong because diagnose debug enable is used to enable real-time debug output for applications, but it does not suppress or invalidate sniffer output. Sniffer capture is a separate command path. Fortinet documentation separately documents diagnose sniffer packet ... for packet capture and diagnose debug enable for debug features.
So the verified answers are: A, B.
問題 #18
Refer to the exhibit.
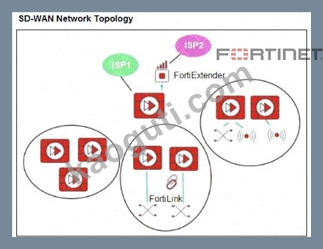
You want to configure SD-WAN on a network, as shown in the exhibit. The network contains many FortiGate devices. Some are used as next-generation firewalls (NGFWs), and some are deployed with extensions such as FortiSwitch, FortiAP, or FortiExtender.
Which factor should you consider when planning the deployment? (Choose one answer.)
- A. You can build an SD-WAN topology that includes all devices. The hubs can be FortiGate devices with FortiExtender.
- B. You should exclude FortiGate devices with FortiLink connections from the SD-WAN topology.
- C. You should build multiple SD-WAN topologies. Each topology should contain only one type of extension.
- D. You can build an SD-WAN topology that includes all devices. The hubs must be devices without extensions.
答案:A
解題說明:
The SD-WAN 7.6 Enterprise Administrator Study Guide states: "An SD-branch is a site with an SD-WAN spoke FortiGate device and one or multiple extensions." It explains that FortiSwitch and FortiAP provide wired and wireless LAN connectivity through FortiLink, while FortiExtender supplements WAN connectivity by providing 4G/5G transport.
The guide further explains that the management plane sees extension-device ports as logical interfaces belonging to the controlling FortiGate. Therefore, FortiSwitch, FortiAP, and FortiExtender do not become independent SD-WAN topology nodes and do not require separate topologies. FortiGate devices with FortiLink connections also do not need to be excluded.
FortiExtender is specifically designed as a natural SD-WAN extension that introduces cellular connectivity as another WAN transport. Consequently, a FortiGate using FortiExtender can function as a hub, provided it satisfies the required capacity, routing, and IPsec design requirements. There is no rule requiring hubs to be extension-free. Therefore, option D correctly describes the unified topology shown in the exhibit.
問題 #19
Which statement about IKEv2 is true?
- A. IKEv1 and IKEv2 use the same TCP port but run on different UDP ports.
- B. IKEv1 and IKEv2 share the concept of phase1 and phase2.
- C. Both IKEv1 and IKEv2 share the feature of asymmetric authentication.
- D. IKEv1 and IKEv2 have enough of the header format in common that both versions can run over the same UDP port.
答案:D
解題說明:
The correct answer is B .
The study guide explicitly states: "IKE version 2 does not interoperate with IKE version 1, but they share enough of the header format that both versions can unambiguously operate over the same UDP port." That directly proves B .
Why the other options are wrong:
* A is wrong because the study guide shows authentication methods as Asymmetric for IKEv2 and Symmetric for IKEv1
* C is wrong because the study guide does not say they use the same TCP port; instead, it specifically says they can operate over the same UDP port
* D is wrong because the study guide states: "IKEv2 does not use the concept of phase 1 or phase 2" , even though FortiOS CLI/GUI still uses those terms for configuration purposes
問題 #20
......
如果你是一名IT職員,你想升職嗎?你想成為一名專業的IT技術專家嗎?那就趕緊報名參加Fortinet的NSE7_FSN_AR-7.6考試認證吧!你也知道這個認證對你們來說是多麼的重要,不要擔心考不過,不要懷疑自己的能力,只要參加了Fortinet的NSE7_FSN_AR-7.6考試認證。所有的備考問題都來找KaoGuTi,它是一家專業的IT認證培訓網站,有了它在,你考試難題將不攻而破,KaoGuTi Fortinet的NSE7_FSN_AR-7.6考試認證培訓資料可以幫助你輕鬆的應對考試,它幫助過的考生數不勝數,保證100%成功,還不趕緊行動,點擊KaoGuTi,早日實現你的IT夢吧。
NSE7_FSN_AR-7.6最新考古題: https://kaoguti.com/NSE7_FSN_AR-7.6_exam-pdf.html
- 有用的NSE7_FSN_AR-7.6題庫下載 |高通過率的考試材料|100%合格率的NSE7_FSN_AR-7.6:Fortinet NSE 7 - Secure Networking 7.6 Architect 🍮 請在➠ www.pdfexamdumps.com 🠰網站上免費下載《 NSE7_FSN_AR-7.6 》題庫NSE7_FSN_AR-7.6題庫資訊
- NSE7_FSN_AR-7.6最新考證 🔱 NSE7_FSN_AR-7.6題庫資訊 ☔ 最新NSE7_FSN_AR-7.6考證 🎮 打開網站➤ www.newdumpspdf.com ⮘搜索▛ NSE7_FSN_AR-7.6 ▟免費下載NSE7_FSN_AR-7.6套裝
- NSE7_FSN_AR-7.6考試心得 👓 NSE7_FSN_AR-7.6考試備考經驗 🐌 NSE7_FSN_AR-7.6下載 🈵 【 www.pdfexamdumps.com 】提供免費➥ NSE7_FSN_AR-7.6 🡄問題收集NSE7_FSN_AR-7.6認證題庫
- 新版的NSE7_FSN_AR-7.6題庫上線 - 下載NSE7_FSN_AR-7.6題庫 - 通過NSE7_FSN_AR-7.6認證考試 🐉 開啟( www.newdumpspdf.com )輸入➽ NSE7_FSN_AR-7.6 🢪並獲取免費下載NSE7_FSN_AR-7.6套裝
- 最新NSE7_FSN_AR-7.6考證 ☣ NSE7_FSN_AR-7.6權威認證 📦 NSE7_FSN_AR-7.6認證題庫 😾 開啟➽ www.newdumpspdf.com 🢪輸入【 NSE7_FSN_AR-7.6 】並獲取免費下載NSE7_FSN_AR-7.6软件版
- Fortinet NSE7_FSN_AR-7.6題庫下載和Newdumpspdf - 保證認證成功,簡便的培訓方式 🎁 開啟( www.newdumpspdf.com )輸入「 NSE7_FSN_AR-7.6 」並獲取免費下載新版NSE7_FSN_AR-7.6考古題
- 可信任的NSE7_FSN_AR-7.6在資格考試領導者和更正的NSE7_FSN_AR-7.6題庫下載:Fortinet NSE 7 - Secure Networking 7.6 Architect 🅰 免費下載✔ NSE7_FSN_AR-7.6 ️✔️只需進入⏩ tw.fast2test.com ⏪網站NSE7_FSN_AR-7.6最新考證
- 可信任的NSE7_FSN_AR-7.6在資格考試領導者和更正的NSE7_FSN_AR-7.6題庫下載:Fortinet NSE 7 - Secure Networking 7.6 Architect 💑 ➤ www.newdumpspdf.com ⮘提供免費✔ NSE7_FSN_AR-7.6 ️✔️問題收集NSE7_FSN_AR-7.6學習筆記
- Fortinet NSE7_FSN_AR-7.6題庫下載和tw.fast2test.com - 保證認證成功,簡便的培訓方式 🎨 在{ tw.fast2test.com }網站下載免費⇛ NSE7_FSN_AR-7.6 ⇚題庫收集NSE7_FSN_AR-7.6最新試題
- Fortinet NSE7_FSN_AR-7.6題庫下載和Newdumpspdf - 認證考試材料的領先提供商 🟦 “ www.newdumpspdf.com ”上的免費下載[ NSE7_FSN_AR-7.6 ]頁面立即打開新版NSE7_FSN_AR-7.6考古題
- 100%合格率的Fortinet NSE7_FSN_AR-7.6題庫下載和授權的www.kaoguti.com - 資格考試中的領先提供商 ✅ 立即到《 www.kaoguti.com 》上搜索⮆ NSE7_FSN_AR-7.6 ⮄以獲取免費下載NSE7_FSN_AR-7.6學習筆記
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes


 icons at the top
right corner of the subsection.