SC-500最新試題, SC-500學習指南, SC-500考試題庫, SC-500在線考題, SC-500題庫分享

你是可以免費下載KaoGuTi為你提供的部分關於Microsoft SC-500認證考試練習題及答案的作為嘗試,那樣你會更有信心地選擇我們的KaoGuTi的產品來準備你的Microsoft SC-500 認證考試。快將我們KaoGuTi的產品收入囊中吧。
Microsoft SC-500 Exam Syllabus Topics:
| Section |
Weight |
Objectives |
| Manage identity, access, and governance |
20-25% |
- Secure access to resources using Microsoft Entra ID
- Secure secrets and keys using Azure Key Vault
- Implement governance with Azure Policy and Defender for Cloud
|
| Manage and monitor security posture |
20-25% |
- Manage security posture using Microsoft Defender for Cloud
- Implement activity and event collection in Microsoft Sentinel
- Implement Microsoft Security Copilot configuration
|
| Secure storage, databases, and networking |
25-30% |
- Implement security for storage accounts
- Implement security for Azure network services
- Implement security for databases
|
| Secure compute |
20-25% |
- Implement security for application platform services
- Implement security for servers and virtual machines (VMs)
- Implement security for AI workloads
|
>> SC-500最新試題 <<
輕松過SC-500認證的考古題 - 是最有效的Implementing End-to-End Security Controls for Cloud and AI Workloads-SC-500考試備考資料
多考一些證照對於年輕人來說不是件壞事,是加薪升遷的法寶。對於參加 SC-500 考試的年輕人而言,不需要擔心 Microsoft 證照沒有辦法過關,只要找到最新的Microsoft SC-500 考題,就是 SC-500 考試順利過關的最佳方式。SC-500題庫涵蓋了考試中心的正式考試的所有的題目。確保了考生能順利通過考試,獲得 Microsoft 認證證照。
最新的 Microsoft Certified: Information Security Administrator Associate SC-500 免費考試真題 (Q11-Q16):
問題 #11
You use Microsoft Security Copilot.
Users are assigned either the Security Copilot Contributor role or the Security Copilot Owner role.
A contributor enables a custom plugin that is NOT approved, and some Security Copilot features in embedded experiences no longer function.
You need to ensure that plugins affecting all users can only be added by owners.
What should you do in the Plugin settings?
- A. Select Owners only to configure which users can add custom plugins at the user scope.
- B. Select Contributors and Owners to configure which users can add custom plugins at the workspace scope.
- C. Select Owners only to configure which users can add custom plugins at the workspace scope.
- D. Select Contributors and Owners to configure which users can add custom plugins at the user scope.
答案:C
解題說明:
To restrict the addition and management of plugins that affect all users to Owners only, you should configure the setting at the workspace scope.
In Microsoft Security Copilot, selecting Owners only at the workspace scope prevents Contributors from adding, configuring, or managing custom plugins for the entire organization.
Contributors will only be allowed to manage plugins for themselves at the user scope, ensuring governance over platform-wide integrations.
Reference:
https://learn.microsoft.com/en-us/copilot/security/authentication
問題 #12
You have a Microsoft 365 tenant that has Microsoft 365 Copilot enabled for a pilot group.
Users frequently generate responses based on Microsoft Teams chats and Microsoft SharePoint Online sites.
You use Microsoft Purview Data Security Posture Management (DSPM) to identify oversharing risks and create policies based on the recommendations.
You need to manage and edit the policies created by DSPM.
Which Microsoft Purview solution should you use?
- A. Communication Compliance
- B. Insider Risk Management
- C. Information Protection
- D. Data Loss Prevention
答案:D
解題說明:
To manage and edit the specific Data Loss Prevention (DLP) or Information Protection policies generated by DSPM, the best feature to use is Microsoft Purview Data Loss Prevention (DLP).
While DSPM for AI assesses data risks and recommends policies (such as preventing Copilot from accessing sensitive sites or limiting risky prompts), the actual management, fine-tuning, and editing of these resulting guardrails occur natively within the centralized Data Loss Prevention or Information Protection dashboards.
Reference:
https://learn.microsoft.com/en-us/purview/data-security-posture-management-oversharing
問題 #13
You have an Azure Logic Apps Consumption workflow that uses a Request trigger. All supported authentication methods are enabled on the Request trigger You need to ensure that the endpoint accepts only OAuth-based requests. The solution must minimize costs.
What should you do?
- A. Disable shared access signature (SAS) authentication for the Request trigger.
- B. Deploy Azure API Management.
- C. Enable Secure Inputs and enable Secure Outputs for the Request trigger.
- D. Use OAuth 2.0 authorization.
答案:A
解題說明:
A Logic Apps Request trigger can be invoked through different authorization mechanisms. If all supported methods are enabled but only OAuth-based requests should be accepted, disabling shared access signature authentication removes the non-OAuth shared-secret URL model. Secure Inputs and Secure Outputs protect run-history data but do not control request authentication. API Management could enforce auth but adds cost and complexity, which the requirement says to minimize. The exam objective emphasizes practical identity enforcement rather than cosmetic configuration. A valid answer must identify who authenticates, what permission is granted, where the scope is applied, and whether the method continues to work without passwords or secrets. That is why the selected answer is preferred over broader administrative roles or unrelated access settings. The result is a direct exam-style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source/topic: SC-500 Study Guide > Logic Apps security; Microsoft Learn > Request trigger SAS and OAuth authentication.
問題 #14
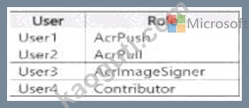
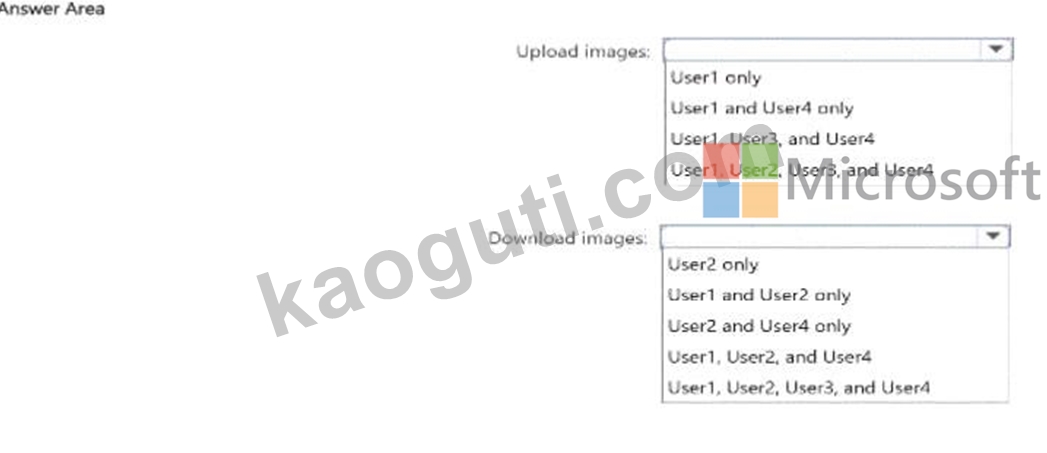
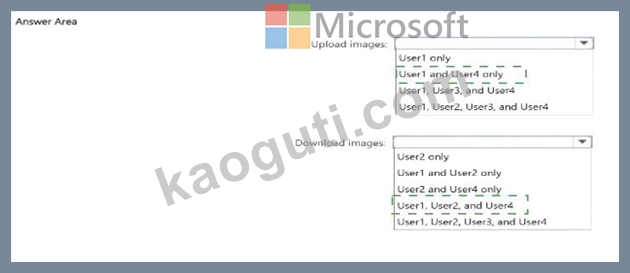
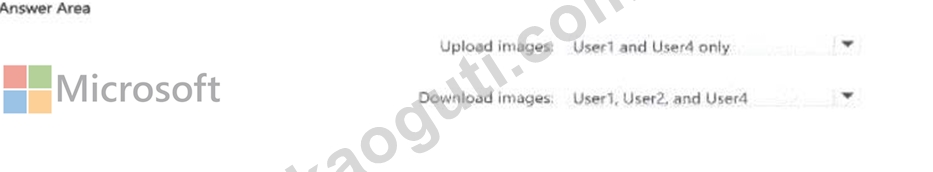
You have an Azure Container Registry named Registry1-
You add role assignments for Registry! as shown in the following table.
答案:
解題說明:
Explanation:
問題 #15
You have a Microsoft Copilot Studio agent.
A Microsoft Power Platform administrator configures external threat detection for the agent by using a Microsoft Entra application.
You need to ensure that real-time protection is enabled during agent runtime.
What should you do in the Microsoft Defender portal?
- A. Configure Microsoft Defender for Cloud Apps session policies.
- B. Connect the Microsoft 365 app connector.
- C. From Microsoft Sentinel, configure the Microsoft Purview data connector.
- D. Enable Global Secure Access for Agents.
答案:B
解題說明:
For external threat detection and real-time agent protection to work, Defender must receive app activity through the Microsoft 365 app connector. Session policies in Defender for Cloud Apps govern user sessions, Global Secure Access controls network access, and a Sentinel connector is for log ingestion and investigation.
The Microsoft 365 app connector is the required Defender portal-side integration for this runtime protection scenario. For SC-500, compute controls are evaluated by workload type: VM, Arc server, AKS, container registry, container group, Functions, Logic Apps, App Service, and AI agent runtime. The right answer uses the Microsoft control that is native to that workload. Broad Azure roles or unrelated monitoring services would either overgrant access or fail to enforce the required security state. The result is a direct exam-style implementation choice: it changes the required security behavior without relying on unrelated monitoring, manual cleanup, or excessive privilege. Official Microsoft source/topic: SC-500 Study Guide > AI workload runtime protection; Microsoft Learn > Microsoft 365 app connector and Copilot agent protection.
問題 #16
......
Microsoft的SC-500考試是IT行業之中既流行也非常重要的一個考試,我們準備了最優質的學習指南和最佳的線上服務,特意為IT專業人士提供捷徑,KaoGuTi Microsoft的SC-500考題涵蓋了所有你需要知道的考試內容和答案,如果你通過我們KaoGuTi的考題模擬,你就知道這才是你千方百計想得到的東西,並且認為這樣才真的是為考試做準備的
SC-500學習指南: https://kaoguti.com/SC-500_exam-pdf.html
- SC-500考試資料 🔄 SC-500熱門考題 🔢 SC-500學習筆記 🥌 在⮆ tw.fast2test.com ⮄網站上查找「 SC-500 」的最新題庫SC-500考試證照
- SC-500在線考題 🔎 SC-500權威認證 🐘 SC-500考試資料 🔑 在▶ www.newdumpspdf.com ◀網站下載免費➽ SC-500 🢪題庫收集SC-500題庫更新
- SC-500試題 🔱 SC-500考試資料 🙉 SC-500資料 🕔 到{ www.newdumpspdf.com }搜尋[ SC-500 ]以獲取免費下載考試資料SC-500考試資料
- SC-500最新試題 100%通過|高質量的Microsoft Implementing End-to-End Security Controls for Cloud and AI Workloads學習指南確保通過 🩲 “ www.newdumpspdf.com ”最新✔ SC-500 ️✔️問題集合SC-500在線考題
- 最好的SC-500最新試題和資格考試中的領先材料提供者和值得信賴的SC-500學習指南 🐝 ▛ www.vcesoft.com ▟提供免費➡ SC-500 ️⬅️問題收集SC-500熱門考題
- SC-500權威認證 🦌 新版SC-500考古題 🧄 SC-500最新考古題 🤴 ▛ www.newdumpspdf.com ▟網站搜索[ SC-500 ]並免費下載SC-500學習筆記
- 高質量的SC-500最新試題,免費下載SC-500考試題庫幫助妳通過SC-500考試 💇 在✔ www.vcesoft.com ️✔️網站下載免費▶ SC-500 ◀題庫收集SC-500考古題介紹
- 最實用的SC-500認證考古題 👈 「 www.newdumpspdf.com 」上搜索➥ SC-500 🡄輕鬆獲取免費下載SC-500學習指南
- 高通過率的SC-500最新試題,高質量的考試指南幫助妳快速通過SC-500考試 💠 【 www.kaoguti.com 】上搜索⮆ SC-500 ⮄輕鬆獲取免費下載SC-500考試證照
- 最好的SC-500最新試題和資格考試中的領先材料提供者和值得信賴的SC-500學習指南 🚉 「 www.newdumpspdf.com 」上的免費下載⇛ SC-500 ⇚頁面立即打開SC-500更新
- 高通過率的SC-500最新試題,高質量的考試指南幫助妳快速通過SC-500考試 🕌 ➥ www.newdumpspdf.com 🡄上搜索➽ SC-500 🢪輕鬆獲取免費下載SC-500熱門考題
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes


 icons at the top
right corner of the subsection.