NSE6_SDW_AD-7.6題庫最新資訊, NSE6_SDW_AD-7.6考題套裝, NSE6_SDW_AD-7.6考古题推薦, NSE6_SDW_AD-7.6熱門題庫, NSE6_SDW_AD-7.6證照資訊

P.S. KaoGuTi在Google Drive上分享了免費的2026 Fortinet NSE6_SDW_AD-7.6考試題庫:https://drive.google.com/open?id=1kYMO_YaQQv19hpo-P_lJc3pIfP0pNt8q
我們都很清楚 Fortinet NSE6_SDW_AD-7.6 認證考試在IT行業中的地位是駐足輕重的地位,但關鍵的問題是能夠拿到Fortinet NSE6_SDW_AD-7.6的認證證書不是那麼簡單的。我們很清楚地知道網上缺乏有高品質的準確性高的相關考試資料。KaoGuTi的考試練習題和答案可以為一切參加IT行業相關認證考試的人提供一切所急需的資料。它能時時刻刻地提供你們想要的資料,購買我們所有的資料能保證你通過你的第一次Fortinet NSE6_SDW_AD-7.6認證考試。
Fortinet NSE6_SDW_AD-7.6 Exam Overview:
>> NSE6_SDW_AD-7.6題庫最新資訊 <<
完整的Fortinet NSE6_SDW_AD-7.6:Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator題庫最新資訊 - 精心準備的KaoGuTi NSE6_SDW_AD-7.6考題套裝
KaoGuTi不僅可以成就你的夢想,而且還會為你提供一年的免費更新和售後服務。KaoGuTi給你提供的練習題的答案是100%正確的,可以幫助你通過Fortinet NSE6_SDW_AD-7.6的認證考試的。你可以在網上免費下載KaoGuTi為你提供的部分Fortinet NSE6_SDW_AD-7.6的認證考試的練習題和答案作為嘗試。
Fortinet NSE6_SDW_AD-7.6 考試大綱:
| 主題 |
簡介 |
| 主題 1 |
- SD-WAN setup: This domain covers how to deploy an enterprise SD-WAN environment by designing SD-WAN members and zones and configuring them for efficient traffic management. It also focuses on implementing Performance SLAs to monitor link quality and ensure applications use the best available path.
|
| 主題 2 |
- Rules and routing: This section explains how to design and apply SD-WAN rules to control traffic steering across multiple WAN links. It also includes configuring SD-WAN routing to ensure proper path selection and connectivity between networks.
|
| 主題 3 |
- Centralized management: This domain focuses on deploying and managing SD-WAN using FortiManager for centralized control. It includes implementing branch configuration deployment and using SD-WAN Manager with overlay orchestration to simplify large-scale network management.
|
| 主題 4 |
- SD-WAN troubleshooting: This domain explains how to diagnose and resolve issues related to SD-WAN operation. It includes troubleshooting SD-WAN rules, session behavior, routing problems, and ADVPN connectivity to maintain reliable network performance.
|
| 主題 5 |
- Advanced IPsec: This section covers the deployment of advanced IPsec configurations within SD-WAN environments. It includes implementing hub-and-spoke IPsec topologies, configuring ADVPN, and supporting multihub, multiregion, and large-scale secure SD-WAN deployments.
|
最新的 Fortinet NSE 6 NSE6_SDW_AD-7.6 免費考試真題 (Q11-Q16):
問題 #11
You are tasked with configuring ADVPN 2.0 on an SD-WAN topology already configured for ADVPN. What should you do to implement ADVPN 2.0 in this scenario?
- A. Update the IPsec tunnel configuration on the branches.
- B. Update the SD-WAN configuration on the branches.
- C. Update the IPsec tunnel configurations on the hub.
- D. Delete the existing ADVPN configuration and configure ADVPN 2.0.
答案:C
問題 #12
Which three factors about SLA targets and SD-WAN rules should you consider when configuring SD-WAN rules? (Choose three.)
- A. SLA targets are used only by SD-WAN rules that are configured with a Lowest Cost (SLA) strategy.
- B. SD-WAN rules can use SLA targets to check whether the preferred members meet the SLA requirements.
- C. When configuring an SD-WAN rule, you can select multiple SLA targets if they are from the same performance SLA.
- D. Member metrics are measured only if a rule uses the SLA target.
- E. When configuring an SD-WAN rule, you can select multiple SLA targets from different performance SLAs.
答案:A,B,E
解題說明:
The use of SLA targets is specific to certain SD-WAN strategies. The "Lowest Cost (SLA)" and
"Maximize Bandwidth (SLA)" strategies are explicitly designed to use the configured SLA targets to make routing decisions. The "Best Quality" strategy uses performance metrics but does not necessarily require or reference SLA targets in the same way, while "Manual" does not use metrics at all for path selection.
This is a core function of SD-WAN rules with SLA targets. The purpose of configuring an SLA target with specific thresholds for latency, jitter, and packet loss is to define what is considered
"acceptable" performance for an application. SD-WAN rules then use these targets to check if the members (interfaces) meet these requirements before a flow is steered over them, ensuring that a preferred path still offers a good user experience.
FortiGate allows for a single SD-WAN rule to reference multiple, different performance SLAs. This is crucial for complex deployments where a single SD-WAN rule needs to handle traffic for multiple applications that have distinct performance requirements. For example, a single rule might direct VoIP traffic based on one performance SLA with strict latency/jitter targets, while simultaneously handling general web traffic using another performance SLA with more lenient requirements.
問題 #13
Refer to the exhibit that shows a diagnose output on a FortiGate device.
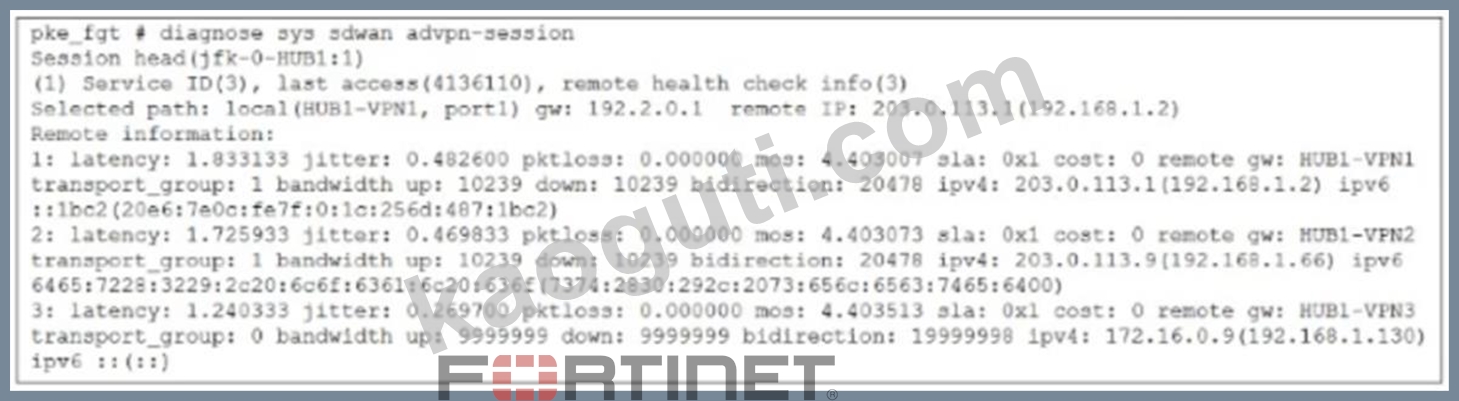
Based on the output shown in the exhibit, what can you conclude about the device role and how it handles health checks?
- A. The device is a hub and it receives health-check measures for the tunnels of a spoke.
- B. The device is a spoke and it receives health-check measures for the tunnels of another spoke.
- C. The device is a hub and it receives embedded health-check measures for each tunnel from the spoke.
- D. The device is a spoke and it provides embedded health-check measures for each tunnel to the hub.
答案:D
解題說明:
The output indicates a spoke-side ADVPN session where the local interfaces are VPNs toward HUB1, meaning the device is a branch connecting to hub tunnels. In this role, the spoke performs performance measurements for each SD-WAN tunnel and embeds these health-check results into the ADVPN session information. These metrics are then provided upstream to the hub to support dynamic shortcut and path selection decisions.
問題 #14
Refer to the exhibit, which shows the SD-WAN rule status and configuration.
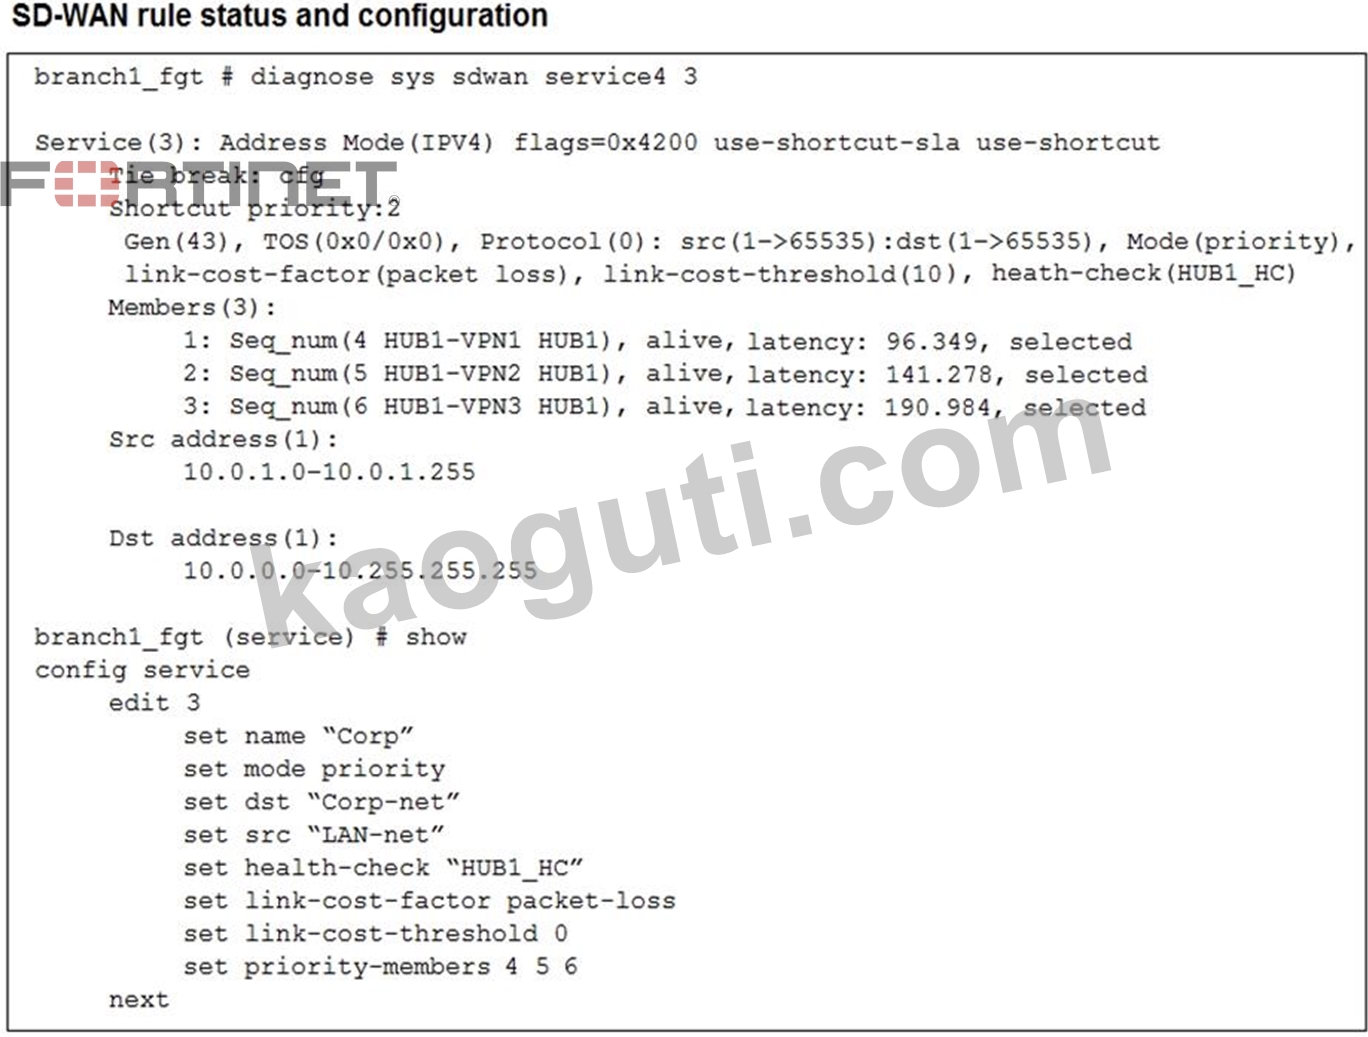
Based on the exhibit, which change in the measured latency will first make HUB1-VPN3 the new preferred member?
- A. When HUB1-VPN1 has a latency of 200 ms
- B. When HUB1-VPN3 has a latency of 90 ms
- C. When HUB1-VPN3 has a latency of 80 ms
- D. When HUB1-VPN3 has a lower latency than HUB1-VPN1 and HUB1-VPN2
答案:A
解題說明:
The rule is in priority mode with HUB1-VPN1 (seq 4) as the first preferred member, HUB1-VPN2 second, and HUB1-VPN3 third. Latency itself does not cause HUB1-VPN3 to become preferred unless a higher- priority member fails SLA. If HUB1-VPN1's latency exceeds the SLA threshold (here simulated by latency reaching 200 ms), FortiGate stops using it and moves down the priority list. That is when HUB1-VPN3 could become the active path.
問題 #15
What are three key routing principles of SD-WAN? (Choose three.)
- A. SD-WAN rules are skipped if the best route to the destination is not an SD-WAN member.
- B. Directly connected routes have precedence over SD-WAN rules.
- C. SD-WAN members are skipped if they do not have a valid route to the destination.
- D. Policy routes have precedence over SD-WAN rules.
- E. SD-WAN rules are skipped if the best route to the destination is a static route
答案:A,C,D
解題說明:
Fortinet outlines key SD-WAN routing principles:
"Policy routes are always evaluated before SD-WAN rules, meaning if a policy route matches, SD-WAN steering is bypassed. If the best route for a destination is not via an SD-WAN member, SD-WAN rules do not apply, and members are ignored if they lack a valid route. This hierarchy ensures traffic always follows the most deterministic and valid path according to configuration." Understanding these principles is critical for correct SD-WAN and routing integration.
問題 #16
......
NSE6_SDW_AD-7.6考題套裝: https://kaoguti.com/NSE6_SDW_AD-7.6_exam-pdf.html
- 高質量的NSE6_SDW_AD-7.6題庫最新資訊和準確的Fortinet認證培訓 - 通過無憂Fortinet Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator 🦗 打開網站“ tw.fast2test.com ”搜索➡ NSE6_SDW_AD-7.6 ️⬅️免費下載NSE6_SDW_AD-7.6考古題分享
- NSE6_SDW_AD-7.6套裝 🤡 NSE6_SDW_AD-7.6最新考古題 🚧 NSE6_SDW_AD-7.6測試 🎲 透過【 www.newdumpspdf.com 】搜索⏩ NSE6_SDW_AD-7.6 ⏪免費下載考試資料NSE6_SDW_AD-7.6考試心得
- 最受推薦的NSE6_SDW_AD-7.6題庫最新資訊,免費下載NSE6_SDW_AD-7.6考試題庫得到妳想要的Fortinet證書 🤬 在➠ www.kaoguti.com 🠰網站上免費搜索⮆ NSE6_SDW_AD-7.6 ⮄題庫NSE6_SDW_AD-7.6考試心得
- NSE6_SDW_AD-7.6考古題分享 📌 NSE6_SDW_AD-7.6考試心得 👖 最新NSE6_SDW_AD-7.6題庫資源 🏞 免費下載《 NSE6_SDW_AD-7.6 》只需進入[ www.newdumpspdf.com ]網站NSE6_SDW_AD-7.6最新考古題
- NSE6_SDW_AD-7.6指南 💧 最新NSE6_SDW_AD-7.6題庫資源 👾 NSE6_SDW_AD-7.6學習筆記 🧂 《 www.newdumpspdf.com 》上的“ NSE6_SDW_AD-7.6 ”免費下載只需搜尋NSE6_SDW_AD-7.6套裝
- NSE6_SDW_AD-7.6題庫下載 🌺 NSE6_SDW_AD-7.6考試心得 🔲 最新NSE6_SDW_AD-7.6題庫資源 😰 來自網站▷ www.newdumpspdf.com ◁打開並搜索➥ NSE6_SDW_AD-7.6 🡄免費下載NSE6_SDW_AD-7.6考試心得
- 可靠的Fortinet NSE6_SDW_AD-7.6題庫最新資訊是行業領先材料&免費PDF NSE6_SDW_AD-7.6考題套裝 🔩 免費下載「 NSE6_SDW_AD-7.6 」只需進入☀ www.newdumpspdf.com ️☀️網站NSE6_SDW_AD-7.6測試
- NSE6_SDW_AD-7.6參考資料 🦆 NSE6_SDW_AD-7.6熱門考古題 🍟 NSE6_SDW_AD-7.6測試 ↪ 複製網址➠ www.newdumpspdf.com 🠰打開並搜索⮆ NSE6_SDW_AD-7.6 ⮄免費下載NSE6_SDW_AD-7.6熱門考古題
- 更新的NSE6_SDW_AD-7.6題庫最新資訊和資格考試領導者和最新的NSE6_SDW_AD-7.6:Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator 👄 ✔ www.newdumpspdf.com ️✔️上的➡ NSE6_SDW_AD-7.6 ️⬅️免費下載只需搜尋NSE6_SDW_AD-7.6熱門考古題
- 免費下載NSE6_SDW_AD-7.6題庫最新資訊擁有模擬真實考試環境與場境的軟件VCE版本&高質量的NSE6_SDW_AD-7.6:Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator 🧶 { www.newdumpspdf.com }網站搜索《 NSE6_SDW_AD-7.6 》並免費下載最新NSE6_SDW_AD-7.6題庫資源
- 更新的NSE6_SDW_AD-7.6題庫最新資訊和資格考試領導者和最新的NSE6_SDW_AD-7.6:Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator 👫 在《 www.kaoguti.com 》網站上免費搜索▛ NSE6_SDW_AD-7.6 ▟題庫NSE6_SDW_AD-7.6測試
-
www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, www.stes.tyc.edu.tw, Disposable vapes
此外,這些KaoGuTi NSE6_SDW_AD-7.6考試題庫的部分內容現在是免費的:https://drive.google.com/open?id=1kYMO_YaQQv19hpo-P_lJc3pIfP0pNt8q


 icons at the top
right corner of the subsection.